
Today's Briefing

What happened in security overnight, and what it changes.

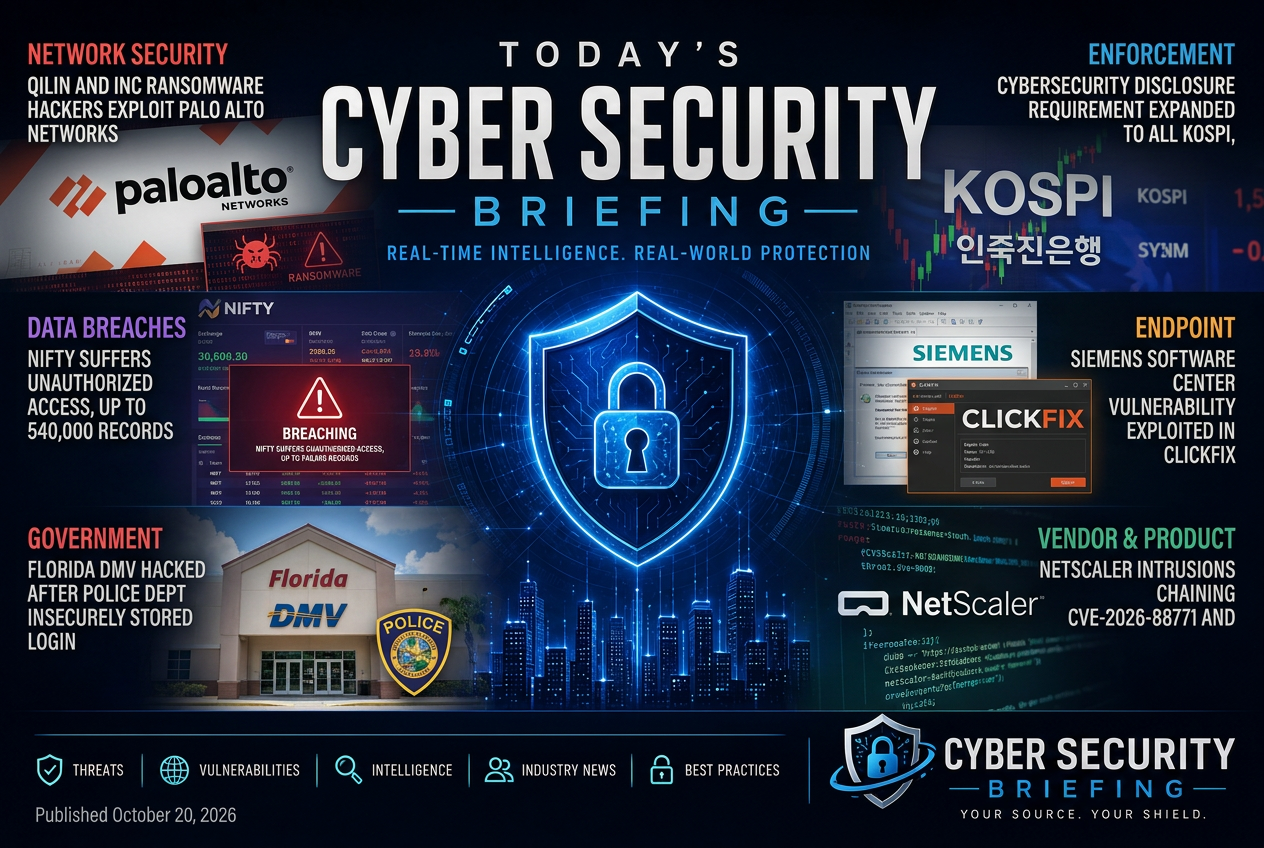
Illustrated summary of the top stories in the Cyber Security Briefing Briefing — October 20, 2026 briefing
Sponsored
Newsletters Automation & Hosting Platform

Tuesday, October 20, 2026

Threat Actors & Campaigns · 1:59 PM

Russian GRU hackers hit NATO shipbuilder, aircraft engine maker, law enforcement agency in espionage campaign

This report says Russian military intelligence targeted a NATO-linked shipbuilder, an aircraft engine maker, and a law enforcement agency in an espionage campaign. The security issue for defenders is exposure across defense and public-sector networks, with a need to tighten monitoring, segmentation, and account protection around likely intelligence targets.
Sponsored
AI-Driven Interactive Websites
Vulnerabilities & Exploitation · 11:08 AM

EU cyber law won’t force fixes for fridge controllers hit in French attack - The Record from Recorded Future News

The piece appears to focus on a gap between EU cyber law and the practical fallout of a French attack on fridge controllers. For defenders, the issue is not just the incident itself but whether the legal framework will actually force remediation on the kinds of connected devices that can become part of an operational disruption.

Get the daily briefing

Join thousands of professionals who start their day with our briefing.

Essential Eight maturity ratings will not carry over to ASD's new cyber framework

Australia's Essential Eight benchmark is being decoupled from ASD's newer cyber framework, which means organisations should not assume past maturity ratings will transfer into the new assessment model. Defenders and compliance teams will need to review their current control evidence and map it to the new framework rather than relying on legacy scores.

News - Health Prime International reports data breach following third-party cyberattack

Health Prime International is reporting a data breach after a third-party cyberattack, which puts the focus on supplier risk rather than only the company’s own controls. For defenders, this is another reminder to map vendor access, understand what data third parties can reach, and verify incident response obligations when an outside provider is breached.
Breaches & incidents · 4:25 AM

NEC Contractor Hit by Cyberattack, Causing System Outages for Multiple Customers and Leak of Files Including Personal Information

A NEC contractor was hit by a cyberattack that disrupted services for multiple customers and exposed files containing personal information. The incident matters because it combines operational outage with potential data exposure, which creates both recovery work and notification obligations for affected organizations.

Monday, October 19, 2026

Nifty Suffers Unauthorized Access, Up to 540,000 Records Potentially Leaked

Nifty says it suffered unauthorized access and that as many as 540,000 records may have been exposed. The operational question for defenders is whether this was limited to one service or reflects broader access-control weakness, because the main impact is exposure of user data and the need for containment, disclosure, and review of account and logging controls.
Sponsored
Ray's Gym Tracker

Get the daily briefing

Join thousands of professionals who start their day with our briefing.

Vulnerabilities & Exploitation · 2:32 PM

Siemens Software Center Vulnerability Exploited in ClickFix Malware Attacks

A vulnerability in Siemens Software Center is being used in ClickFix malware attacks, which makes this a live exploitation issue rather than a routine patch notice. Defenders should treat it as exposure in a widely deployed vendor product and review whether affected systems are reachable, patched, or already showing signs of malicious use.

Florida DMV hacked after police dept insecurely stored login info

Florida residents and former residents appear to have been affected by a DMV data breach that was triggered by insecurely stored login credentials at a police department. The defender lesson is basic but important: weak credential handling at an upstream public agency can expose a different agency’s records and widen the blast radius far beyond the original system.
Breaches & incidents · 12:10 PM

Ticketmaster Confirms Brazil Customer Data Breach as Scope, Timing Remain Unclear

Ticketmaster says customer data in Brazil was breached, but the company has not yet clarified how many people were affected or when the intrusion occurred. For defenders, this is another reminder that large consumer platforms need tight access controls, better logging, and fast breach scoping so they can tell customers and regulators what was exposed.

Suspected cyber incident at CUSI disrupts utility bill payments

A suspected cyber incident is disrupting utility bill payment services at CUSI, which makes this an operational issue for a critical service rather than just a security headline. Defenders and utility operators should treat payment systems as part of the attack surface and review incident response, customer communication, and continuity plans for billing outages.
Sponsored
Newsletters Automation & Hosting Platform

Showing 1–25 of 2164

← PreviousPage 1 of 87Next →

