
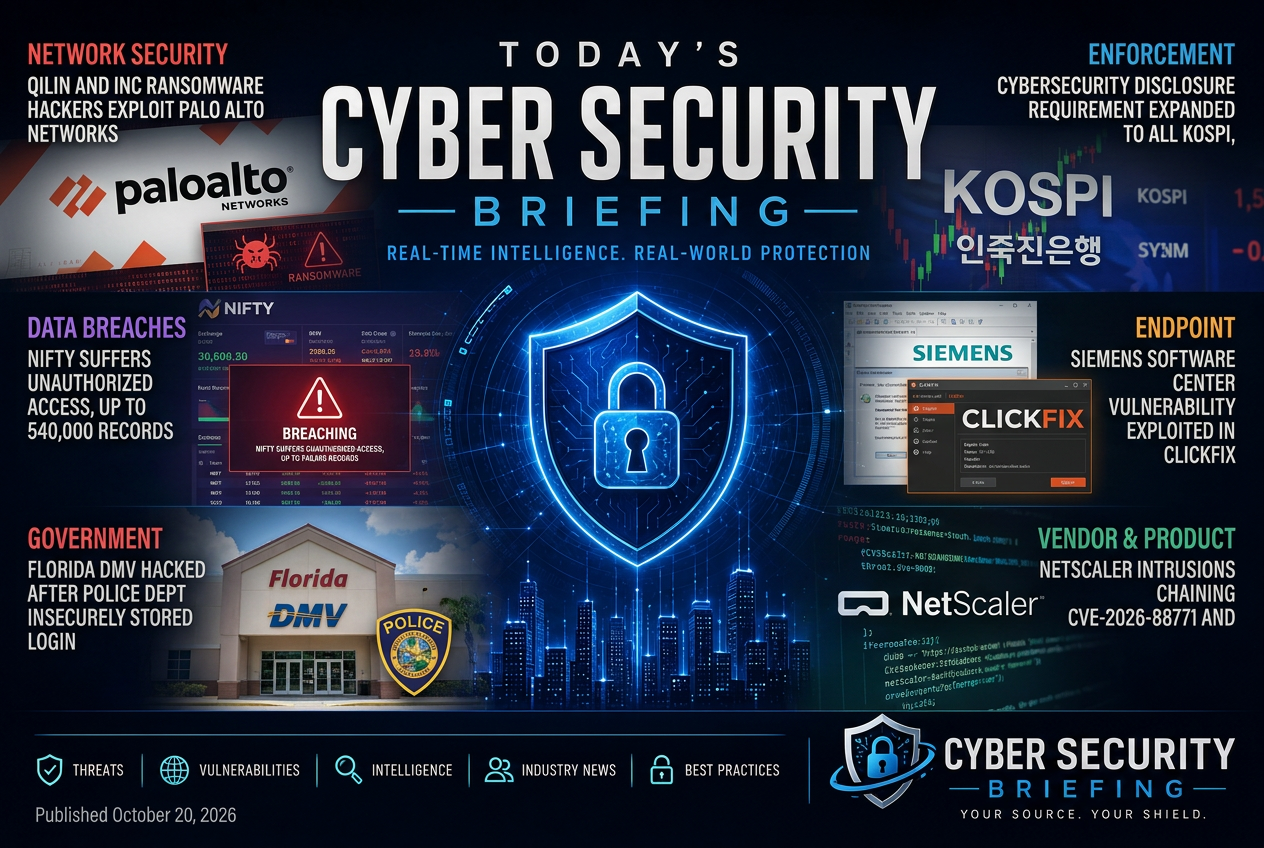
Today's Briefing

What happened in security overnight, and what it changes.

Illustrated summary of the top stories in the Cyber Security Briefing Briefing — October 20, 2026 briefing

Monday, October 19, 2026

Cyber Security Briefing Original
Vulnerabilities & Exploitation · 9:45 AM

WARNING: Template Injection Vulnerability in Adobe Commerce and Magento Open Source Can Be Exploited to Execute Arbitrary Code, Patch Immediately!

CCB Belgium is warning that a template injection flaw in Adobe Commerce and Magento Open Source can be used for arbitrary code execution. Defenders using those platforms should treat this as an application security patching issue and prioritize remediation because exposed ecommerce systems can become an entry point for takeover or further compromise.
Vulnerabilities & Exploitation · 7:14 AM

Linux KVM PwnEscape: the flaw is in IPv4 networking

This is about a Linux KVM escape risk tied to IPv4 networking, so the security concern is a virtualization boundary being crossed through network handling. For defenders, the immediate questions are whether they run affected Linux KVM hosts and whether guest-to-host isolation depends on the exposed networking path.
Regulation & Enforcement · 7:00 AM

Data Breach at Japanese Karaoke System Maker Daiichi Kosho Affects More Than 8.7 Million People

Daiichi Kosho has disclosed a breach tied to its karaoke systems business, with a very large number of people affected. For defenders, the key issues are exposure of customer or user data, the scope of systems involved, and whether the incident points to weaknesses in identity controls, segmented access, or vendor-managed infrastructure.
Sponsored
Newsletters Automation & Hosting Platform

Data Breach at Hankyu Hanshin Department Store Common ID System Affects Nearly All 1.26 Million Members

Hankyu Hanshin Department Store says a breach in its common ID system affected nearly all of its 1.26 million members. The main defender takeaway is that a shared identity platform can turn a single compromise into a large-scale exposure of customer accounts and records, so access controls, monitoring, and blast-radius limits matter here.
Breaches & incidents · 12:00 AM

Ashikaga City Crematorium Reservation System Hacked, ~8,800 User Records Potentially Leaked

A municipal crematorium reservation system in Ashikaga City was hacked, and the incident may have exposed personal records for thousands of users. For defenders, this is a public-sector data breach tied to a local service that handles sensitive personal information, so the focus is on access control, incident response, and notification obligations.

Get the daily briefing

Join thousands of professionals who start their day with our briefing.

Sunday, October 18, 2026

Vulnerabilities & Exploitation · 7:14 AM

CDU Heilbronn Email Account Compromised: Phishing Attack Targets German Government and Security Officials

A German political email account was compromised in a phishing attack, which puts government and security officials at risk of further impersonation or follow-on targeting. The immediate defender concern is account takeover, message trust, and whether the compromise was used to reach other official recipients.

ConnectWise Credential Compromise Enables Unauthorized Access to 173 Microsoft 365 Tenants: Cybersecurity Incident Analysis

A credential compromise at ConnectWise led to unauthorized access across a large set of Microsoft 365 tenants. For defenders, the issue is identity and access exposure in a managed-service supply chain, which means tenant review, credential reset, and session invalidation matter more than treating this as a single-vendor incident.

Saturday, October 17, 2026

Sponsored
Newsletters Automation & Hosting Platform

SBI, Subsidiaries’ Customer Data Allegedly On Dark Web: 3.75 Lakh Records, 2,722 Documents Claimed In Data

This alleges customer data from SBI and its subsidiaries has been posted on the dark web, which is an exposure issue for a large financial institution and its customers. The immediate concern for defenders is verification, containment, and determining whether the claimed records came from a breach, a third party, or reused credentials.
Vulnerabilities & Exploitation · 10:44 AM

CISA Issues Federal Directive on Windows Shell Zero-Day CVE-2026-96951 Following Active Exploitation

CISA has issued a federal directive after active exploitation of a Windows Shell zero-day, which puts federal Windows fleets under immediate patching and mitigation pressure. For defenders, the issue is not just the flaw itself but the obligation to verify exposure, prioritize remediation, and watch for signs of exploitation already underway.

Get the daily briefing

Join thousands of professionals who start their day with our briefing.

Breaches & incidents · 6:08 AM

BAE Systems Cyber Incident Takes US Bankruptcy Noticing Center Offline for a Week

A cyber incident at BAE Systems knocked the US Bankruptcy Noticing Center offline for a week, which points to operational disruption in a government-adjacent service rather than a simple disclosure. Defenders should read this as an availability and continuity issue, with the main questions being resilience, recovery time, and whether any sensitive court-related data or workflow was exposed.

Friday, October 16, 2026

Sponsored
Ray's Gym Tracker

Showing 26–50 of 2164
