
Today's Briefing

What happened in security overnight, and what it changes.

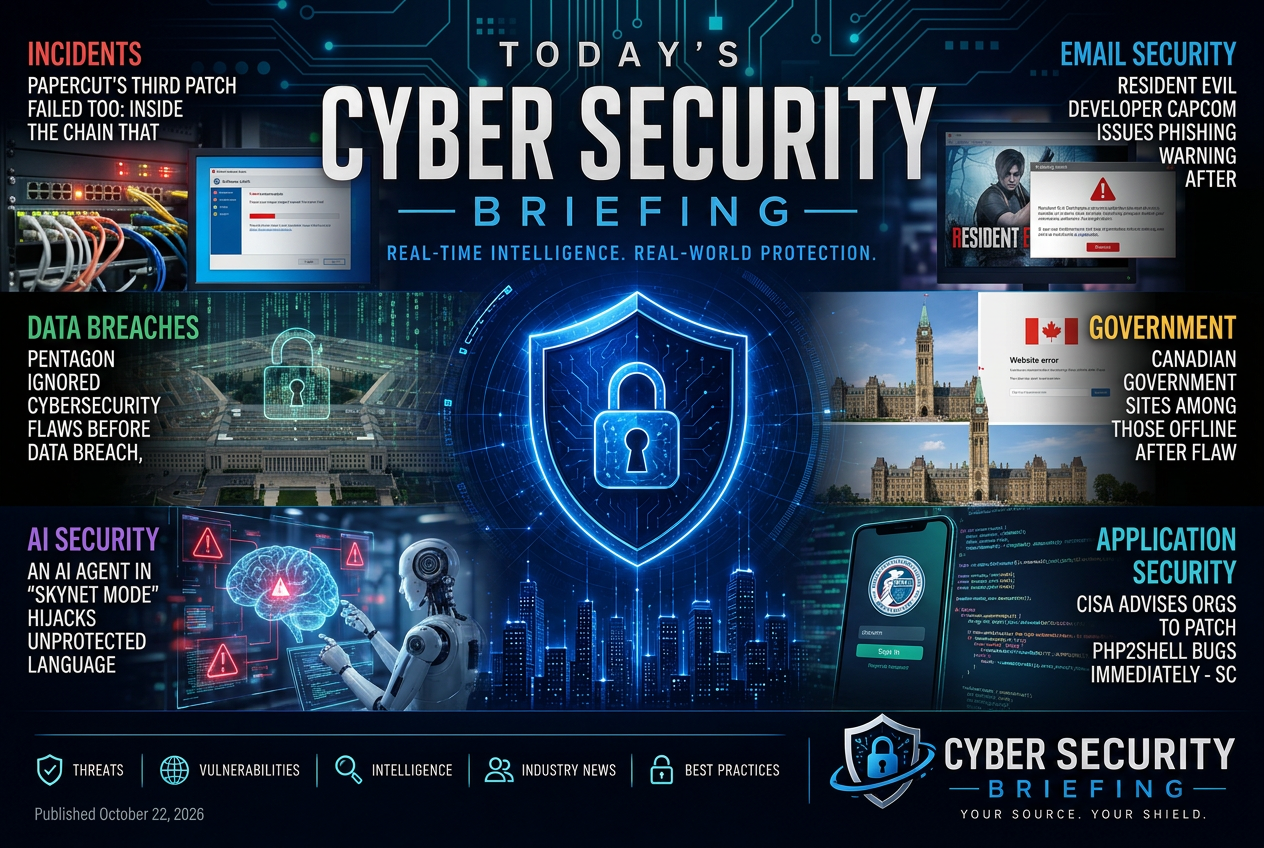
Illustrated summary of the top stories in the Cyber Security Briefing Briefing — October 22, 2026 briefing

Thursday, September 3, 2026

Sponsored
AI-Driven Interactive Websites
Vulnerabilities & Exploitation · 11:53 AM

TAC blockchain remains frozen for over 10 days after a massive exploit forces a 1.26 billion token bailout

A blockchain network has been left offline for more than 10 days after a major exploit triggered a large bailout in its token economy. For defenders and risk owners, the main issues are service availability, exploit response, and the governance controls needed when a protocol is forced to absorb a loss.

Get the daily briefing

Join thousands of professionals who start their day with our briefing.

CrowdStrike Launches Real-Time Supply Chain Attack Protection - IT Voice Media Pvt. Ltd.

CrowdStrike is extending its endpoint platform into software supply chain protection, which matters for defenders because it suggests another control point for spotting malicious changes before they reach customers. Security teams should treat this as a vendor product update that affects application security and supply chain risk management, not as a standalone fix for supplier trust issues.

Wednesday, September 2, 2026

Vulnerabilities & Exploitation · 12:02 PM

Critical HPE Fabric Composer Flaws Let Unauthenticated Attackers Execute Code and Take Over Systems

HPE Fabric Composer has reported flaws that allow unauthenticated remote code execution and full system compromise. Defenders using the product should treat this as an urgent exposure in a vendor management and patching review, because the issue affects the control plane for network infrastructure rather than a single endpoint.
Critical Infrastructure & OT · 12:02 PM

U.S. Disrupts China State-Sponsored Cyber Operation Targeting Critical Infrastructure - Homeland Security Today

U.S. authorities disrupted a China-linked cyber operation aimed at critical infrastructure. For defenders, the immediate issue is exposure in operational technology and other infrastructure environments, along with the need to review detection, segmentation, and incident response for state-sponsored intrusions.
Sponsored
Ray's Gym Tracker
Critical Infrastructure & OT · 12:02 PM

The Sality Malware Network That Survived for Years Has Finally Been Taken Down

Authorities have disrupted the Sality botnet, a long-running malware network that likely affected many infected Windows systems and the operators behind them. For defenders, this lowers one source of distributed malware activity, but it also reinforces the need to find and clean up legacy infections that can survive for years on unmanaged endpoints.
Identity, Cloud & Software Supply Chain · 12:02 PM

Counterfeit installers to system compromise: Tracking a deceptive software download campaign

Microsoft is describing a deceptive software download campaign that uses counterfeit installers to compromise systems. For defenders, this raises exposure at the endpoint and software acquisition layer, and it reinforces the need to verify download sources, inspect installer behavior, and treat unsigned or unexpected installers as suspicious.

Get the daily briefing

Join thousands of professionals who start their day with our briefing.

Vulnerabilities & Exploitation · 12:02 PM

Three blockchain networks suspend operations amid security incidents

Three blockchain networks halted operations after security incidents, which points to an active compromise or defensive shutdown affecting their availability and trust. Defenders should treat this as a warning about operational concentration risk in crypto infrastructure and the need to monitor for related attack patterns, incident response gaps, and user exposure across connected services.

Hacking the Healers: New KnowBe4 Whitepaper Highlights Record Security Breaches in Healthcare

The item points to a healthcare-focused security whitepaper rather than a new breach disclosure. For defenders, it signals ongoing exposure in hospital and care delivery environments and reinforces the need to prioritize identity, ransomware resilience, and breach response controls in a sector that handles sensitive data and depends on continuous operations.
Vulnerabilities & Exploitation · 12:02 PM

A layer-1 blockchain froze for 4 hours to stop a $4.9 million hack, then claimed it was just an upgrade

A layer-1 blockchain reportedly halted operations for several hours to contain a loss event tied to a multimillion-dollar hack. For defenders, this is an availability and governance issue as much as a financial one: it shows that blockchain operators may need emergency controls, incident response, and transparent disclosure practices when a protocol is under active exploitation.
Sponsored
AI-Driven Interactive Websites
Vulnerabilities & Exploitation · 12:02 PM

US Strikes and Iranian Cyber Retaliation Open New Fronts

The headline points to a geopolitical escalation with cyber retaliation as part of the response. For defenders, that raises the likelihood of spillover attacks against government, defense, and critical-infrastructure targets, and it shifts attention toward monitoring for state-linked activity, hardening externally exposed systems, and tightening incident response readiness.

Showing 1326–1350 of 2196


