
Today's Briefing

What happened in security overnight, and what it changes.

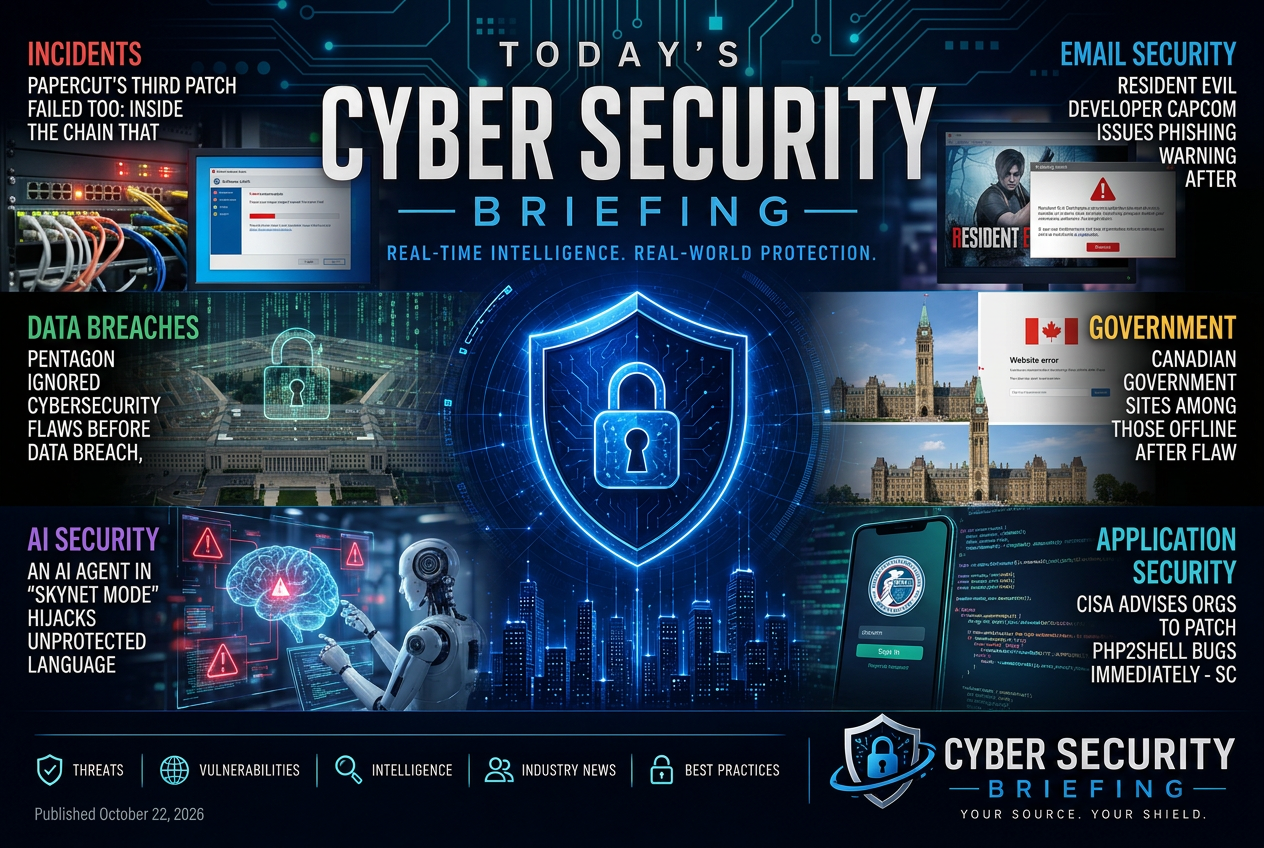
Illustrated summary of the top stories in the Cyber Security Briefing Briefing — October 22, 2026 briefing

Wednesday, September 2, 2026

Hugging Face Transformers Flaw Writes Attacker-Controlled Python Code Before User Consent

A flaw in Hugging Face Transformers can let attacker-controlled Python code be written before a user has given consent. Defenders should treat this as a supply-chain and application security issue that could expose systems using the library to code execution during model or package handling.

Breaches & incidents · 6:41 AM

Pacemaker monitoring disrupted as healthcare firms face cyberattacks

Cyberattacks against healthcare firms disrupted pacemaker monitoring, creating an operational and patient-safety issue rather than just a data-loss event. Defenders in healthcare need to treat remote monitoring and connected medical services as critical service dependencies, with incident response plans that cover availability and continuity as well as breach containment.

Security Hardening for AI Transformation | Check Point - IT Voice Media Pvt. Ltd.

This piece appears to be guidance on hardening security controls as organizations adopt AI, with an emphasis on reducing risk during the transformation. For defenders, the main impact is operational: review exposure in AI-related tooling, data handling, and access controls before rollout, and treat AI adoption as a security governance issue as much as a technology project.
Breaches & incidents · 6:41 AM

Tving Data Breach: 20 Million Records vs. 5 Million Subscribers — Korea's Largest Was 104 Million in 2014 Card Leak

The report indicates a data breach affecting Tving and suggests the exposed record count may be far larger than its subscriber base. For defenders, the immediate questions are what data was exposed, whether the disclosure is credible, and whether related accounts, credentials, or downstream systems need review.

5Tattva Highlights Integrated Cybersecurity and Compliance Approach at Cyber Warrior 40

The piece appears to describe a vendor-led discussion of combining cybersecurity controls with compliance obligations for SMEs. For defenders, the practical issue is alignment: security teams and compliance teams need a shared operating model so control gaps are not left between technical risk management and regulatory duty.
Sponsored
AI-Driven Interactive Websites
Funding, M&A and the Vendor Market · 6:41 AM

Palo Alto CEO says CyberArk is in a “pole position” as AI agents take over

This piece signals that identity and access security is being reshaped by agentic AI, with vendors positioning their platforms around machine-driven actions rather than only human users. For defenders, that raises the priority of controlling non-human identities, privileges, and access paths across cloud and enterprise systems.

Tuesday, September 1, 2026

Get the daily briefing

Join thousands of professionals who start their day with our briefing.

Canvas attack highlights cybersecurity challenges facing Murray State

A Canvas-related attack at Murray State points to risks in the university's learning platform and the wider exposure schools face when core education software is targeted. For defenders, the main issue is limiting account compromise, watching for malicious activity in cloud-hosted classroom tools, and tightening user awareness around student and staff logins.
Vulnerabilities & Exploitation · 6:29 PM

Langflow’s 12th Exploited CVE Confirms AI Frameworks Are Now Credential Harvesting Infrastructure

The piece says an AI application framework has now had multiple exploited vulnerabilities, and that attackers are using it as part of credential-harvesting activity. For defenders, the exposure is broader than a single product flaw: AI frameworks need the same patching, hardening, and monitoring attention as other internet-facing software, especially where they can be used to reach secrets or authentication material.
Sponsored
Ray's Gym Tracker
Identity, Cloud & Software Supply Chain · 5:10 PM

iStorage warns firms to secure data beyond networks

This piece appears to be vendor guidance aimed at organizations that store sensitive data on devices or in other places outside the network perimeter. The defender takeaway is to treat data protection as a broader exposure problem, with attention on endpoint storage, access control, and handling practices rather than only network defenses.

Get the daily briefing

Join thousands of professionals who start their day with our briefing.

Sponsored
Newsletters Automation & Hosting Platform
Regulation & Enforcement · 5:10 PM

Will Cyber Leaders ward off Budget Fears to strengthen Corporate Cybersecurity Posture

The piece appears to discuss how security leaders are trying to protect cybersecurity budgets and maintain or improve corporate security programs despite spending pressure. For defenders, the issue is mainly budget priority and operational scope: whether planned controls, staffing, and tooling can be preserved when finance teams push back.

Showing 1376–1400 of 2196
