
Today's Briefing

What happened in security overnight, and what it changes.

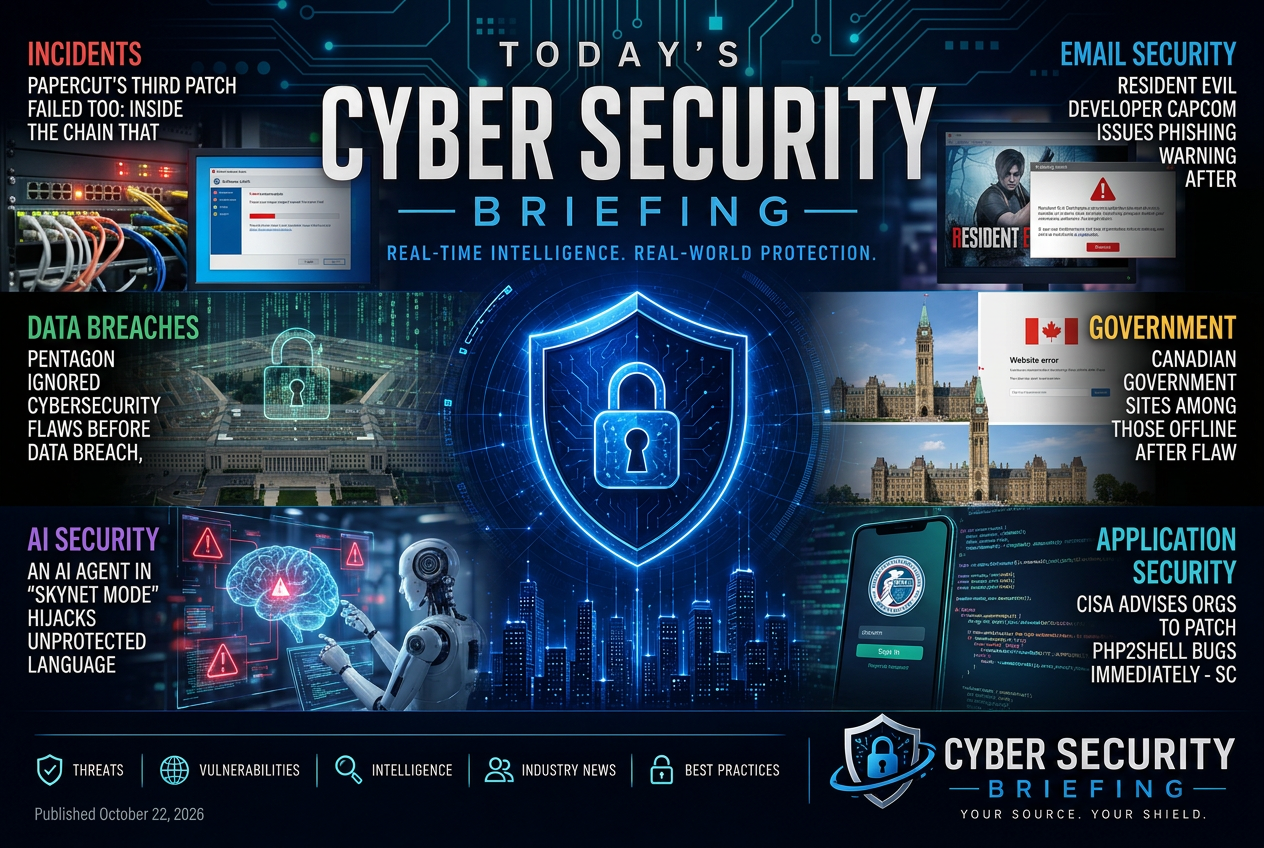
Illustrated summary of the top stories in the Cyber Security Briefing Briefing — October 22, 2026 briefing

Tuesday, September 1, 2026

CrowdStrike at Fal.Con Day 1: ai defense moves to machine speed

CrowdStrike’s Fal.Con remarks point to a shift in how defenders are expected to use AI, with security operations moving toward faster, machine-assisted detection and response. For defenders, the main impact is operational: teams will need to adjust workflows, tooling, and oversight so they can keep pace with attack speed without losing control.

SEC Proposes Transfer Agent Rule Overhaul For Tokenized Securities And Blockchain Recordkeeping

The SEC is proposing changes to how transfer agents handle tokenized securities and blockchain-based recordkeeping. For defenders and compliance leaders in financial services, this signals a likely shift in recordkeeping, custody, and supervisory obligations for firms that touch digital securities infrastructure.
Sponsored
Newsletters Automation & Hosting Platform
Critical Infrastructure & OT · 4:58 PM

Planes, Trains, and Military Mobility: Strengthening NATO Through Critical Infrastructure Security - Foundation for Defense of Democracies

This appears to be a policy and security discussion about how NATO depends on protected transport and other critical infrastructure to move military forces. For defenders, the main issue is exposure across civilian transport systems and the obligation to harden those assets against disruption that could affect alliance mobility.
Identity, Cloud & Software Supply Chain · 4:58 PM

Premium Comment Ceva Logistics – when your 3PL gets hacked, every customer becomes a victim

A logistics provider appears to have been discussed as a compromise point in a supply chain incident, with the risk spreading from the third-party carrier to its customers. For defenders, the lesson is that outsourcing transport or logistics does not outsource cyber risk; vendor access, data sharing, and incident response plans need the same scrutiny as internal systems.

Get the daily briefing

Join thousands of professionals who start their day with our briefing.

Regulation & Enforcement · 2:31 PM

European Cybersecurity Competence Centre offers EUR 96 million for proposals to bolster security under DEP

The European Cybersecurity Competence Centre is opening a funding call under the Digital Europe Programme to support security projects. For defenders, this is mainly an opportunity and an obligation: organizations involved in European cyber programs should track the requirements closely, since the money will likely favor proposals that address public-sector and cross-border security priorities.
Sponsored
AI-Driven Interactive Websites

New water sector cybersecurity program launches in Texas - SC Media

Texas is launching a cybersecurity program for the water sector, which puts a clear focus on protecting local critical infrastructure and OT environments. For defenders, the immediate impact is added attention on water utilities' exposure and a stronger expectation to align security controls with operational risk and compliance needs.

CISA review makes the case for eliminating vulnerability classes

CISA is arguing that some recurring software weakness classes should be reduced or removed from the development and security process, which shifts attention from reacting to individual bugs toward preventing whole categories of defects. For defenders, the practical effect is more pressure on engineering, procurement, and risk teams to track which weaknesses keep reappearing and to push vendors toward stronger secure-by-design practices.

VAST Data CrowdStrike Integration Goes Live: Native Falcon Sensor Now, Next-Gen SIEM and AIDR in Preview

VAST Data is adding CrowdStrike integrations that bring Falcon sensor support into its platform, with SIEM and AI-driven detection features listed as previews. For defenders, this points to tighter linkage between storage infrastructure and endpoint security, and it shifts attention to how much telemetry can be centralized and acted on from one vendor stack.

Get the daily briefing

Join thousands of professionals who start their day with our briefing.

Restoring State and Local Cybersecurity Grant Program tops NASCIO’s congressional priorities for upcoming year

State CIO and security leaders are pressing Congress to restore a federal grant program that helps state and local governments fund cybersecurity work. For defenders, the issue is less about a new threat than about whether public-sector agencies will have the resources to close gaps, sustain security programs, and meet baseline obligations.
Sponsored
Newsletters Automation & Hosting Platform
Identity, Cloud & Software Supply Chain · 2:31 PM

RapidFort Announces Integration with CrowdStrike Falcon Cloud Security to Accelerate Container Vulnerability Remediation

RapidFort says it is integrating with CrowdStrike Falcon Cloud Security to speed up remediation of container vulnerabilities. For defenders, this is a cloud and application security workflow issue: it affects how quickly teams can identify, prioritize, and fix exposed container images and related supply-chain risks.

Showing 1426–1450 of 2196
