
Today's Briefing

What happened in security overnight, and what it changes.

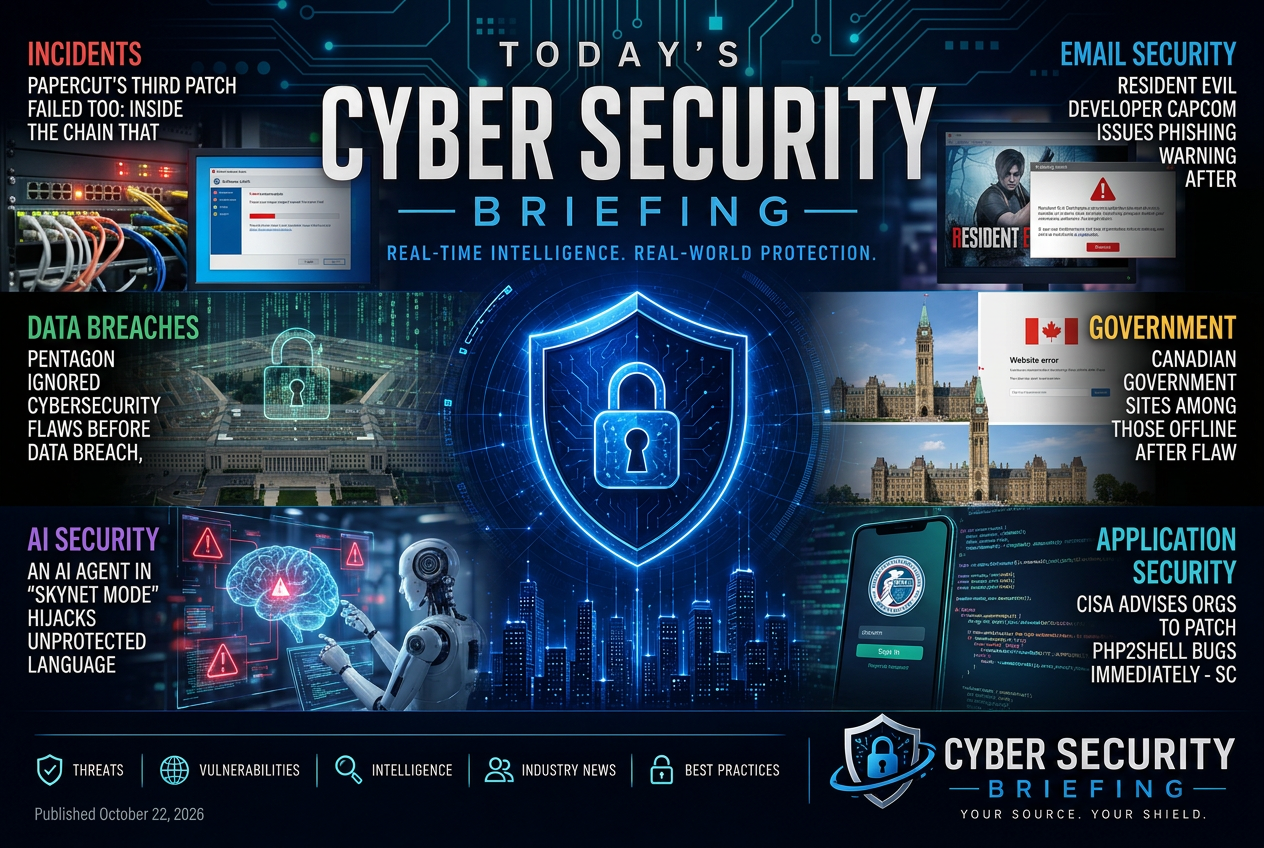
Illustrated summary of the top stories in the Cyber Security Briefing Briefing — October 22, 2026 briefing

Monday, August 31, 2026

Identity, Cloud & Software Supply Chain · 1:13 PM

LastPass Expands SaaS and Identity Security Tools as AI Threats Rise

LastPass is expanding tools aimed at SaaS and identity security, which matters because identity controls are a primary target when attackers use automation and AI. For defenders, this is mainly an exposure and priority issue: review how well identity governance, SaaS access controls, and credential protections are covered by existing programs.
Breaches & incidents · 1:13 PM

Pharmaceutical giant McKesson warns of 'service degradation' following cyberattack - The Record from Recorded Future News

McKesson says a cyberattack is affecting service availability, which puts operational continuity ahead of any confirmed disclosure at this stage. For defenders in healthcare and adjacent supply chains, the immediate concern is resilience of business-critical systems and the downstream impact on medication distribution and customer service.
Sponsored
Ray's Gym Tracker
Identity, Cloud & Software Supply Chain · 1:13 PM

LastPass Advances Secure Access to Strengthen Identity Security in the Age of AI

LastPass is positioning a secure access update as part of broader identity security efforts, with an emphasis on AI-era risk. For defenders, the main question is whether the product reduces exposure around credential use and access control, and whether it changes procurement or configuration obligations for organizations already using it.

Get the daily briefing

Join thousands of professionals who start their day with our briefing.

Critical Infrastructure & OT · 1:13 PM

Why Water Security Is the Next Frontier of Cyber Warfare, According to Expert

The piece frames water systems as a cyber target and a public-safety issue, which raises the stakes for utilities, local governments, and the operators that support them. For defenders, the main concern is exposure in OT and critical-infrastructure environments where disruption can affect service continuity and physical outcomes, so monitoring, segmentation, and incident response planning matter.
Funding, M&A and the Vendor Market · 1:13 PM

Switzerland Proceeds With Transparency Register Despite Hack Fears - Global Banking & Finance Review

Switzerland is moving ahead with a transparency register even though there are concerns that it could create a target for hackers. For defenders, the issue is increased exposure around sensitive ownership and financial data, along with a compliance obligation to secure the register and the systems that support it.
Critical Infrastructure & OT · 8:50 AM

Top Cybersecurity Startups In China

This is a list-style piece about cybersecurity startups in China. For defenders, it is mainly a market watch item: it can help identify where new security tooling and investment are emerging, but it does not describe a specific vulnerability, incident, or policy change.
Sponsored
Newsletters Automation & Hosting Platform
AI Security · 8:50 AM

Anthropic Study Finds AI Can Fix Its Own Safety Flaws

The story points to research on whether AI systems can detect and correct their own safety weaknesses. For defenders, that raises a governance issue: teams will need to validate claims about self-improving safeguards before trusting them in production, and to understand how much human review remains necessary.
Critical Infrastructure & OT · 8:50 AM

The AI Kill Switch Act is repeating the Clipper Chip’s mistakes

The piece argues that the proposed AI Kill Switch Act would repeat past regulatory mistakes by treating a security control as if it were a simple technical fix. For defenders, the issue is not a new attack or breach, but the risk that policy built on the wrong model could distort AI security requirements and create compliance obligations that do not improve actual protection.

Get the daily briefing

Join thousands of professionals who start their day with our briefing.

Threat Actors & Campaigns · 8:50 AM

ValleyRAT is spreading disguised as adware

ValleyRAT is being distributed under the cover of adware, which means defenders should treat a seemingly low-risk installer or bundle as a potential malware delivery path. The immediate concern is endpoint exposure and detection, especially where users can run unsigned or bundled software without strong controls.
Sponsored
AI-Driven Interactive Websites

Building trustworthy agentic AI: How security concerns have changed in 2026

The piece appears to discuss how security teams should reassess controls, governance, and risk management as agentic AI systems become part of normal operations. For defenders, the main issue is exposure from autonomous decision-making and the obligation to build stronger oversight, access control, and validation around AI-enabled workflows.

Showing 1526–1550 of 2200

