
Today's Briefing

What happened in security overnight, and what it changes.

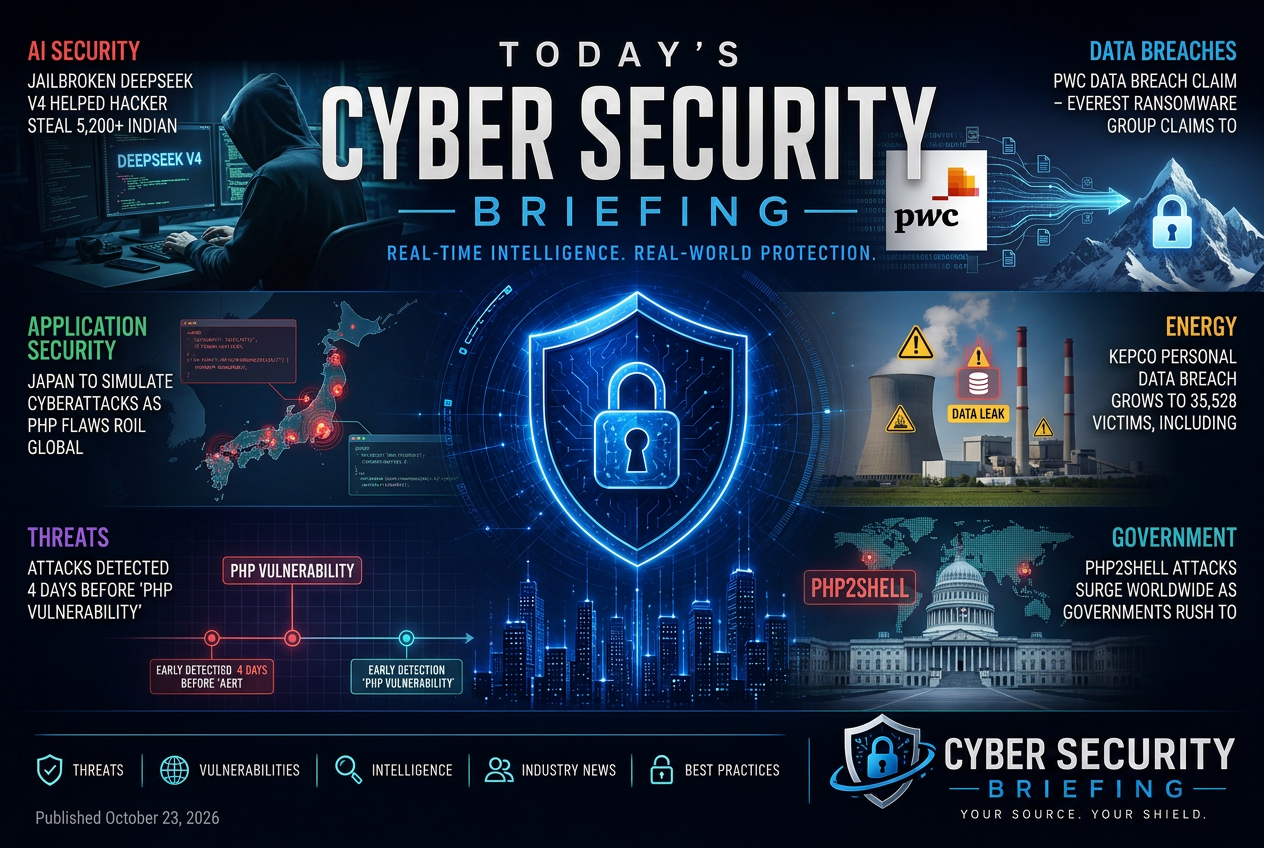
Illustrated summary of the top stories in the Cyber Security Briefing Briefing — October 23, 2026 briefing

Sunday, August 23, 2026

Identity, Cloud & Software Supply Chain · 11:37 AM

AWS Security: 760+ Leaked Keys With Full Admin Rights Still Active

Leaked AWS access keys that still had administrative privileges create direct risk to cloud environments, including unauthorized access, persistence, and lateral movement. For defenders, the immediate priority is key rotation, credential inventory, and review of any systems exposed through those accounts, especially if the keys were published or reused in third-party workflows.
Identity, Cloud & Software Supply Chain · 11:37 AM

Malware in Rust Crates With 245M Downloads: North Korea Behind the crates.io Supply Chain Attack

This reports a supply chain compromise in Rust crates on crates.io, where malware was embedded in packages that had reached wide distribution. For defenders, the immediate exposure is dependency risk in software builds and the obligation to review Rust package sources, pinned versions, and internal artifact controls.
Sponsored
Newsletters Automation & Hosting Platform
Vulnerabilities & Exploitation · 11:37 AM

Coldcard now requires 65 key presses after seed exploit, while exposed funds still must move

Coldcard has changed its signing process after a seed-related exploit, which raises the bar for physical approval of transactions but also signals that some wallets or funds may remain exposed until users act. For defenders, the main issue is exposure management: identify affected devices, validate whether seed material or funds could be at risk, and move assets or rotate keys where needed.

Get the daily briefing

Join thousands of professionals who start their day with our briefing.

Sponsored
Newsletters Automation & Hosting Platform

Get the daily briefing

Join thousands of professionals who start their day with our briefing.

AI Security · 11:37 AM

Medusa’s 500 Victims Point to a Bigger Shift in Ransomware

Medusa’s reported victim count points to continued ransomware pressure on organizations and to the operational model behind modern extortion campaigns. For defenders, the main takeaway is exposure to broad, recurring intrusion and encryption risk, with priority on detection, resilience, and incident-response readiness rather than assuming this is a one-off event.
Regulation & Enforcement · 11:37 AM

Indian cybersecurity startups chase international deals up to 100x larger

Indian cybersecurity startups are looking beyond domestic customers and targeting larger international contracts. For defenders, that signals more vendor competition and potentially broader access to security tooling, but it also raises procurement and third-party risk questions if buyers rely on younger firms expanding into unfamiliar markets.
Sponsored
AI-Driven Interactive Websites

Showing 2176–2200 of 2209
