F5 Patches Actively Exploited BIG-IP APM Flaw; watchTowr Traces It to an Unchecked OAuth Header
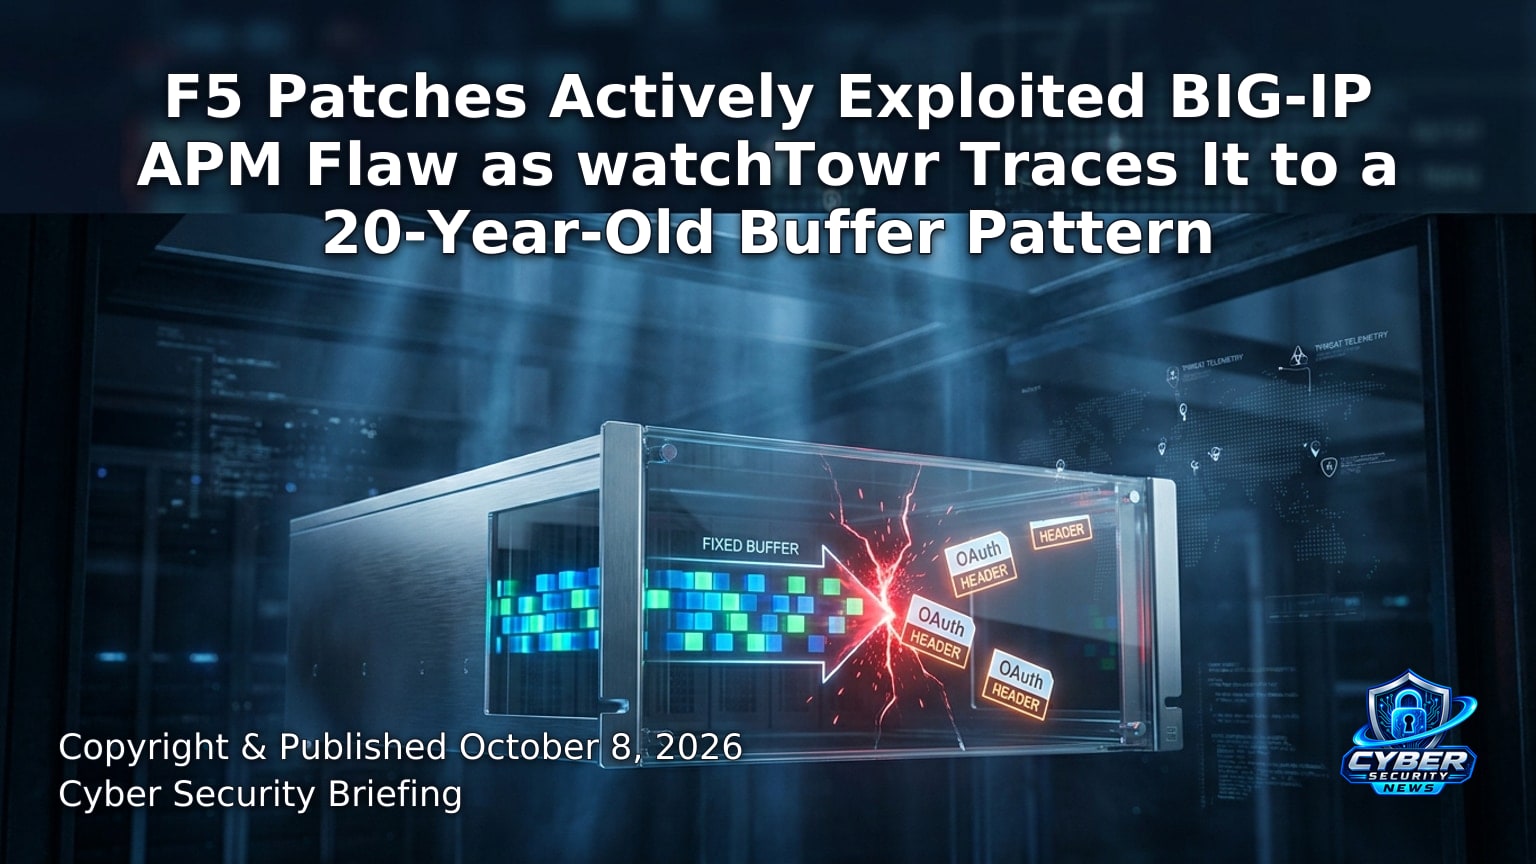
Original illustration created for Cyber Security Briefing.

F5 Patches Actively Exploited BIG-IP APM Flaw; watchTowr Traces It to an Unchecked OAuth Header
F5 disclosed a critical heap-based buffer overflow in BIG-IP Access Policy Manager on September 22, 2026, and confirmed in the same advisory that the vulnerability, tracked as CVE-2026-94127, "has been exploited" in the wild. CISA added the flaw to its Known Exploited Vulnerabilities catalog the same day, triggering remediation deadlines for federal agencies under Binding Operational Directive 26-04.
The bug carries a CVSS v3.1 score of 9.8, according to Rapid7's analysis, and requires no authentication to trigger.
California's Cal-CSIC went further than the vendor on impact. Its September 24 advisory states that successful exploitation grants code execution with "elevated privileges on the underlying operating system" — not merely within the APM process. F5's own advisory, K000162605, confirms remote code execution but does not characterize the privilege level attackers land at post-exploitation; Rapid7's writeup is likewise silent on that point. The distinction matters for anyone running APM as an edge authentication gateway, since OS-level access changes what a compromised appliance can reach next.
A fixed buffer, an unchecked header
watchTowr Labs traced the flaw to the OAuth handler's processing of the Authorization header. watchTowr's writeup is blunt about where that leaves BIG-IP, criticizing the persistence of "legacy" primitives of this kind in critical network infrastructure — a missing bounds check on attacker-controlled input, copied into a fixed-size buffer, with no authentication required to reach it.
Where the exposure actually sits
Rapid7's analysis draws a distinction CISOs should not skip past. The flaw lives in the BIG-IP data plane, not the control plane, and it only applies when a virtual server combines an APM access policy with an OAuth profile configured as an Authorization Server. Rapid7 calls that configuration non-default but "common" wherever BIG-IP serves as an authentication gateway at the network edge — the one place none of the material reviewed here puts a number on: no vendor or advisory source gives a count or share of deployments actually running APM with an OAuth Authorization Server profile.
Picus Security's September 24 breakdown adds a separate point: because the issue sits in traffic handling rather than the management interface, standard management-plane segmentation does nothing to reduce exposure. An organization that has locked down administrative access to BIG-IP but still exposes an APM/OAuth virtual server to the internet remains exposed.
Exploitation evidence and what to look for in logs
CERT-EU's September 22 advisory treats the exploitation as already underway at the time of disclosure and tells administrators to preserve forensic evidence before patching, though it does not specify when exploitation activity began. The agency lists specific indicators: repeated OAuth authentication failures recorded in /var/log/apm, and TMM process crashes registering as SIGABRT. CERT-EU singles out one log pattern in particular — entries reading "Request UserInfo from Source ID (null) IP
SentinelOne's September 24 guide adds detection targets on the process side: unexpected crashes, core dumps, or restarts of the APM data plane process, tmm. Field Effect's summary frames the mechanism the same way administrators will see it in incident tooling: the attacker sends crafted traffic that corrupts memory during request handling, with no credentials and no user interaction required.
What to do this week
The remediation sequence that emerges from these advisories is narrow and specific, not a general BIG-IP hardening exercise.
- Inventory every virtual server for the APM-plus-OAuth-Authorization-Server combination flagged above. Everything else is not exposed to this CVE.
- Apply F5's hotfix per K000162605. Where patching has to wait, Cal-CSIC recommends a vendor-validated mitigation iRule as a stopgap; none of the advisories reviewed describe what that iRule costs in throughput or whether applying the hotfix itself requires a TMM restart or failover.
- Pull /var/log/apm for the CERT-EU indicators — repeated OAuth failures and the invalid_token/Source ID (null) pattern — before patching, so forensic evidence survives the fix.
- Alert on tmm restarts and SIGABRT crashes. CERT-EU's September 22 advisory does not give a start date for exploitation activity, so treat any unexplained APM data-plane crash on record as worth reviewing.
Federal agencies face a BOD 26-04 deadline tied to the KEV listing; state, local and private-sector operators do not have that forcing function, which is the gap Cal-CSIC's own advisory was written to close.
CERT-EU, Cal-CSIC and CISA all treated this one the same way — as already exploited, not merely exploitable — which should settle any argument about whether this week's patch cycle can wait.
Links Verified at Time of Publish.
Sources
This article was reported from the following sources.
- K000162605: BIG-IP APM vulnerability CVE-2026-94127 — MyF5 (F5, Inc.), 2026-09-22
- Is This A Joke? In The Auth Header? (F5 BIG-IP UnAuth Heap-Overflow to RCE CVE-2026-94127) — watchTowr Labs, 2026-09-23
- CISA Adds Four Known Exploited Vulnerabilities to Catalog — Cybersecurity and Infrastructure Security Agency (CISA), 2026-09-22
- CYBER ADVISORY - Critical Buffer Overflow Vulnerability Affecting F5 BIG-IP Access Policy Manager — California Governor's Office of Emergency Services (Cal-CSIC), 2026-09-24
- CVE-2026-94127: Critical Unauthenticated RCE in F5 BIG-IP APM — Rapid7, 2026-09-23
- Critical Vulnerability in F5 BIG-IP APM — CERT-EU, 2026-09-22
- CVE-2026-94127: F5 BIG-IP APM OAuth Server RCE Flaw — SentinelOne, 2026-09-24
- F5 BIG-IP Heap Overflow Lets Attackers Skip Authentication for Code Execution — WebPulse Newsroom, 2026-09-27
- F5 Fixes Actively Exploited BIG-IP APM Vulnerability — Field Effect, 2026-09-23
- CVE-2026-94127 Explained: F5 BIG-IP APM Heap Overflow Attack — Picus Security, 2026-09-24