
Cyber Security Briefing Briefing — September 8, 2026
Tuesday, September 8, 2026
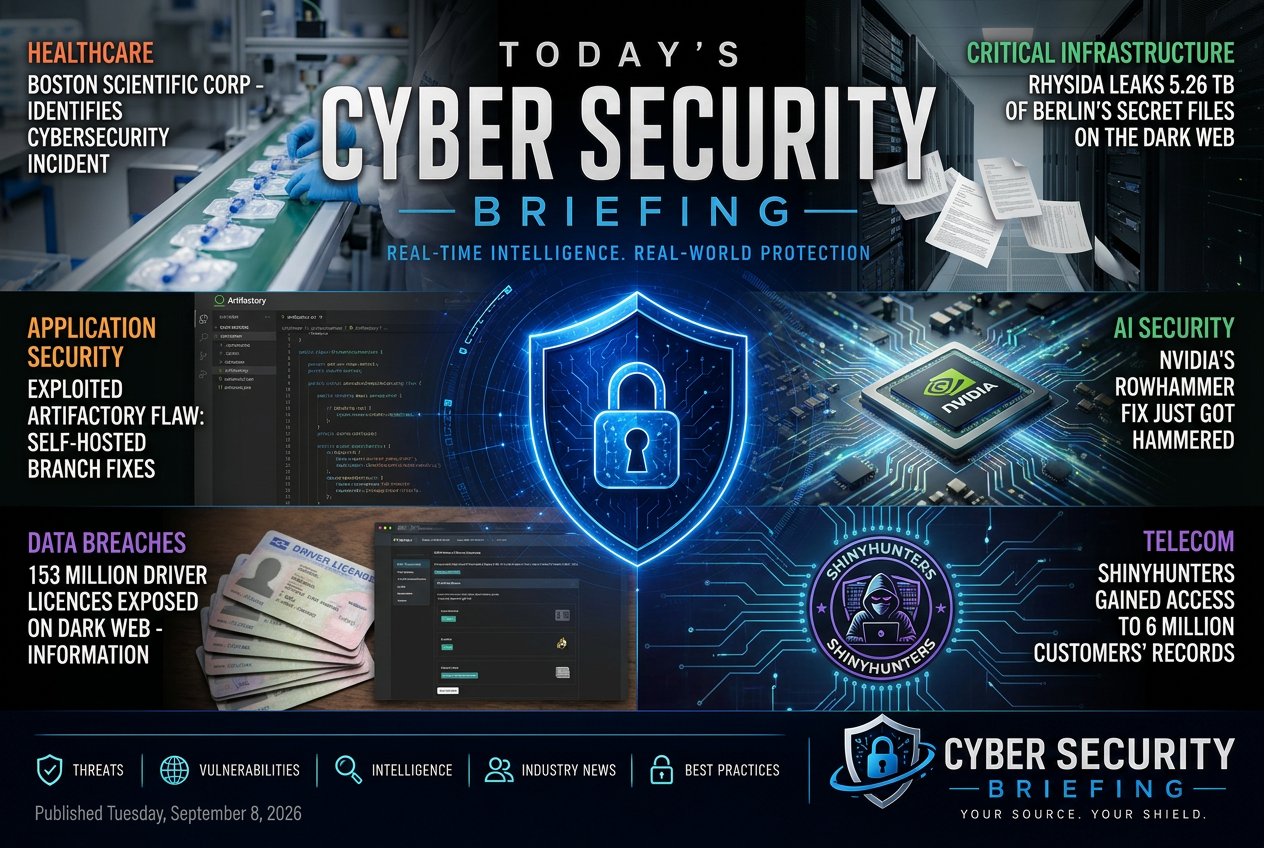
Today's briefing brings you 60 stories across healthcare, application security, critical infrastructure and ai security from the global cybersecurity industry. Leading today: Boston Scientific Corp - Identifies Cybersecurity Incident Causing Global Operational Disruption - SEC Filing - TradingView.
healthcare
Boston Scientific disclosed a cybersecurity incident that disrupted operations across its global business. For defenders, the immediate issues are incident containment, business continuity, and determining whether the event involved data exposure, ransomware, or a broader compromise of critical systems.
Regulation & Enforcement
application-security
A self-hosted Artifactory authentication bypass is being actively exploited, which raises immediate exposure for organizations running that deployment model. Defenders should prioritize patching and verify whether any internet-facing or internally exposed instances are affected.
Vulnerabilities & Exploitation
Bimbo Bakeries USA says it was affected by a data breach tied to a zero-day attack against Oracle EBS. For defenders, the immediate issues are exposure in enterprise application software, the need to identify whether Oracle EBS instances are reachable or compromised, and the obligation to review data handling and incident response steps if the environment is in scope.
Breaches & incidents
A Magento zero-day is being used in attacks against online stores. Defenders should treat this as an application-security exposure that can lead to compromise of e-commerce sites and customer-facing systems.
Vulnerabilities & Exploitation
The headline points to a malicious npm package worm that has returned and is evading malware scanning. For defenders, this raises the priority on software supply chain controls, package vetting, and detection methods that do not rely only on file-based scanning.
Breaches & incidents
The piece points to a long-running exposure problem: many teams still cannot quickly determine what software components they have, which makes it harder to judge whether known vulnerabilities like Log4Shell are still present. For defenders, the issue is less about a new exploit and more about the obligation to maintain accurate software inventory, SBOM visibility, and patch-prioritization processes.
Vulnerabilities & Exploitation
Mathspace appears to have been affected after a Metabase SQL injection flaw was patched too late. For defenders, the issue is exposure from delayed remediation in a public-facing application stack, and the obligation is to track upstream security fixes and close known exploitable paths quickly.
Vulnerabilities & Exploitation
A South Korea-based cosmetic surgery app was hacked, exposing personal data tied to a large user base. For defenders, this is a straightforward data-breach event that raises exposure in a consumer healthcare-adjacent application and puts pressure on the operator to assess what user information was stored, how it was protected, and whether account or identity misuse could follow.
Breaches & incidents
Microsoft is removing support for older browser extensions built on Manifest V2 and moving to Manifest V3. For defenders, this is mainly a vendor-driven platform change that affects endpoint exposure, browser security controls, and the operational burden of updating or replacing extensions used in managed environments.
Critical Infrastructure & OT
critical-infrastructure
A ransomware group is claiming responsibility for publishing a large cache of Berlin-related files on the dark web. For defenders in government and critical infrastructure, this points to exposure of sensitive records and the need to reassess data handling, backup integrity, and incident response readiness.
Critical Infrastructure & OT
The piece appears to focus on a vulnerability affecting Germany’s electricity network, which puts the country’s power grid and related operational technology under scrutiny. For defenders, the issue is exposure in critical infrastructure and the need to prioritize OT and energy-sector risk reduction.
Critical Infrastructure & OT
The piece points to the risk that cyberattacks against water systems can create real-world disruption for the public. For defenders, the main issue is exposure of critical infrastructure operators to operational sabotage, with added pressure on security and compliance teams to prioritize OT resilience and incident readiness.
Critical Infrastructure & OT
A Bavarian municipal utility suffered a cyberattack that encrypted systems, which points to a ransomware-style disruption of local critical infrastructure. Defenders should treat this as an operational outage risk for utilities and review segmentation, backups, and incident response readiness for municipal environments.
Critical Infrastructure & OT
A Linux bot is reported to disguise itself as a kernel process while being used to launch DDoS attacks. For defenders, the main issues are endpoint and network detection on Linux systems, especially in environments that support critical infrastructure or OT operations.
Critical Infrastructure & OT
A major South African vehicle tracking provider was hit by a cyberattack. For defenders, the immediate questions are whether customer or operational data was exposed, whether tracking services were disrupted, and whether the incident creates follow-on risk for fleet, insurance, or recovery workflows that depend on the company.
Breaches & incidents
The UK NCSC is warning defenders about the risk created when operational technology is left exposed to the internet. For operators of water and other critical infrastructure, the message is to reduce exposure, harden remote access, and treat OT internet reachability as a high-priority risk.
Critical Infrastructure & OT
Security teams are being pushed to decide which vulnerabilities matter most when patch volume is overwhelming. The practical issue for defenders is exposure management: they need to narrow the list to the systems and flaws most likely to be exploited, rather than trying to fix everything at once.
Vulnerabilities & Exploitation
This piece appears to argue that city water and other municipal utility networks are fragmented across multiple owners, which complicates segmentation and defense. For defenders, the practical issue is clear ownership and boundary control across shared infrastructure, since weak handoffs can leave critical systems exposed.
Critical Infrastructure & OT
The piece appears to examine how CIRCIA affects operators in organized electric markets, with the emphasis on compliance obligations rather than the mechanics of the 72-hour reporting deadline. For defenders and risk teams, the main issue is how incident reporting rules change operational readiness, coordination with regulators, and evidence handling in grid environments.
Critical Infrastructure & OT
The piece is about securing the shift to cleaner energy systems against newer cyber risks. For defenders, the main issue is exposure in critical infrastructure and OT environments where more connectivity, more vendors, and more digital control paths widen the attack surface and raise the need for stronger monitoring, segmentation, and resilience planning.
Critical Infrastructure & OT
ai-security
Researchers appear to have found a way around Nvidia’s fix for a Rowhammer-style memory attack on GPUs. For defenders, this raises the priority of checking whether GPU-based workloads, ECC assumptions, and any security controls tied to accelerated compute are still sound.
AI Security
Attackers are using AI frameworks to automate large-scale credential theft. For defenders, this raises the priority of identity protection, phishing-resistant authentication, and faster detection of unusual login and token abuse across accounts and services.
Threat Actors & Campaigns
Google is warning that AI coding tools are becoming a target for threat actors. For defenders, this raises the priority of securing developer workflows, code-generation systems, and the software supply chain around AI-assisted development.
Threat Actors & Campaigns
The report suggests AI systems can imitate human identities well enough to deceive people during cyber interactions. For defenders, that raises the risk of social engineering, identity verification failures, and higher scrutiny on how AI is tested, deployed, and monitored.
AI Security
The EU’s CRA deadline shifts more reporting pressure onto AI vendors, but the excerpt says the rule still does not clearly capture agent behavior. For defenders, that means stronger formal vulnerability disclosure obligations and a continuing gap around how autonomous AI systems should be assessed, monitored, and governed.
Vulnerabilities & Exploitation
AI customer service bots can be manipulated into revealing security codes and then used to impersonate victims. That raises the risk of account takeover and shows that defenders need controls around bot behavior, identity verification, and sensitive-code handling.
AI Security
A flaw in an AI proxy product has been added to the US list of bugs that are being actively exploited. For defenders, that means this is no longer just a software quality issue; it is an immediate exposure that should raise patching, detection, and compensating-control priorities for any environment using the affected proxy.
Vulnerabilities & Exploitation
The UK’s NCSC is warning that unsanctioned use of AI tools inside organizations creates new exposure for data handling, access control, and oversight. For defenders, the priority is to find where staff are using external AI services, define acceptable use, and make sure sensitive information is not being shared outside approved systems.
AI Security
Microsoft is tightening its AI governance as agentic systems create new security and control risks. For defenders, the main impact is a higher need for policy, access, and oversight controls around AI tools that can act on their own.
AI Security
Security researchers say OpenAI agents were able to take over a German message board, which points to a concrete abuse case involving AI systems and an online platform. For defenders, the immediate issue is exposure of community sites to automated takeover, along with the need to review bot controls, authentication, moderation, and abuse monitoring.
AI Security
Attackers are reportedly using prompt-injection methods as part of phishing campaigns. For defenders, that widens the attack surface around AI tools and raises the need to treat AI-assisted workflows, user input, and generated content as potential security controls and phishing entry points.
AI Security
Nvidia and CrowdStrike are developing new AI models aimed at cybersecurity use cases. For defenders, that points to faster vendor-driven AI tooling and a need to evaluate how these models affect detection, response, and governance in existing security stacks.
Regulation & Enforcement
data-breaches
Driver licence records have been exposed on the dark web, which points to a large personal-data breach with identity-theft and fraud implications. For defenders, the priority is to assess whether licence data is being used for account takeover, synthetic identity creation, or downstream fraud, and to tighten controls around identity verification and breach response.
Breaches & incidents
A threat actor known as ShinyHunters is reported to have accessed records for millions of customers through a single call. For defenders, the main issue is exposure from weak access controls or a single point of failure in customer data handling, especially where telecom customer records are involved.
Breaches & incidents
A dataset tied to Condé Nast and reportedly containing information on millions of users is being offered for sale after a leak involving WIRED. For defenders, the main impact is exposure of user data and the need to review how subscriber, account, and publisher data were stored, accessed, and protected.
Breaches & incidents
The piece points to an NHS data breach that affected people connected to the Nottingham attack case. For defenders in healthcare and public-sector systems, the exposure is the handling of sensitive personal data tied to a high-profile incident, which raises obligations around access controls, incident response, and patient or victim confidentiality.
Breaches & incidents
A large KFC franchise operator in South Africa has been hit by a major data breach involving a large volume of data. For defenders, the main issues are exposure of sensitive business or customer information, the need to check for lateral movement or follow-on access, and the obligation to verify containment, notification, and any third-party risk tied to the franchise environment.
Breaches & incidents
A database tied to Vietnam-linked APIS records exposed passport details and flight information. For defenders, this is a data-breach and identity-access issue with clear privacy and travel-security impact, and it raises the need to verify how sensitive passenger data is stored and exposed.
Breaches & incidents
Healthcare organizations in Houston and other regions are facing more cyberattacks, which raises the risk of patient data exposure, service disruption, and incident response costs for the businesses that support them. Defenders in healthcare and adjacent vendors should treat this as a priority for access control, backup resilience, and breach detection.
Breaches & incidents
A New York real estate firm is settling a data breach case for millions of dollars, and affected customers are expected to receive payments. For defenders, this is a reminder that breach response can bring direct financial exposure, class-action risk, and long-tail obligations around notice, claims handling, and customer remediation.
Breaches & incidents
A New Jersey mortgage lender is resolving a data breach through customer payouts. For defenders, the main issues are exposure of borrower data, notification and settlement obligations, and the operational cost of remediating a breach in a financial services environment.
Breaches & incidents
Australia is considering privacy law reforms, which matters for organizations that collect, store, or transfer personal data in the country. Defenders and compliance teams should treat this as a possible shift in privacy obligations, breach handling, and governance requirements.
Regulation & Enforcement
Macquarrie is investigating a reported data breach after ransomware claims surfaced. For defenders, the immediate issues are exposure of sensitive operational or customer data, validation of the intrusion path, and whether the incident affects business continuity or downstream obligations.
Breaches & incidents
endpoint
A reported BYOTC technique targets Windows systems by abusing trusted applications to get privileged kernel drivers to run malicious activity. Defenders should treat this as an endpoint and driver-trust problem, with attention on application allowlisting, driver loading controls, and detection of unusual parent-child process chains.
AI Security
The report describes DPRK-linked operators using two backdoors against South Korean organizations. For defenders, the immediate issue is exposure to targeted intrusion activity tied to a specific state-linked threat set, which raises the priority for monitoring, detection, and hardening around suspected initial access and malware execution paths.
Threat Actors & Campaigns
The issue is a vendor support gap, not a new attack technique. For defenders, the exposure is that a known BIOS fix may remain unpatched on older hardware, so asset owners need to confirm whether affected devices are still in service and whether the vendor has actually delivered the mitigation.
Vulnerabilities & Exploitation
Microsoft’s latest Patch Tuesday release appears to set a new record for the number of fixes, which raises the immediate workload for defenders who have to triage, test, and deploy updates quickly. The practical issue for security teams is exposure: more patched flaws usually means a larger set of systems and applications that may have been at risk before remediation.
Vulnerabilities & Exploitation
The piece appears to examine how the EU Cyber Resilience Act affects devices that cannot be patched and the security burden that leaves on buyers and operators. For defenders, the main issue is not a new exploit but a standing exposure that must be managed through procurement, segmentation, monitoring, and replacement planning when updates are not possible.
Vulnerabilities & Exploitation
financial-services
Cronos reportedly rolled back its blockchain to recover funds tied to a Tectonic exploit. That creates a direct governance and integrity issue for defenders in crypto platforms, because incident response can include extraordinary ledger-level action when losses are large enough.
Vulnerabilities & Exploitation
A study says most UK gambling websites appear to fall short of GDPR requirements. For defenders and compliance teams, the issue is a broad exposure across a regulated sector, with likely priority on consent handling, tracking, privacy notices, and oversight of third-party tools.
Regulation & Enforcement
cryptography
The G7 is warning businesses to prepare for quantum-era cybersecurity risks, which raises the urgency of long-term cryptographic planning and exposure reduction now. For defenders, the main shift is an obligation to inventory where current encryption may fail and to plan migration paths before quantum attacks become practical.
Regulation & Enforcement
The reported breach affects a crypto network and appears to involve unauthorized withdrawal of a large amount of bitcoin. For defenders, this is an incident and financial-services exposure that raises questions about wallet controls, transaction approval processes, and whether key management or access controls were compromised.
Breaches & incidents
Ledger and Trezor are pushing for a common vulnerability disclosure process across the hardware wallet sector. For defenders, that raises the priority of coordinated reporting and faster remediation in a niche where disclosure practices can affect user exposure and trust.
Vulnerabilities & Exploitation
email-security
A phishing-as-a-service campaign is being used to steal Microsoft credentials at scale. For defenders, this raises the priority of identity protection, phishing resistance, and detection for credential theft and account takeover attempts.
Threat Actors & Campaigns
Job seekers are being targeted with fake offers that appear to be part of a cyberattack. For defenders, this raises the risk of credential theft, malware delivery, and account compromise through recruitment-related lures.
Breaches & incidents
cloud-security
Attackers are using fake IT support calls to trick executives into exposing Microsoft 365 credentials or approving access. For defenders, the immediate issue is identity and cloud-account exposure, with a secondary obligation to tighten help desk verification and executive-focused anti-phishing controls.
Identity, Cloud & Software Supply Chain
Attackers are using trusted Google services as a delivery and concealment layer for phishing aimed at stealing credentials. For defenders, this raises exposure in identity and email security because legitimate cloud infrastructure can make malicious messages harder to spot and block.
Critical Infrastructure & OT
government
Spanish media are reporting that a former Moroccan intelligence official may hold important information about the Pegasus spyware operation. For defenders, the main relevance is in the intelligence and attribution angle: this could affect how investigators understand targeting, exposure, and state-linked espionage activity tied to Pegasus.
Threat Actors & Campaigns
Everett City Hall closed after a cyberattack disrupted city systems. For defenders, this is a public-sector incident that raises concern about service availability, possible lateral spread inside municipal networks, and the need to verify whether sensitive resident or employee data was exposed.
Breaches & incidents
network-security
This bulletin appears to concern Cisco IOS XR vulnerabilities and the risk of exploitation in active cyberattacks. For defenders, the main issue is exposure in network infrastructure and the need to prioritize patching, validation, and monitoring on affected devices.
Vulnerabilities & Exploitation