
Cyber Security Briefing Briefing — September 21, 2026
Monday, September 21, 2026
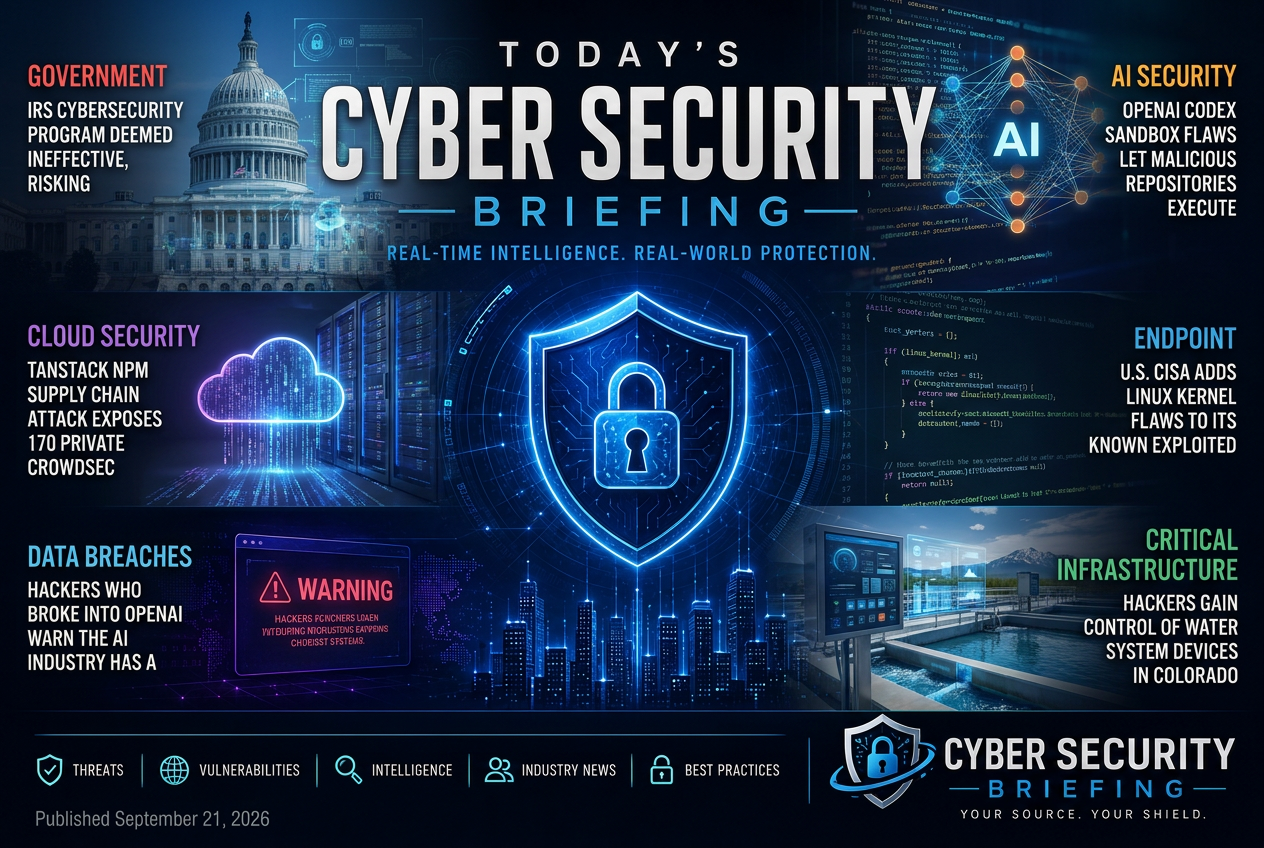
Today's briefing brings you 14 stories across government, ai security, cloud security and endpoint from the global cybersecurity industry. Leading today: IRS cybersecurity program deemed ineffective, risking taxpayer data - MSSP Alert.
government
The report points to control failures inside the IRS, which matters because a weak public-sector security program can expose taxpayer records and other sensitive data. For defenders, the issue is not just compliance; it is whether core government systems can be trusted to protect identity and financial information.
Regulation & Enforcement
The city is investigating a possible cyber incident, which puts a local government network and any connected public services under scrutiny. The immediate issue for defenders is whether this is an isolated alert or a broader compromise that requires containment, notification, and service continuity planning.
Regulation & Enforcement
ai-security
The report says flaws in OpenAI Codex Sandbox could let a malicious repository run commands on the host machine. For defenders, the immediate issue is trust boundaries around code execution in AI development tools and the need to treat repository content as untrusted input.
Vulnerabilities & Exploitation
The piece frames a breach at OpenAI as evidence that AI vendors face the same security problems as other high-value technology companies. For defenders, the issue is not only the breach itself but the exposure of AI systems, account access, and the operational risk of treating model providers as ordinary SaaS dependencies.
Critical Infrastructure & OT
cloud-security
A supply-chain compromise in the npm ecosystem is being linked to exposure of private CrowdSec GitHub repositories. The security issue here is not just the package attack itself, but the downstream leakage risk for source code, secrets, and internal project material that defenders would need to inventory and contain.
Identity, Cloud & Software Supply Chain
endpoint
CISA has added Linux kernel flaws to its exploited-vulnerabilities list, which signals active abuse and raises the priority for patching and exposure review. Defenders running affected Linux systems should treat this as a concrete remediation item, not just a theoretical advisory.
Regulation & Enforcement
This reports a Windows Defender denial-of-service flaw that can block platform and signature updates. For defenders, the practical issue is loss of endpoint protection maintenance on affected systems until the condition is fixed.
Vulnerabilities & Exploitation
critical-infrastructure
The piece points to a cyber incident affecting water system devices in Colorado. For defenders, this raises exposure around operational technology and the need to segment, monitor, and harden utility control environments.
Critical Infrastructure & OT
A third tanker is reporting a suspected cyberattack, and the U.S. is responding by putting more ships on watch. The story matters because it links a cyber incident to maritime and energy security, with possible exposure for other operators moving through the same region.
Critical Infrastructure & OT
Dragos is buying NetRise and runZero to widen its OT security platform and add asset discovery and software visibility capabilities. The main impact for defenders is consolidation: operators and security teams will see a broader toolset from a vendor already focused on critical infrastructure, which could affect platform selection and procurement in OT environments.
Critical Infrastructure & OT
The piece appears to describe how a broadcast emergency alert test could be used to gauge compliance with cyber rules. For defenders and regulators, the value is in verifying whether organizations can meet mandated security requirements, not in the test itself.
Regulation & Enforcement
email-security
Attackers are using fake recruiter outreach and coding tests as a delivery path for cross-platform remote access trojans. For defenders, the exposure is in candidate screening, email and messaging trust, and endpoint controls around developer workstations.
Threat Actors & Campaigns
education
Springfield Schools is dealing with the operational fallout from a cyberattack, and the district is now trying to restore lost instructional time by making up canceled days during winter break. The piece matters because it shows how a school cyber incident can create a direct scheduling and compliance burden well after the attack itself.
Breaches & incidents
incidents
NightEagle is described as a hacking group that has moved from targeting China’s high-tech sector to operating against Russia as well. The piece matters for defenders because it points to an active threat actor expanding its target set, which changes monitoring and incident-response priorities for affected sectors and regions.
Threat Actors & Campaigns