
Cyber Security Briefing Briefing — September 23, 2026
Wednesday, September 23, 2026
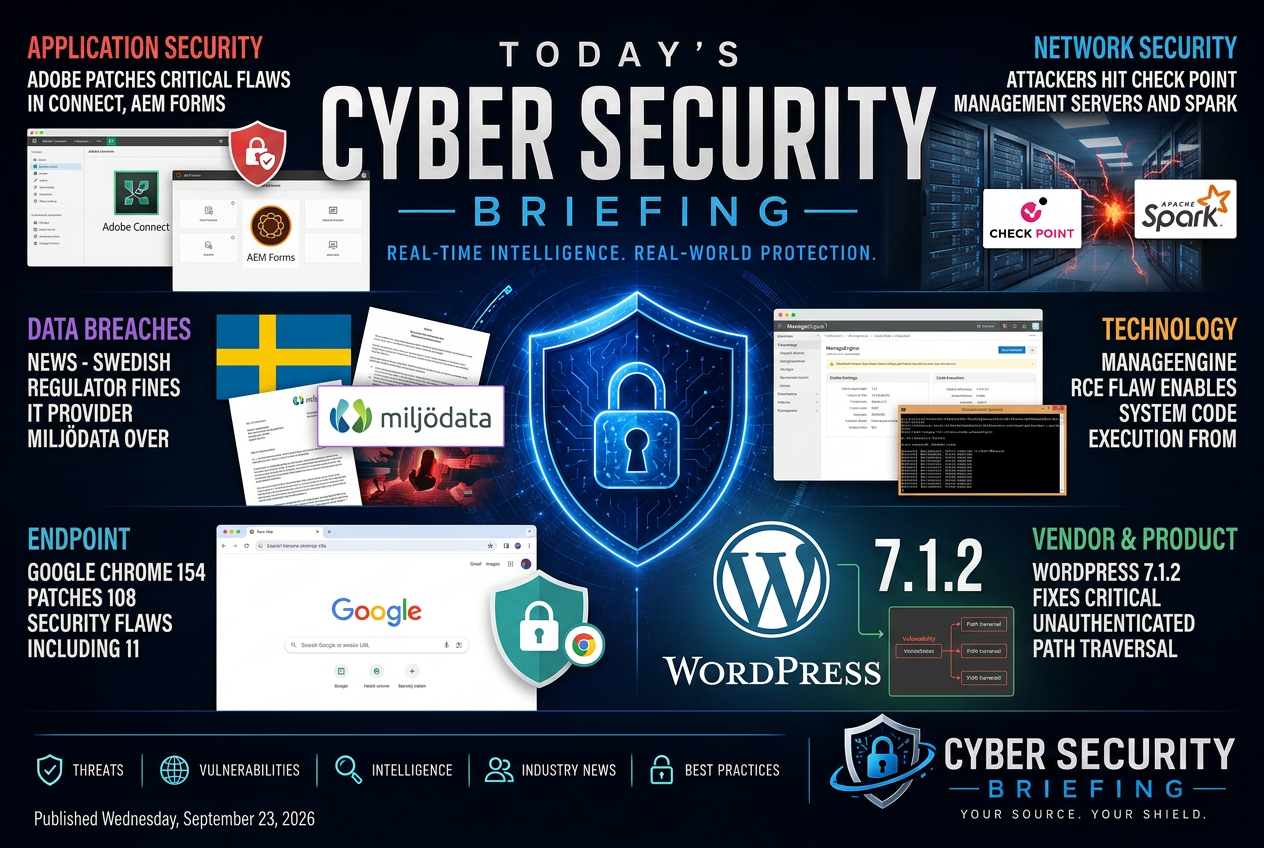
Today's briefing brings you 30 stories across application security, network security, data breaches and technology from the global cybersecurity industry. Leading today: Adobe Patches Critical Flaws in Connect, AEM Forms - SecurityWeek.
application-security
Adobe has patched critical flaws in Connect and AEM Forms. Defenders using these products need to prioritize exposure review and patch validation because both are customer-facing platforms where a serious flaw can turn into broad application risk.
Vulnerabilities & Exploitation
WordPress has shipped a security release to fix a critical unauthenticated path traversal flaw. For defenders, this is a patch-priority issue for any internet-facing WordPress deployment because unauthenticated bugs can raise exposure quickly once details are public.
Vulnerabilities & Exploitation
network-security
Attackers are actively targeting exposed management and security appliances from Check Point and F5. For defenders, the immediate issue is exposure of perimeter and administrative infrastructure, which raises the priority of patching, access review, and monitoring for compromise across firewall and access management estates.
Vulnerabilities & Exploitation
Arista is telling customers to patch a zero-day in its VCO product that is already being exploited. For defenders, this is an immediate exposure and patching priority because it moves the issue from theoretical risk to active attack pressure on managed network infrastructure.
Vulnerabilities & Exploitation
Check Point says it has fixed a critical flaw that was already being exploited, which makes this a patch-and-exposure story rather than a routine advisory. Defenders should treat affected Check Point deployments as immediate priority because active exploitation turns a vendor fix into an urgent risk-reduction task.
Vulnerabilities & Exploitation
Belgium’s cyber authority is warning defenders about an improper input validation flaw in VeloCloud Orchestrator and urging immediate patching. The practical issue is exposure in a network management platform that could affect operators relying on it for remote connectivity and traffic control.
Vulnerabilities & Exploitation
data-breaches
Sweden's regulator has fined IT provider Miljödata over a breach that affected millions of people. This is a clear enforcement outcome after a large data breach and it matters for organizations that handle personal data on behalf of others.
Regulation & Enforcement
Tving says it is moving to a zero-trust approach after a major data breach. The piece is relevant because it points to a concrete post-incident security response and the exposure of user or corporate data.
Breaches & incidents
Quest Apartment customers are being told to check whether passport and licence details were exposed in a major breach. For defenders, this is a data-breach and identity-theft problem because travel and identity documents can be reused for fraud, account takeover, and follow-on social engineering.
Breaches & incidents
Hackers are claiming a breach of an FBI jobs site and the theft of a large data set. If true, the immediate issue for defenders is exposure of government employment and identity data, plus the need to verify whether the intrusion reached any connected systems beyond the public-facing site.
Breaches & incidents
A cyber breach exposed medical results and personal information tied to veterans, which makes this a direct data-breach and healthcare-privacy issue. The main defender concern is exposure of sensitive records and the follow-on obligation to notify affected people, contain the breach, and review the handling of protected health data.
Regulation & Enforcement
Skroutz Last Mile says a security incident exposed customer contact details. The practical issue for defenders is exposure of personal data through an operational incident, which raises breach handling, notification, and account-monitoring obligations.
Breaches & incidents
Seyfarth is reporting a data breach that exposed Social Security numbers, which makes this an identity-theft and notification issue for affected people and a disclosure and response issue for the firm. The main defender takeaway is that legal and professional-services firms hold sensitive identity data that can create direct downstream risk when exposed.
Breaches & incidents
Dartmouth is resolving litigation tied to an Oracle-related data breach with a cash settlement, which makes this a consequence story rather than just a disclosure. For defenders, it reinforces that breaches can create direct legal and financial exposure for the affected institution, especially in education where sensitive records are often involved.
Regulation & Enforcement
Technology
A reported ManageEngine flaw allows remote code execution with SYSTEM-level impact from the Windows login screen. For defenders, that means a product used in enterprise environments may need immediate patch review and exposure assessment, especially where management consoles are reachable on internal networks.
Vulnerabilities & Exploitation
endpoint
Google Chrome is being patched for a large set of security flaws, including multiple critical issues. For defenders, the immediate question is exposure to unpatched browsers, since browser flaws can quickly become a workstation entry point or a path to credential theft and further compromise.
Vulnerabilities & Exploitation
Volexity says a China-aligned group is chaining Chrome and Microsoft vulnerabilities, which puts browser and Windows exposure back at the center of defender priority. The immediate issue for security teams is faster patching, tighter exploit detection, and review of whether related intrusions have already reached endpoints.
Vulnerabilities & Exploitation
This is about a newly disclosed Microsoft Defender exploit tied to a named threat actor. For defenders, the immediate issue is exposure in a widely deployed endpoint product and the need to assess patching, detection, and hardening guidance quickly.
Vulnerabilities & Exploitation
ai-security
The report says a Chinese-speaking hacker used AI agents to break into many companies and steal payment card data. For defenders, the immediate issues are account security, detection of AI-assisted intrusion activity, and protecting payment systems and customer records.
Regulation & Enforcement
The piece appears to examine how AI changes the attack and defense picture for space systems that support critical infrastructure. For defenders, the main implication is that space operators and their suppliers need to treat AI-enabled misuse, automation, and targeting of operational dependencies as part of critical-infrastructure risk.
Critical Infrastructure & OT
CERT Polska appears to be documenting the technical analysis and disclosure of MikroTrick, with an emphasis on how LLM agents were used in the work. For defenders, that points to both an AI-security angle and an operational disclosure lesson: what was found, how it was handled, and what exposure or mitigation follows for affected systems.
Vulnerabilities & Exploitation
critical-infrastructure
Researchers found a remote attack path against the BYD Shark 6 that can expose vehicle controls and cabin audio. For defenders, the issue is a concrete vehicle-security exposure that affects both driver safety and occupant privacy, and it raises the priority of hardening connected-car interfaces and monitoring for unauthorised remote access.
Critical Infrastructure & OT
Stolen credentials are putting water utilities at risk, which makes this an identity and critical-infrastructure problem rather than a generic password story. For defenders, the immediate issue is exposure of operator access and the need to tighten account hygiene, monitoring, and password reuse controls across water-sector environments.
Critical Infrastructure & OT
Forescout’s research points to a basic segmentation problem in OT environments: most network segments are still shared with non-OT systems. That raises the exposure of industrial control assets to lateral movement from IT networks and makes segmentation and asset isolation a higher priority for defenders.
Critical Infrastructure & OT
CISA is preparing recovery guidance for critical infrastructure operators and is urging them to test their recovery plans. That matters because recovery readiness is a core defender obligation in sectors where downtime can affect essential services.
Critical Infrastructure & OT
India’s semiconductor buildout is being framed as a cybersecurity exposure problem, not just an industrial policy story. For defenders, the issue is that more chip fabrication and supply-chain activity creates more targets for intrusion, tampering, and supplier risk across critical manufacturing and associated infrastructure.
Critical Infrastructure & OT
enforcement
The piece is about a government setting a deadline to close major cybersecurity gaps. It matters to defenders because it signals a compliance push that can force faster remediation, tighter reporting, and closer scrutiny of public-sector security posture.
Regulation & Enforcement
Police action against a suspect tied to cyberattacks on Latvian companies. The security relevance is that it signals enforcement against intrusion activity affecting named organizations, which can matter to regional defenders watching for repeat targeting or related tactics.
Breaches & incidents
education
Princeton is investigating a possible cybersecurity incident, which suggests an early-stage security event rather than a confirmed breach. For defenders, the immediate issue is exposure and response: whether any systems or records were accessed, and what containment or notification obligations follow if the incident is confirmed.
Breaches & incidents
government
Suisun City Hall has reopened after a recent cyberattack, which makes this a local government incident with operational disruption. The article matters to defenders because it signals a real-world service impact and a likely need for recovery, containment, and public-sector hardening.
Breaches & incidents