
Cyber Security Briefing Briefing — September 24, 2026
Thursday, September 24, 2026
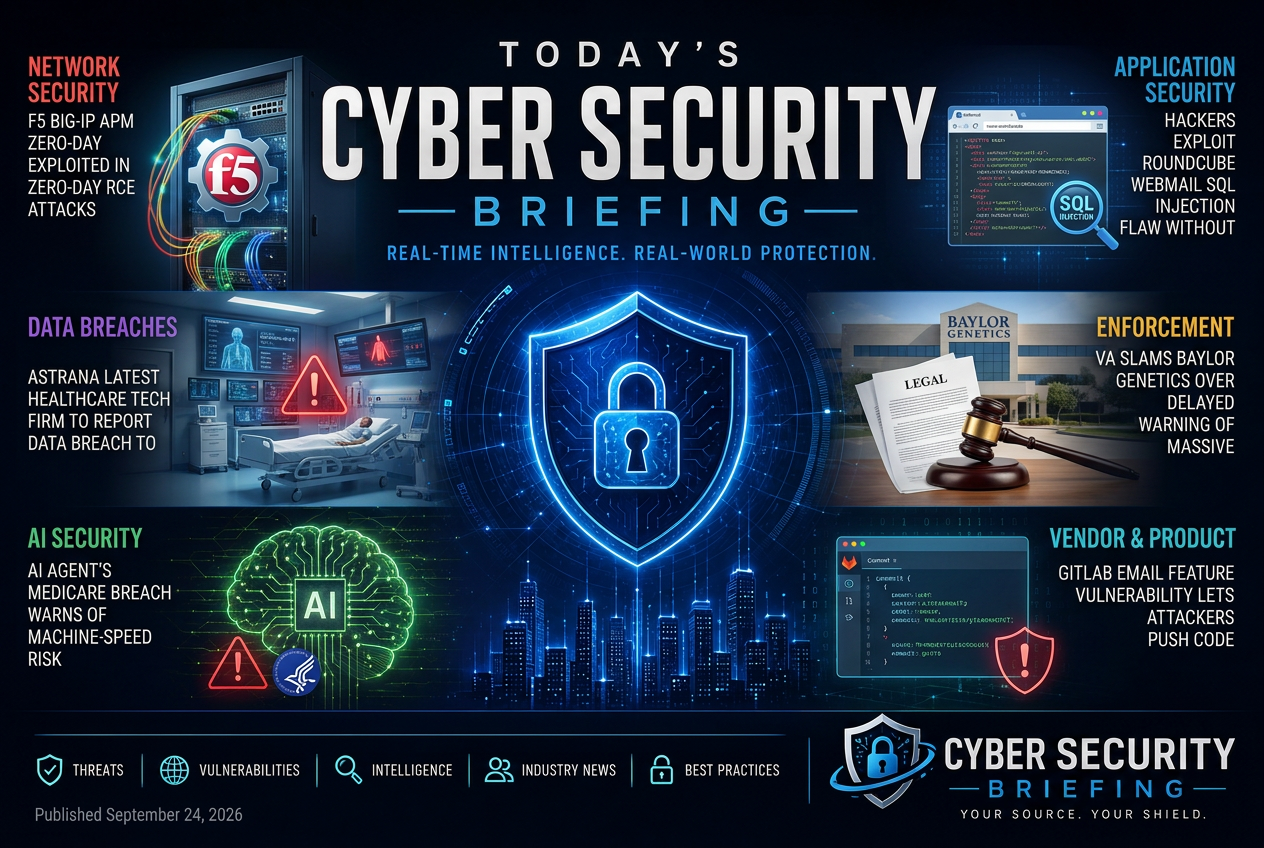
Today's briefing brings you 23 stories across network security, data breaches, application security and ai security from the global cybersecurity industry. Leading today: F5 BIG-IP APM Zero-Day Exploited in Zero-Day RCE Attacks - Security Affairs.
network-security
A zero-day in F5 BIG-IP APM is being exploited to deliver remote code execution attacks. For defenders, this raises immediate exposure on perimeter access infrastructure and makes patching, mitigation, and asset inventory urgent.
Vulnerabilities & Exploitation
data-breaches
Astrana has reported a data breach to the SEC, which makes this a disclosure and enforcement-relevant incident rather than a routine business update. For defenders, the immediate issue is exposure: a healthcare technology company has confirmed a breach, so peers in the sector should review similar external access paths, logging, and incident reporting obligations.
Regulation & Enforcement
The VA is criticizing Baylor Genetics for not warning promptly about a large patient data breach. For defenders in healthcare and regulated sectors, the issue is less the breach itself than the delay in disclosure, which can affect notification duties, incident response, and downstream exposure management.
Regulation & Enforcement
A threat actor is claiming a large theft of FBI agent records, which makes this a law-enforcement data breach story with potential exposure for personnel and investigations. The immediate defender issue is validating the claim, containing any related compromise, and determining whether identities or operational details were exposed.
Breaches & incidents
A breach at Skroutz Last Mile exposed customer contact and delivery information. For defenders, this is a plain data-breach event with privacy and fraud exposure for affected customers and a reminder to tighten access to logistics records and monitoring around customer-data handling.
Regulation & Enforcement
application-security
A SQL injection flaw in Roundcube webmail is being exploited without authentication. For defenders, that raises priority on patching exposed webmail systems and reviewing whether mail accounts or associated infrastructure were accessed through the vulnerable service.
Vulnerabilities & Exploitation
GitLab users should treat this as an application security issue that could affect private source code access and integrity. The headline indicates a flaw in GitLab’s email feature that could let an attacker push code into private repositories, which raises exposure for code owners, security reviewers, and teams that rely on GitLab for controlled contributions.
Vulnerabilities & Exploitation
A critical Next.js flaw is being described as enabling remote code execution through a weaponized SVG file. For defenders, that makes any exposed Next.js deployment a patching and exposure-priority issue, especially where user-uploaded files or SVG handling are part of the application flow.
Vulnerabilities & Exploitation
ai-security
The story points to a breach involving an AI agent and Medicare, which makes it relevant to defenders because it combines identity, healthcare data, and machine-speed automation risk. For security teams, the practical question is how much access an AI system has and what controls stop it from moving faster than humans can intervene.
AI Security
This piece is about a claimed security risk in Meta’s AI assistant that could leave Mac users exposed to attack. For defenders, the relevant issue is whether the product introduces a new endpoint or application security exposure that needs validation, hardening, or user guidance.
Vulnerabilities & Exploitation
critical-infrastructure
Password theft at a large number of US water utilities points to exposed identity controls across critical infrastructure, not just an isolated account problem. The security concern for defenders is access risk in operational environments that can affect water services if stolen credentials are reused or poorly segmented.
Critical Infrastructure & OT
ENISA is highlighting a systemic risk for EU digital infrastructure: the more it depends on shared services, suppliers, and interconnected systems, the more a failure or compromise can spread. For defenders, the practical issue is exposure management across third parties and dependencies, not just hardening internal networks.
Regulation & Enforcement
The FCC is giving broadcasters compliance guidance ahead of new cybersecurity requirements for the Emergency Alert System. This matters for operators of public warning infrastructure because it turns a rule change into a near-term operational obligation and raises the priority of securing EAS-related systems.
Regulation & Enforcement
government
The piece points to a coordination problem in Europe’s cyber posture: member states are not sharing enough data for EU-level defenders to build a full picture of threats and incidents. That matters for detection, cross-border response, and regulatory oversight, because weak information sharing leaves gaps in situational awareness and slows coordinated action.
Regulation & Enforcement
identity-access
The story is about technology and VPN firms pressing Ottawa to revise a lawful-access bill. For defenders, the issue is not a breach but the legal and operational impact of any new access requirements on encryption, user privacy, and provider compliance duties.
Regulation & Enforcement
ZTE’s SmartLife platform has vulnerabilities that can let attackers take over user accounts. For defenders, the immediate issue is account security on a vendor platform, which creates exposure for customers who rely on it and raises the priority of patching, hardening, and monitoring for unauthorized access.
Vulnerabilities & Exploitation
financial-services
This is a fraud and identity abuse story, not a product or policy issue. It shows how customer-support impersonation can be used to steal money from crypto users and why service desks and user verification remain a direct risk for defenders.
Breaches & incidents
enforcement
This is a privacy enforcement story centered on Facebook's handling of users in New Mexico. For defenders and compliance teams, the issue is not a technical exploit but the legal and operational exposure that comes from how personal data is collected, explained, and controlled.
Regulation & Enforcement
This points to an internal control failure at a major U.S. tax agency, not a new exploit. For defenders, the relevant issue is governance and assurance: if a core cybersecurity framework is ineffective in key areas, the organization likely has exposure in detection, risk management, or control execution that warrants remediation and oversight.
Regulation & Enforcement
education
SideCopy is targeting Indian academic institutions with updated intrusion methods, which puts universities and related organizations on notice about a persistent threat actor adapting its tactics. The story matters for defenders because it points to active targeting of the education sector in India and suggests existing detections or controls may need review.
Threat Actors & Campaigns
endpoint
Gigabyte has patched a high-severity flaw in the Control Center kernel driver. For defenders, this is mainly an endpoint exposure and patch-management issue because privileged driver bugs can be used to weaken local security controls or gain deeper system access.
Vulnerabilities & Exploitation
defense
New Zealand is publicly identifying China as its most persistent state-backed cyber threat. The practical issue for defenders is that this points to sustained espionage and intrusion pressure on government and critical institutions, which raises the priority of monitoring, hardening, and incident response even without a single disclosed breach in the headline.
Threat Actors & Campaigns
software-supply-chain
Ubuntu is changing kernel release cadence to weekly updates so security fixes for CVEs can reach users faster. This matters to defenders because it shortens exposure windows for patched kernel flaws, but it also increases the need to track and test more frequent kernel rollouts across fleets.
Vulnerabilities & Exploitation