
Cyber Security Briefing Briefing — October 3, 2026
Saturday, October 3, 2026
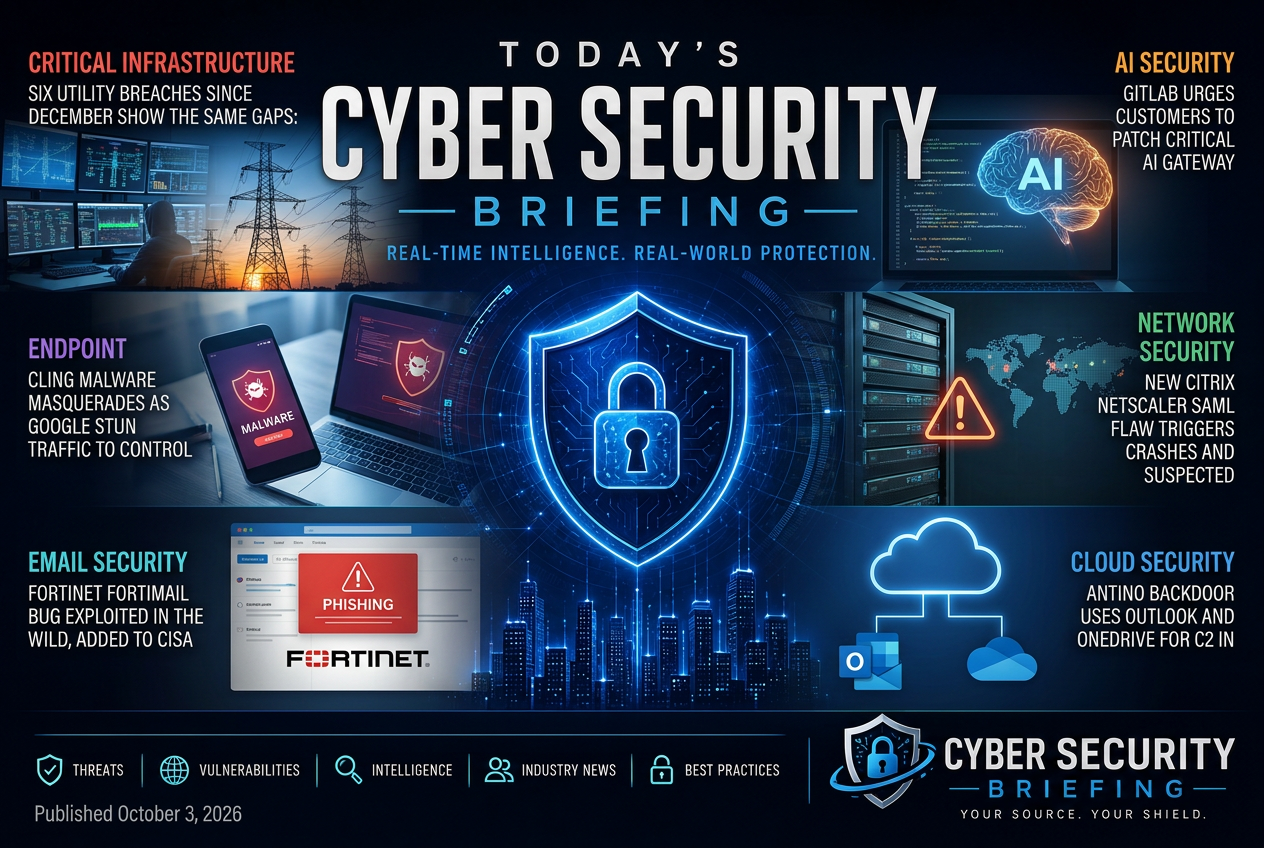
Today's briefing brings you 12 stories across critical infrastructure, ai security, endpoint and network security from the global cybersecurity industry. Leading today: Six Utility Breaches Since December Show the Same Gaps: Default Passwords, No Segmentation, No Visibility.
critical-infrastructure
Five federal and industry reports from December 2023 to May 2024 trace water and energy sector breaches to the same root causes: default passwords, flat networks, and no OT visibility.
From Our Desk
CISA is telling operators of critical infrastructure to tighten basic cyber hygiene during Cybersecurity Awareness Month. The piece matters because it points to defensive steps for organizations that run essential services and likely raises the priority of patching, access control, and incident readiness.
Regulation & Enforcement
ai-security
GitLab is telling customers to patch a critical vulnerability in its AI Gateway. For defenders, the immediate issue is exposure in a vendor product used to manage AI workloads, so the priority is patching, checking whether the gateway is exposed, and reviewing any dependent systems that may inherit the risk.
Vulnerabilities & Exploitation
Google has delayed a public release of a new AI model after concerns that wider access could increase cyberattack risk. For defenders, the important issue is not the model itself but the likelihood that advanced AI capabilities will be withheld or restricted because they could lower the bar for abuse, phishing, or other offensive use.
Critical Infrastructure & OT
The piece appears to warn that AI agents can keep access to business data and continue acting on a user’s behalf after setup. For defenders, that raises questions about access control, privilege cleanup, and whether AI assistants are being granted more authority than they should have.
Regulation & Enforcement
Google is arguing that AI is speeding up vulnerability discovery, which matters because defenders will need to assume more bugs are found and weaponized faster. The practical impact is higher pressure on patching, triage, and validation of security findings, even if the piece is more about industry trends than a single incident.
Vulnerabilities & Exploitation
endpoint
This describes malware that hides its command traffic inside what looks like normal Google STUN traffic to control infected IoT devices. For defenders, the main issue is stealthy network abuse on compromised devices, which raises monitoring, detection, and containment priorities for IoT estates.
Vulnerabilities & Exploitation
network-security
A Citrix NetScaler SAML flaw is causing crashes and appears to be attracting exploitation attempts. For defenders, the immediate issue is exposure of internet-facing access gateways and the need to confirm patch status, monitor for abnormal crashes, and look for signs of probing or follow-on compromise.
Vulnerabilities & Exploitation
email-security
Fortinet FortiMail has a vulnerability that is already being exploited, which makes it an immediate defensive priority for mail security teams. CISA adding it to the Known Exploited Vulnerabilities list raises the obligation to identify exposed systems, patch quickly, and verify whether any mail gateways were already touched.
Vulnerabilities & Exploitation
cloud-security
This appears to describe an espionage backdoor using Microsoft Outlook and OneDrive as command-and-control channels. For defenders, the issue is the abuse of common cloud and email services for covert communications, which raises the priority on monitoring tenant activity, outbound traffic, and suspicious mailbox or file access in the affected region.
Threat Actors & Campaigns
data-breaches
A data-breach settlement tied to AT&T has cleared court approval, putting a large payout behind claims from users affected by the incident. For defenders, the main takeaway is that breach response now carries clear financial and legal exposure, not just notification and remediation costs.
Regulation & Enforcement
government
The city is still restoring systems after a cyberattack, which puts basic municipal services and public operations at risk until recovery is complete. For defenders, the immediate question is whether this was a disruption-only incident or one with data exposure or malware persistence that could prolong recovery.
Breaches & incidents