
Cyber Security Briefing Briefing — October 4, 2026
Sunday, October 4, 2026
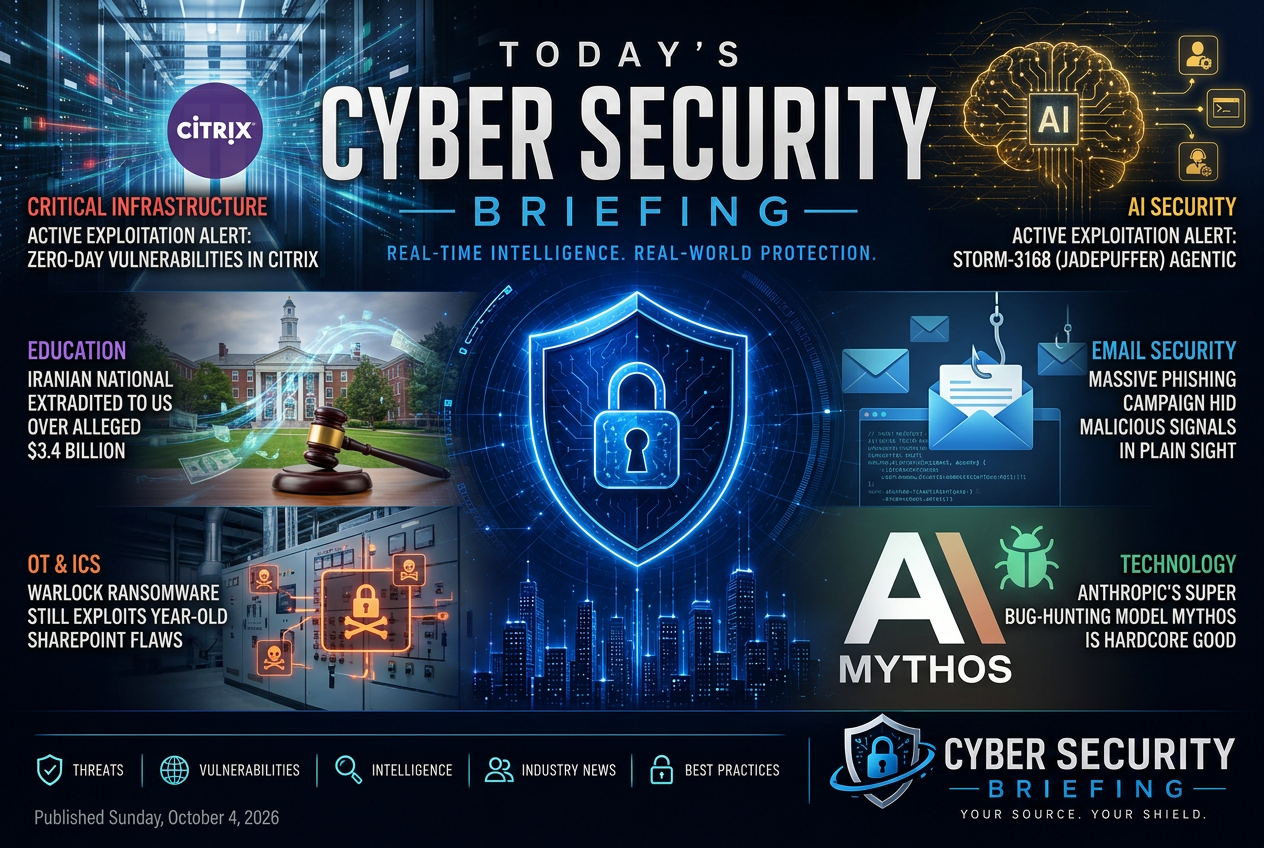
Today's briefing brings you 10 stories across critical infrastructure, education, ai security and email security from the global cybersecurity industry. Leading today: Active Exploitation Alert: Zero-Day Vulnerabilities in Citrix NetScaler and Kiteworks Impact Critical Infrastructure (CVE-2026-88771, CVE-2026-88772) - Rescana.
critical-infrastructure
Citrix NetScaler and Kiteworks are reported to be under active exploitation through zero-day flaws. For defenders, this raises immediate exposure for internet-facing infrastructure and for any critical services that rely on these products, so patching, mitigation, and hunting for compromise move to the top of the queue.
Critical Infrastructure & OT
Warlock ransomware is still reaching critical infrastructure by abusing older SharePoint vulnerabilities that remain exposed. For defenders, the point is less about a new flaw than the operational cost of delayed patching and the continued risk to internet-facing collaboration systems used in essential environments.
Critical Infrastructure & OT
education
This is a law-enforcement and accountability story, not a new intrusion report. It matters because the alleged campaign targeted universities at scale and the extradition suggests prosecutors are trying to turn attribution into enforcement, which raises the stakes for state-linked operators and the institutions they hit.
Regulation & Enforcement
ai-security
The piece says attackers are actively abusing compromised Azure service principals in an agentic campaign tied to Storm-3168, which makes identity and cloud access controls the immediate defensive priority. Defenders should treat service principal hygiene, privilege review, and detection for unusual Azure control-plane activity as urgent rather than routine hardening.
Vulnerabilities & Exploitation
The piece appears to tie a vulnerability already under attack to Anthropic’s bug-hunting model, so the defender takeaway is about whether AI-assisted analysis is helping prioritize exposure fast enough. For security teams, the practical issue is triage and response to an exploited flaw, not the model itself.
Regulation & Enforcement
Apple is tightening macOS Full Disk Access controls in response to the risk that AI agents could be used to reach sensitive local data. For defenders, this is an endpoint and AI-security issue because it changes how much privilege automation and assistant tools should have on managed Macs.
AI Security
email-security
A phishing campaign is being described as having hidden its malicious activity in ways that made it harder to spot. For defenders, the issue is email security and identity protection, because the operational question is how such lures bypassed normal detection and what controls need tightening.
Regulation & Enforcement
Microsoft is reissuing an Exchange Server update after finding another security flaw. For defenders, the immediate issue is patch exposure on Exchange systems and the need to verify whether the new update closes a weakness that could affect mail services or adjacent identity infrastructure.
Vulnerabilities & Exploitation
identity-access
Fortra says it has patched critical flaws in BoKS, which matters because exposed access-control software can become an entry point into privileged systems. Defenders using the product should verify patch status and look for any signs the weaknesses were reached before remediation.
Vulnerabilities & Exploitation
healthcare
Epic is pausing product development because of cybersecurity concerns. For defenders, that signals a security issue serious enough to affect product delivery and should be read as an operational risk for customers and partners, even though the excerpt does not say whether this stems from a breach, vulnerability, or internal control problem.
Regulation & Enforcement