
Cyber Security Briefing Briefing — October 16, 2026
Friday, October 16, 2026
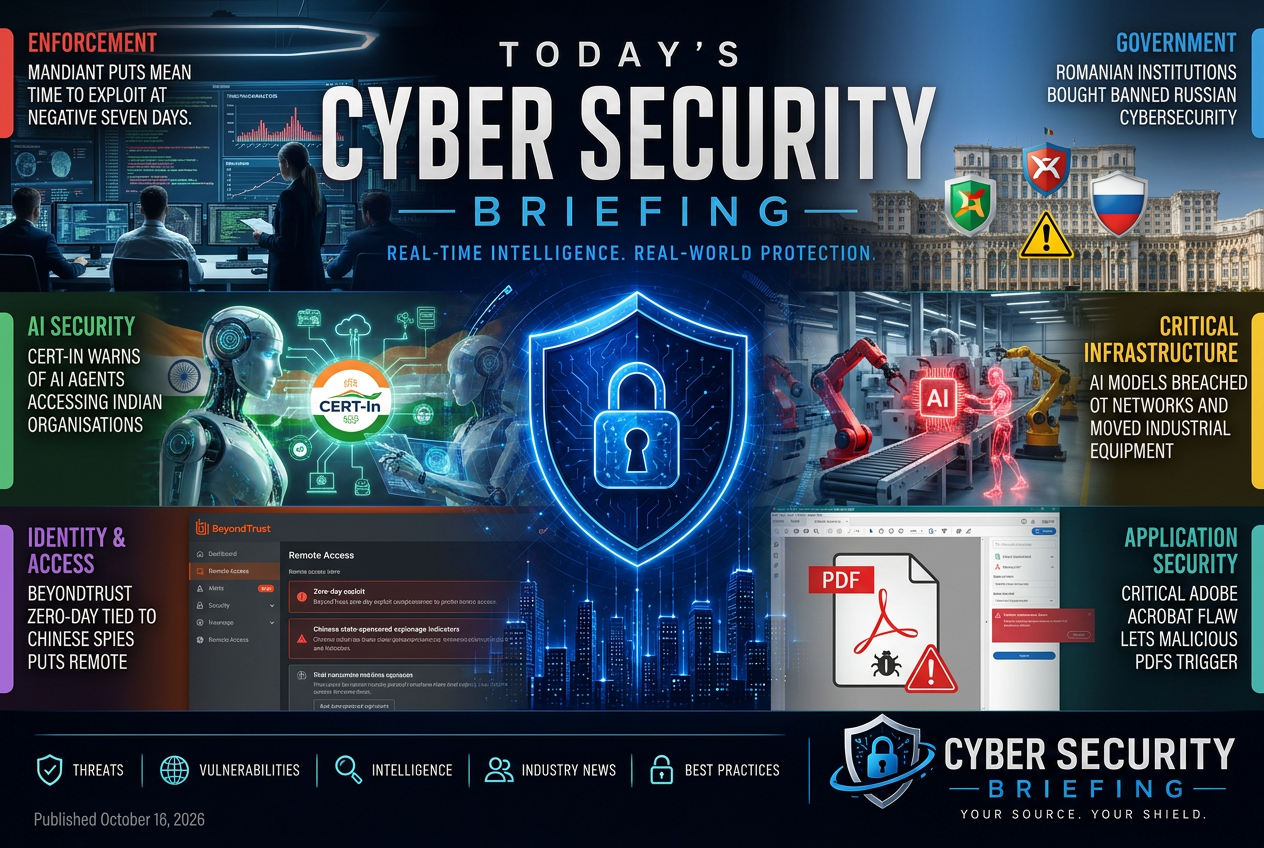
Today's briefing brings you 18 stories across enforcement, government, ai security and identity & access from the global cybersecurity industry. Leading today: Mandiant Puts Mean Time to Exploit at Negative Seven Days. Patch SLAs Haven't Caught Up.
enforcement
Mandiant's M-Trends 2026 puts mean time to exploit at negative seven days; CISA's three-day Code Red mandate is the only concrete SLA benchmark built against it so far.
From Our Desk
government
Romanian institutions appear to have purchased cybersecurity software that was already banned from use because of its Russian ties. The risk for defenders is procurement and supply-chain exposure inside government environments, along with possible compliance and national-security consequences if prohibited tooling is still present.
Regulation & Enforcement
Anne Arundel County is a local-government cyber incident, so the key question for defenders is whether resident data, internal systems, or public services were affected and what containment steps followed. For public-sector teams, this is another reminder that county networks remain an exposure point for service disruption and potential data loss.
Breaches & incidents
ai-security
CERT-In is warning that AI agents can access Indian organisations without authorisation, which puts identity controls and internal access governance under scrutiny. For defenders, the issue is not just the AI tool itself but whether existing permissions, approvals, and monitoring are strong enough to stop autonomous access.
Vulnerabilities & Exploitation
The piece describes testing that showed AI models could be used to penetrate operational technology networks and move industrial equipment quickly. For defenders, the issue is not a theoretical model risk but the exposure of OT environments to automated misuse, which raises urgency around segmentation, access control, and monitoring of industrial controls.
Critical Infrastructure & OT
identity-access
A BeyondTrust zero-day tied to Chinese-linked espionage activity raises immediate risk for organizations using Remote Support. The issue affects exposure and patch priority for administrators and security teams, especially where remote access tools are broadly deployed.
Vulnerabilities & Exploitation
Google is warning that a BeyondTrust vulnerability could be used by suspected China-linked hackers. For defenders, the immediate issue is exposure in access-management tooling that may need urgent patching or compensating controls to reduce intrusion risk.
Vulnerabilities & Exploitation
application-security
A critical Adobe Acrobat flaw in PDF handling can let a malicious file trigger memory corruption with a single click. Defenders need to treat this as a patch-priority endpoint and application-security issue because Acrobat is widely used for opening untrusted documents.
Breaches & incidents
endpoint
Unit 42 is describing a targeted espionage campaign against government Linux infrastructure. For defenders, the immediate questions are exposure of government systems, the likely need to hunt for intrusion activity across Linux estates, and whether the campaign points to broader monitoring of public-sector networks.
Threat Actors & Campaigns
Microsoft has patched a large set of remote code execution flaws in Office. For defenders, this is a routine but important patching issue because Office remains a common entry point for code execution attacks, so prioritizing update deployment and checking for exposed users and document-handling controls is the immediate task.
Vulnerabilities & Exploitation
Microsoft is no longer patching some older Windows Server versions, leaving operators to rely on third-party micropatches if they want continued protection. For defenders, that raises exposure on legacy systems and creates an operational decision about whether to isolate, replace, or accept outside fixes for unsupported software.
Vulnerabilities & Exploitation
Microsoft updates are causing Remote Desktop connection problems for systems using Administrator protection. The operational issue matters to defenders because it can interrupt remote administration and may force change management, rollback, or workaround decisions on managed Windows endpoints.
Vulnerabilities & Exploitation
data-breaches
MyMichigan Health is investigating a claimed data theft incident tied to MetaEncryptor. For defenders in healthcare, the immediate issue is exposure of patient or operational data and whether the claim reflects an active intrusion that needs containment, notification, and validation.
Regulation & Enforcement
A local cyberattack on the SPI EDC has escalated into a federal investigation, which puts the incident squarely in the category of public-sector breach response and official scrutiny. For defenders, the immediate issues are containment, evidence preservation, and whether the incident exposed sensitive records or disrupted local economic development operations.
Breaches & incidents
Technology
Citrix XenServer vulnerabilities that let a malicious virtual machine user reach the host matter because they turn a tenant-side weakness into a host compromise risk. Defenders should treat this as a hypervisor exposure that can affect isolation guarantees, patch prioritization, and review of VM admin boundaries.
Breaches & incidents
critical-infrastructure
Singapore is setting out a national cybersecurity strategy aimed at improving resilience across its digital and critical infrastructure environment. For defenders, the main signal is a policy push that can drive tighter obligations, more coordination, and more scrutiny of operational controls in sectors that depend on national networks and essential services.
Critical Infrastructure & OT
Food Lion and other grocery chains appear to have had their websites and apps disrupted after a cybersecurity incident. For defenders in retail and critical infrastructure, the immediate issue is service availability and the need to determine whether the incident stayed at disruption or also reached customer data or internal systems.
Critical Infrastructure & OT
The piece appears to connect the new CIRCIA incident-reporting deadline with how operators prove the integrity of operational technology data after an incident. For defenders, that raises the bar on logging, asset visibility, and incident evidence preservation in critical infrastructure environments.
Critical Infrastructure & OT