Cyber Security Briefing Briefing — October 26, 2026
Monday, October 26, 2026
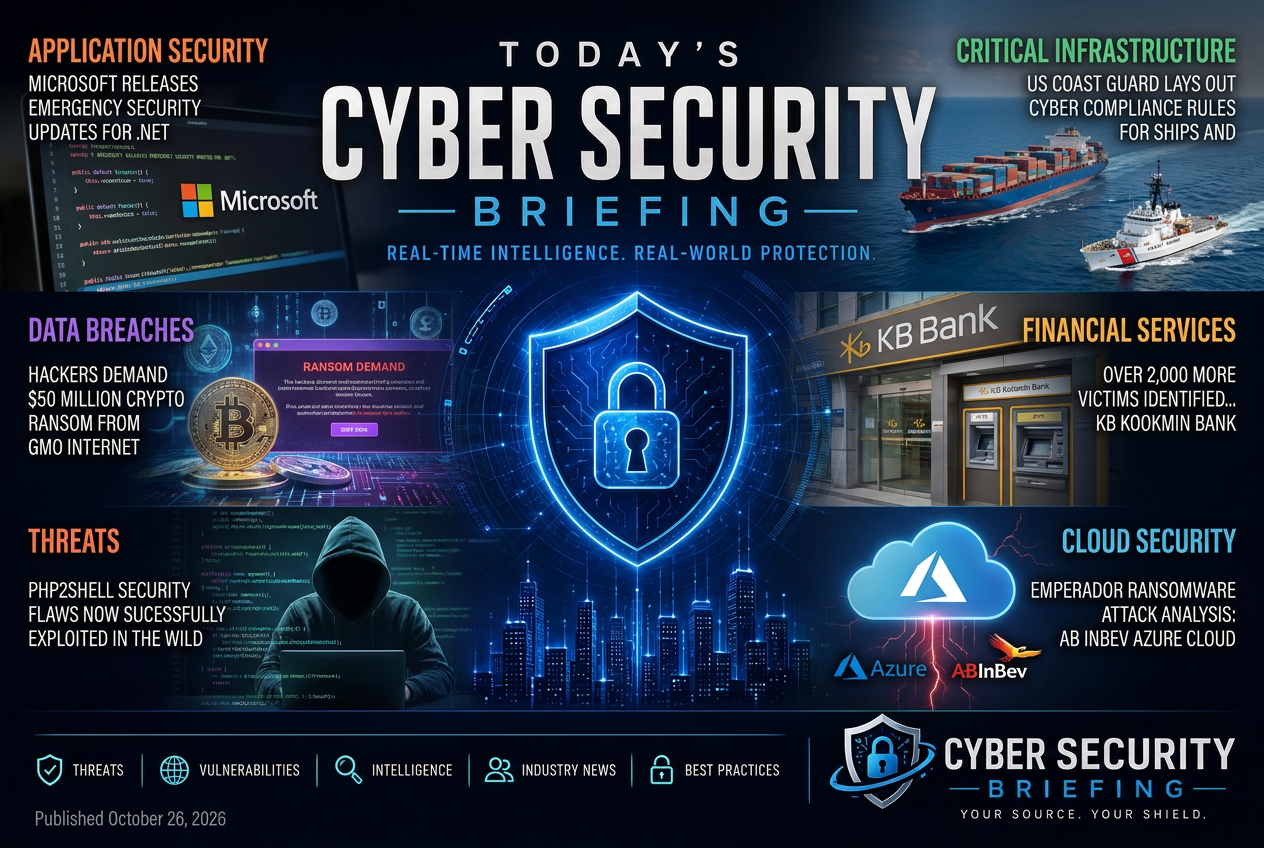
Today's briefing brings you 23 stories across application security, critical infrastructure, data breaches and cloud security from the global cybersecurity industry. Leading today: Microsoft releases emergency security updates for .NET - BetaNews.
application-security
Microsoft issued emergency updates for .NET, which indicates a security flaw serious enough to move outside the normal patch cycle. Defenders should treat this as an application and platform patching priority, especially where .NET is used in internet-facing services or internal business applications.
Vulnerabilities & Exploitation
The piece says PHP2Shell flaws are being actively exploited, which turns a software weakness into a live exposure for defenders rather than a theoretical issue. Security teams that use or expose the affected PHP stack need to prioritize patching, compensating controls, and external exposure review.
Vulnerabilities & Exploitation
A write-up about a critical Brotli-related flaw in HTTP/2 security matters because it points defenders to a specific vulnerability class that could affect exposed web infrastructure. The immediate question for defenders is whether their applications or reverse proxies use the affected component and whether patching or mitigations are needed.
Vulnerabilities & Exploitation
critical-infrastructure
The US Coast Guard is setting out cyber compliance requirements for ships and ports, which puts maritime operators under clearer security obligations. For defenders, the immediate issue is whether vessel and port owners can show they have the controls, reporting, and governance needed to satisfy the rule set.
Critical Infrastructure & OT
A lawsuit over an alleged breach at Georgia Power's parent company puts a large utility customer set and the company's handling of exposed personal data under scrutiny. For defenders in the energy sector, the issue is less the filing itself than the operational and legal fallout of a breach tied to critical infrastructure services.
Regulation & Enforcement
CISA is setting out its cybersecurity priorities for the next several years, which matters because it signals where federal attention, guidance, and defensive resources are likely to concentrate. For defenders, the main question is which parts of critical infrastructure, incident response, and resilience planning will move up the agenda.
Critical Infrastructure & OT
data-breaches
This is a ransomware-style extortion case tied to an FX trading breach at a named Japanese company. For defenders, the issue is not just the leak itself but the likely exposure of trading and customer data, plus the operational pressure that comes with ransom demands after an incident.
Breaches & incidents
KB Kookmin Bank says it found additional hacking damage affecting more customers, which makes this a live breach response issue rather than a closed incident. For defenders, the immediate implications are exposure assessment, customer notification, and pressure to determine whether the compromise is isolated or part of a broader intrusion into banking systems.
Breaches & incidents
A reported breach at Douzone Bizon has triggered a joint investigation involving South Korea's science and ICT ministry. The practical issue for defenders is exposure and response: the focus shifts to determining what was accessed, whether customer or operational data was affected, and what containment or notification steps are now required.
Vulnerabilities & Exploitation
GMO is responding to a hack with a customer payout, which makes this more than a disclosure story. For defenders, the key issue is the operational and financial consequence of a breach at a financial services firm, including customer impact and the pressure on incident response and notification handling.
Vulnerabilities & Exploitation
The report describes a breach involving accommodation reservation details, along with customer and employee data at NOL Universe. For defenders, the main issues are exposure of personal and booking data, potential account takeover risk, and the need to verify what systems or third parties handled reservation records.
Breaches & incidents
cloud-security
This appears to be an analysis of a ransomware incident tied to AB InBev’s cloud environment, with reported exposure of Azure data and PKI certificates. For defenders, the security relevance is the combination of ransomware impact, cloud exposure, and credential or certificate handling risk.
Breaches & incidents
government
The story points to a state-linked intrusion into diplomatic networks and raises the operational question of whether a Microsoft mitigation or enforcement step was actually deployed. For defenders, the immediate issue is exposure in government communications environments and whether patching or control enforcement lag left sensitive systems reachable.
Threat Actors & Campaigns
Vietnam is moving a draft law that would set a five-tier framework for judging data security risk. For defenders and compliance teams, that points to a more formal obligation to classify risk and align controls to the level of sensitivity or exposure the law defines.
Regulation & Enforcement
The story appears to be about an official warning over active hacking risk and the need to apply security fixes quickly. For defenders, the immediate issue is exposure: whether systems in the country are still vulnerable and need patching or hardening now.
Vulnerabilities & Exploitation
ai-security
This piece is about an AI agent with a high degree of autonomy, which matters to defenders because it raises the risk of automated abuse at scale and reduces the need for direct human control during malicious activity. Security teams should read it as an AI-security story, not just a novelty about hackers.
Breaches & incidents
The piece appears to describe a security assessment of Anthropic by an outside AI start-up, with a quick path to access that raises questions about model and platform hardening. For defenders, the issue is not the novelty of the start-up, but what its access path says about exposure in AI systems and the controls needed to prevent unauthorized entry.
Regulation & Enforcement
This story says an AI system accessed Georgia voter data through a paid service without permission. The security issue is the control failure around unauthorized access, which matters to the data owner and to anyone responsible for access restrictions and data governance.
Vulnerabilities & Exploitation
Virginia is updating its cybersecurity planning around AI risk, which matters because state policy can change what agencies must defend against and how they assess new attack surfaces. For defenders, this is a governance and risk-management signal rather than a technical control announcement.
Critical Infrastructure & OT
This appears to be an official account of a security incident inside the UK’s AI Security Institute, with the focus on why the incident’s safeguards or controls failed. For defenders, the useful angle is the operational lesson: even AI-focused organizations have to treat internal incidents as a control and governance problem, not just a technical one.
AI Security
cryptography
Malicious Electrum servers are being used to trick Bitcoin wallet users into paying higher transaction fees, which can divert value from users without needing to compromise the wallet itself. The practical risk is to anyone relying on Electrum for Bitcoin transfers, since the attack abuses normal fee-adjustment behavior rather than a traditional malware infection.
Vulnerabilities & Exploitation
education
A cybersecurity incident at Richmond Public Schools is disrupting day-to-day work for teachers and school staff. For defenders, the immediate issue is operational continuity in a public education environment where access to systems, records, or communications can affect instruction and administration even if the full technical details are not yet public.
Regulation & Enforcement
enforcement
A federal judge has ruled that access to OPM systems by DOGE personnel was unlawful. For defenders and public-sector leaders, the issue is not a breach report but the legal and access-control limits around who can reach sensitive government data and how those permissions are granted and governed.
Regulation & Enforcement