Cyber Security Briefing Briefing — October 27, 2026
Tuesday, October 27, 2026
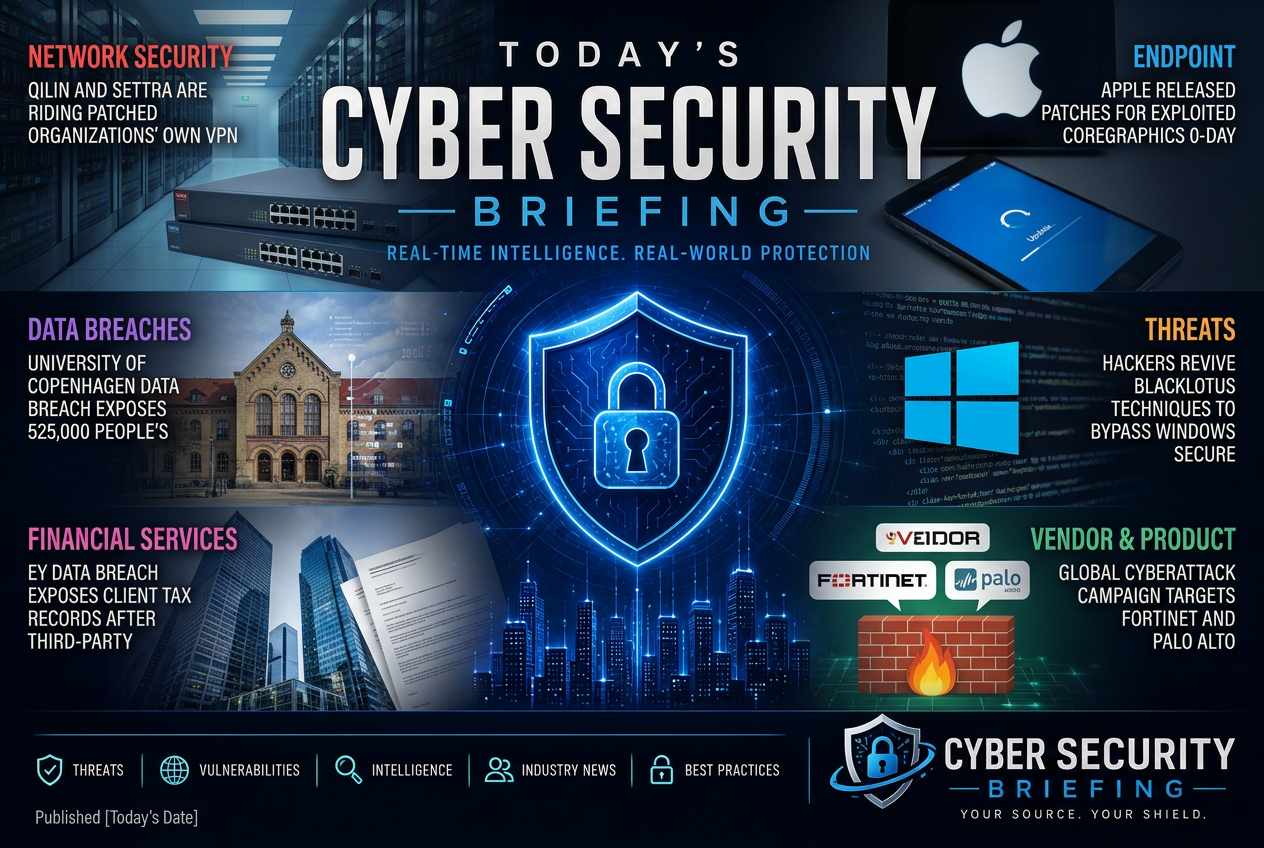
Today's briefing brings you 17 stories across network security, endpoint, data breaches and ai security from the global cybersecurity industry. Leading today: Qilin and Settra Are Riding Patched Organizations' Own VPN Sessions Through CVE-2026-0257.
network-security
Qilin and Settra affiliates are exploiting CVE-2026-0257, a PAN-OS GlobalProtect bypass, to open MFA-free VPN sessions that evade standard detection rules.
From Our Desk
The headline points to a coordinated attack campaign against edge firewalls from major vendors. For defenders, the immediate issue is exposure at perimeter devices that sit in front of internal networks, which raises priority for patching, configuration review, and threat hunting on exposed appliances.
Regulation & Enforcement
endpoint
Apple has patched an actively exploited CoreGraphics zero-day affecting older iPhones. For defenders, the main issue is exposure on devices that may lag on updates, which turns this into a patch-priority item for mobile fleet owners and a reminder to verify remediation on legacy Apple hardware.
Vulnerabilities & Exploitation
This piece is about attackers reusing BlackLotus bootkit techniques to get around Windows Secure Boot and load malware. The defender impact is clear: secure boot protections are not enough on their own if an attacker can reach the boot chain, so patching, device hardening, and boot integrity checks matter here.
Threat Actors & Campaigns
data-breaches
The report describes a personal-data breach at the University of Copenhagen that exposed information on a large number of people, including phone numbers. For defenders in education, the immediate lesson is exposure of student, staff, or research-adjacent records and the need to review access controls, logging, and notification duties.
Breaches & incidents
EY is reporting a breach that exposed client tax records after a compromise of a third-party platform. The security impact is a disclosure of sensitive client data and a reminder that vendors and service providers can become the entry point for regulated information loss.
Breaches & incidents
UltraMobile Imaging says a data breach exposed information tied to 75,000 people. For defenders, the immediate issue is exposure of personal data and the need to confirm what records were taken, how the intrusion happened, and whether notification or containment obligations apply.
Regulation & Enforcement
A credit union is being held financially liable after a data breach, which points to regulatory or legal consequences beyond the incident itself. For defenders, the story is a reminder that breaches can turn into direct enforcement costs as well as notification and remediation work.
Regulation & Enforcement
Austin ISD says staff data was compromised in a software breach. For defenders, the immediate questions are what data was exposed, whether any accounts or systems were affected, and whether other districts using the same software need to review their exposure and response plans.
Breaches & incidents
Keystone says it will destroy a large number of older devices after a data breach. For defenders, the immediate issue is whether exposed records or device data were accessible through those systems, and whether the incident creates follow-on risk for customers or internal access controls.
Breaches & incidents
ai-security
Amazon is being reported as unwilling to patch a critical flaw in its AI model server, which leaves customers and operators to manage the exposure themselves. For defenders, that means the priority shifts to compensating controls, access restriction, monitoring, and fast migration away from the affected deployment if they rely on it.
Vulnerabilities & Exploitation
enforcement
California’s settlement with 23andMe matters because it extends the company’s legal and operational fallout beyond the original incident. For defenders and compliance teams, it is a reminder that consumer genetics data can create long-tail regulatory and breach-response obligations even after the immediate crisis fades.
Regulation & Enforcement
identity-access
The story reports a vulnerability in HashiCorp Consul that can let an attacker bypass authorization and raise privileges. For defenders, this is a software risk that can turn into unauthorized access if Consul is exposed or misconfigured, so patching and access review are the immediate priorities.
Vulnerabilities & Exploitation
cloud-security
DreamHost says it is forcing password resets for email and FTP accounts after an unexplained security incident. For defenders, this is an exposure and response issue: hosted account access may have been at risk, and administrators should treat credential hygiene, multifactor authentication, and account review as immediate priorities.
Breaches & incidents
application-security
This piece appears to downshift the immediate risk around a critical Brotli decompression flaw rather than describing a confirmed active intrusion. For defenders, the issue is still relevant because compression libraries are widely embedded in application stacks, so even a debated severity level can affect patch priority and exposure review.
Vulnerabilities & Exploitation
This is a vendor analysis of the PHP2Shell exposure and the gap between alarm and actual patching. For defenders, the point is not the naming of the flaw but the operational lesson: exposure remains high until organizations move from awareness to remediation, especially for internet-facing PHP deployments.
Vulnerabilities & Exploitation
government
South Carolina is rolling out a cybersecurity pilot aimed at rural hospitals. For defenders, the immediate issue is better protection for healthcare systems that often have limited security staff and budget, and a clearer signal that state support is being used to reduce exposure in a high-risk sector.
Breaches & incidents