Cyber Security Briefing Briefing — October 28, 2026
Wednesday, October 28, 2026
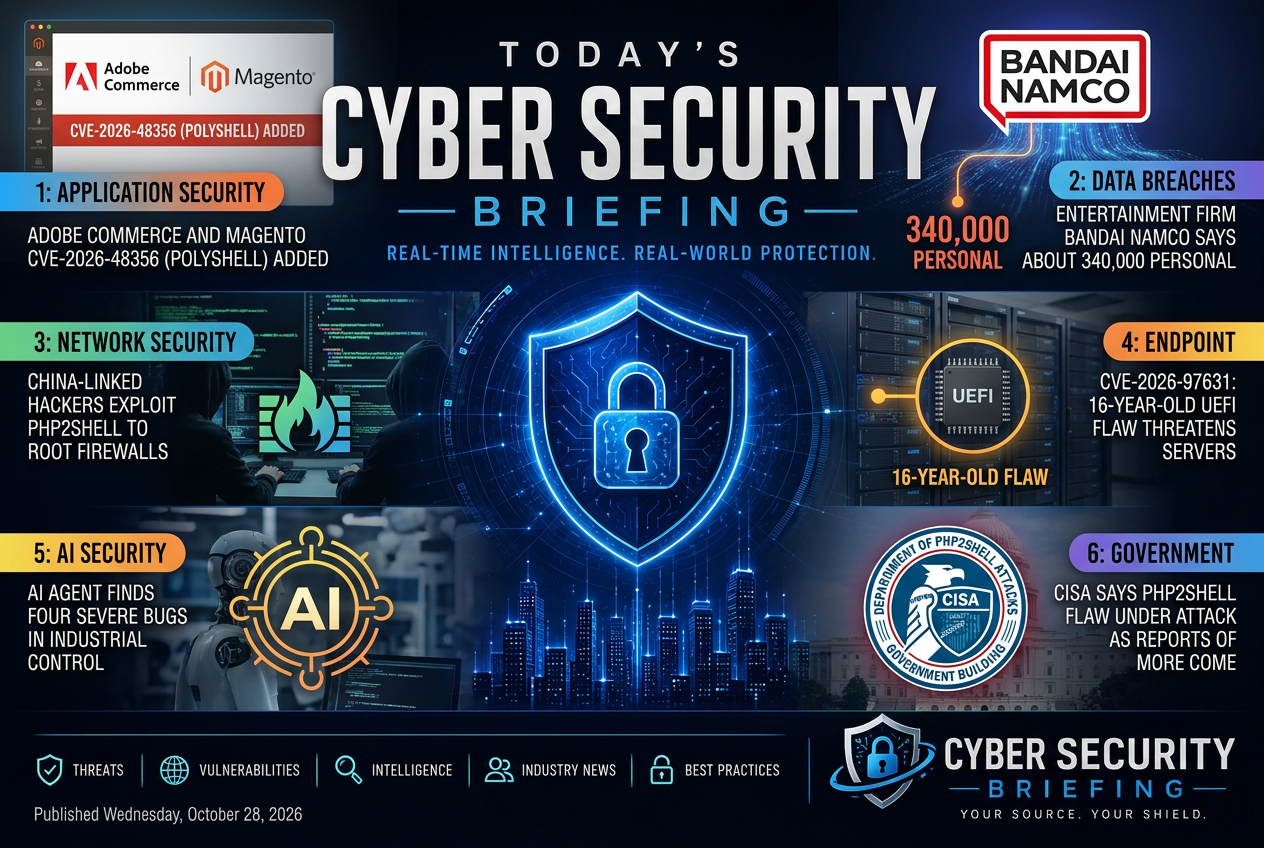
Today's briefing brings you 22 stories across application security, data breaches, network security and endpoint from the global cybersecurity industry. Leading today: Adobe Commerce and Magento CVE-2026-48356 (PolyShell) Added to CISA KEV: Apply APSB26-73 and Check for Planted Files - Rescana.
application-security
CISA has added Adobe Commerce and Magento CVE-2026-48356 to its known exploited vulnerabilities list, which means defenders need to treat this as an active risk rather than a theoretical flaw. The immediate operational question is whether affected sites have been patched with Adobe's APSB26-73 update and whether any planted files or persistence artifacts are already present.
Vulnerabilities & Exploitation
CISA says a PHP2Shell flaw is being actively attacked, which puts PHP-based systems and the teams that patch them under immediate exposure pressure. The story matters because it signals real-world exploitation, so defenders need to verify whether affected assets are present and prioritize mitigation over routine patch queues.
Vulnerabilities & Exploitation
A critical flaw in GoAhead affects certificate revocation handling for mutual TLS, which means systems may continue trusting certificates that should no longer be valid. That raises the risk of unauthorized access for any organization using the affected server software to gate sensitive services.
Vulnerabilities & Exploitation
A Brotli vulnerability with a Node.js angle is being described as affecting more than one runtime, which makes this a broader application-security issue rather than a single-package bug. For defenders, the immediate question is where Brotli is embedded in exposed services and whether that code path can be reached before patches are in place.
Vulnerabilities & Exploitation
data-breaches
Bandai Namco says personal records were exposed in a data breach affecting a large number of people. For defenders, this is a reminder that consumer-facing firms can still face material exposure from incidents that hit personal data rather than systems availability.
Breaches & incidents
Moldova’s e-government agency says a cyberattack appears to have put national identity data at risk, with a large set of IDNP records allegedly extracted. For defenders, this is a government data-breach case with clear identity-theft and public-sector exposure, and it raises questions about containment, notification, and the integrity of citizen records.
Breaches & incidents
Coinbase says customer data was exposed through a security incident at its analytics vendor, which shifts this from a vendor issue to a customer-data exposure problem for a major financial platform. Defenders should treat third-party telemetry and analytics access as part of the attack surface and review what customer information those vendors can see.
Ransomware & Extortion
network-security
The story says China-linked actors are using a PHP vulnerability to gain root access on firewalls. That puts perimeter devices at immediate risk and raises the priority of patching, exposure review, and monitoring for compromise on internet-facing network gear.
Vulnerabilities & Exploitation
endpoint
A long-lived UEFI flaw that can affect servers matters because it sits below the operating system and can undermine patching, boot integrity, and recovery. Defenders should treat it as a hardware-firmware exposure with priority for server fleets, especially where secure boot and remote management are in scope.
Vulnerabilities & Exploitation
A public exploit has been released for an unpatched Linux kernel vulnerability. That raises immediate exposure for any organization still running affected systems, because defenders now need to assume active weaponization and prioritize patching, isolation, and hunting for signs of compromise.
Vulnerabilities & Exploitation
This is about a bootkit that can get around Secure Boot by abusing a specific UEFI flaw. For defenders, that raises the priority of firmware-level patching, boot-chain integrity checks, and hunting for persistence that survives normal endpoint cleanup.
Threat Actors & Campaigns
ai-security
An AI system reportedly found multiple severe flaws in industrial control software in a short window. For defenders, the issue is not the speed of the discovery but the exposure it suggests in OT software that could affect safety, availability, and patch priority.
Critical Infrastructure & OT
A reported AI agent was used in a way that resembles a supply chain attack, including fake accounts to distribute malware. For defenders, the issue is not just model misuse but the risk that autonomous tooling can be turned into a delivery channel for malicious software and account abuse.
AI Security
Researchers say they found a flaw in OpenAI's API that let them extract hidden reasoning traces from GPT-5.6. For defenders, this is an AI-security exposure because it suggests sensitive model output can be exposed through the application layer, which can affect privacy, model hardening, and vendor assurance.
Vulnerabilities & Exploitation
Anthropic is signaling security and operational issues in the course of an IPO filing, which makes the disclosure relevant to defenders as a corporate risk and governance matter rather than a product announcement. The key takeaway is that even major AI vendors are now having to describe security breaches and training disruptions in public filings, which raises scrutiny of how they protect model pipelines, internal systems, and sensitive data.
AI Security
government
An Ohio state office appears to have been hit by a cyberattack, with officials suggesting foreign involvement. For defenders, the relevant issue is service disruption and the possibility that a public-sector compromise may still be under investigation while the source and method are not yet confirmed.
Breaches & incidents
email-security
Italian lawmakers’ email systems are being targeted in a cyberattack that includes accounts linked to Prime Minister Giorgia Meloni. The immediate concern for defenders is mailbox compromise, credential theft, and the possibility of follow-on access to government correspondence.
Breaches & incidents
threats
Security teams need to assume exposed Oracle systems are being actively targeted soon after patch release. The immediate task is to verify exposure, confirm the fix is applied everywhere, and look for signs that systems were probed before patching.
Vulnerabilities & Exploitation
critical-infrastructure
The story appears to focus on a cyberattack affecting a French supermarket and the security risk created by ageing operational technology. For defenders, the relevant issue is exposure in legacy OT environments, especially where retail operations depend on older systems that are harder to patch and monitor.
Critical Infrastructure & OT
The story appears to connect a cyberattack on Colmobil to broader weaknesses in Israel’s connected-car environment. For defenders, the main issue is exposure across a transport-adjacent ecosystem where a single incident can affect multiple systems, vendors, and vehicle-linked services.
Ransomware & Extortion
cloud-security
The story appears to involve a travel scam that followed a cyberattack on RMS Cloud, with Australian travellers being targeted through fraudulent hotel booking messages. The defender-facing issue is exposure of booking data and the downstream fraud risk for customers and hospitality operators.
Breaches & incidents
education
A cyber incident has disrupted a university health operation and forced class cancellations, which makes this an operational continuity issue rather than a narrow IT event. Defenders should treat it as a reminder that campus health systems can have wider blast radius across care delivery, scheduling, and student services.
Regulation & Enforcement