Cyber Security Briefing Briefing — October 29, 2026
Thursday, October 29, 2026
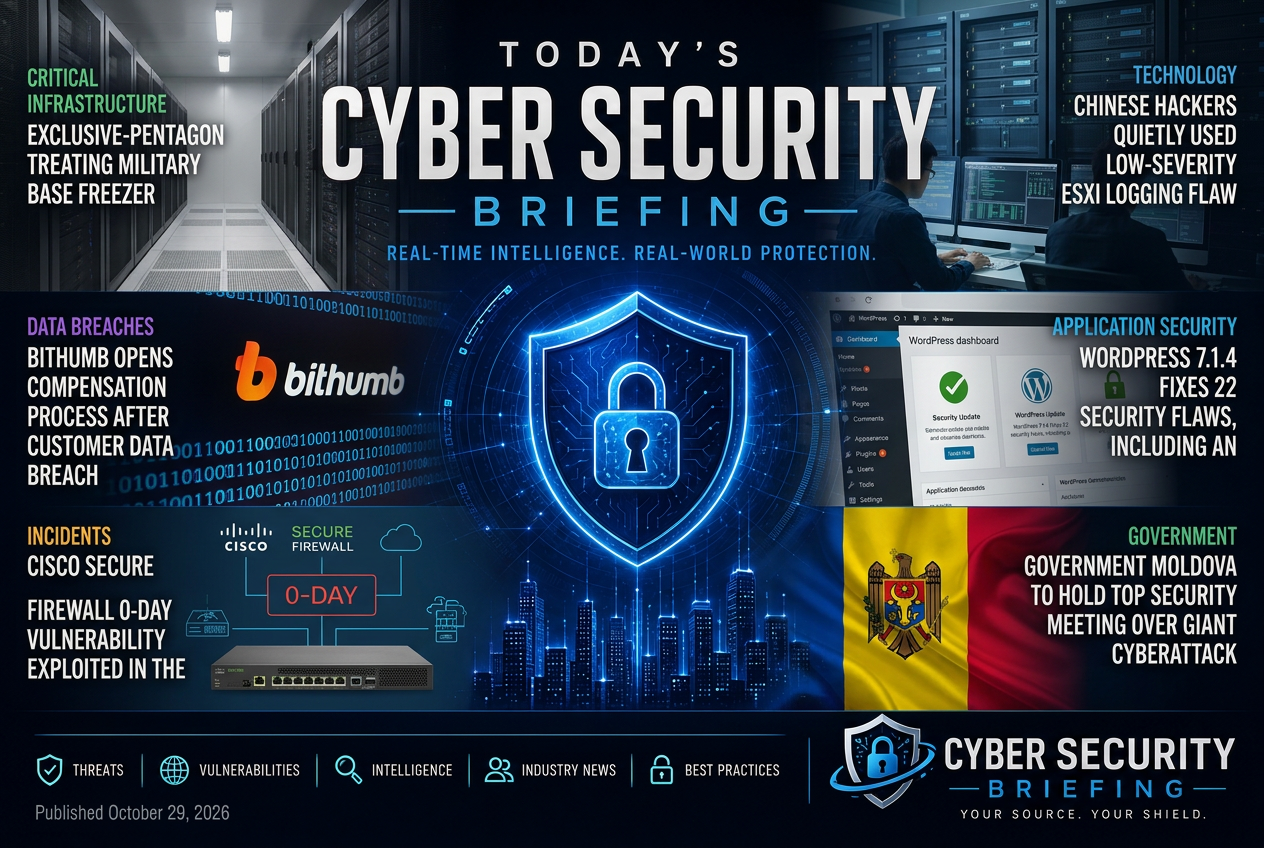
Today's briefing brings you 23 stories across critical infrastructure, data breaches, technology and incidents from the global cybersecurity industry. Leading today: Exclusive-Pentagon treating military base freezer malfunctions as suspected cyberattack, officials say - Forth.News.
critical-infrastructure
The Pentagon is treating freezer failures at military bases as a possible cyber incident, which puts a routine facilities problem into the realm of operational security. For defenders, the key question is whether building systems and OT assets were interfered with, because even a narrow incident can affect mission readiness and raise reporting and containment obligations.
Critical Infrastructure & OT
The Federal Election Commission took its systems offline after a cyberattack, which puts a government body responsible for election oversight into incident response mode. The immediate defender concern is service disruption, containment, and whether any sensitive records or administrative systems were accessed before shutdown.
Critical Infrastructure & OT
This piece appears to cover new research on Volt Typhoon’s covert infrastructure and what that means for defenders watching for persistent access in critical networks. The security value is in understanding how the group is maintaining a low-profile presence and what detection or hardening gaps that exposes.
Critical Infrastructure & OT
The report ties a cyberattack on Italy’s parliament to broader hybrid warfare concerns. For defenders, the main takeaway is that legislative bodies are part of the critical-government attack surface and may face pressure from politically motivated or state-linked operations rather than ordinary criminal campaigns.
Critical Infrastructure & OT
Hoover is saying it has serious cyber weaknesses to address, which puts municipal systems and services in the frame for remediation. For defenders, the immediate issue is exposure in local government infrastructure and the obligation to prioritize fixes before those gaps become an incident.
Critical Infrastructure & OT
data-breaches
Bithumb is moving into customer compensation after confirming a data breach. For defenders, the issue is not just disclosure but the operational fallout: exposed customer data can drive fraud, account takeover attempts, and follow-on support burden, especially for a financial services platform.
Breaches & incidents
A data breach has exposed the identities of immigration agents despite DHS protection. The security issue is the exposure of sensitive government personnel data, which can raise operational risk, targeting risk, and handling obligations for the agencies involved.
Regulation & Enforcement
Moldova’s election authority says the State Register of Voters was not compromised after a cyberattack. The immediate issue for defenders is confidence in an election-adjacent system and the need to verify whether the intrusion was contained before it could affect voter records or trust in the process.
Breaches & incidents
Technology
The piece says attackers used a VMware ESXi logging flaw as a zero-day, which turns a low-severity issue into a real exposure for defenders running ESXi in production. The practical impact is that teams need to treat even modest-seeming virtualization bugs as potential intrusion paths, especially when exploitation is already in the wild.
Vulnerabilities & Exploitation
incidents
Cisco Secure Firewall devices are being hit by an in-the-wild zero-day that can crash SSL VPN services. For defenders, the immediate issue is service availability and exposure of remote access gateways, with patching and mitigations taking priority over routine maintenance.
Vulnerabilities & Exploitation
This reports a ransomware attack on a major Israeli car importer, which makes the business impact more important than the ransom group’s branding. For defenders, it is a reminder that large distributors and importers can be operationally exposed even when they are not obvious primary targets.
Ransomware & Extortion
application-security
WordPress has issued a security release that closes a large set of flaws, including one that could allow unauthenticated remote code execution. For defenders, the immediate issue is patch priority: internet-facing WordPress sites and any hosted environments that lag on updates need review now because a single platform update may remove several attack paths at once.
Vulnerabilities & Exploitation
A researcher says they found a zero-click flaw in Telegram stickers that could be chained into code execution on iOS. For defenders, this is an application-security issue that raises exposure for Telegram users on Apple devices and warrants patching, detection, and user-risk review once vendor guidance is available.
Vulnerabilities & Exploitation
Researchers say they found a chain of flaws in Cloudflare-related security controls that can be used to bypass content security policy and run malicious JavaScript. The issue matters to defenders because it weakens a browser-side control many teams rely on to reduce the impact of cross-site scripting and similar web attacks.
Vulnerabilities & Exploitation
government
Moldova is treating the cyberattack as a national security issue rather than a routine IT incident. For defenders, the immediate questions are whether critical government systems were disrupted, whether sensitive data was exposed, and what hardening or response measures officials will order next.
Breaches & incidents
financial-services
The Belgian Finance Ministry says a cyberattack took down MyMinfin and other public services. For defenders, the immediate issue is service availability in a government environment that handles sensitive financial and citizen records, which raises questions about containment, recovery, and whether any data was accessed.
Breaches & incidents
cryptography
Lazarus is described as abusing legitimate South Korean security software to deliver malware, which means defenders in that market need to review how trusted local tools can be turned into an execution path. The post-quantum encryption detail suggests the campaign is also trying to make traffic and payload handling harder to inspect, raising the bar for detection and incident response.
Threat Actors & Campaigns
Ethereum client maintainers patched a flaw that could let an attacker alter how ETH rewards are directed. For defenders and operators, the immediate issue is patching and verifying client versions, since the exposure sits in core blockchain software rather than in a user-facing app.
Vulnerabilities & Exploitation
endpoint
CERT-In is warning that Apple device security flaws could let attackers reach stored data, which puts Indian users and organizations on alert for patching and exposure reduction. The practical issue for defenders is straightforward: identify affected Apple devices, verify update status, and prioritize remediation where sensitive data is handled.
Vulnerabilities & Exploitation
The piece describes a vulnerability in Bitcoin node software that can cause Windows and Mac systems to crash. For defenders, that makes this an availability and patch-priority issue for anyone running exposed or mission-critical node infrastructure.
Vulnerabilities & Exploitation
education
UNM is warning the public not to interact with groups claiming responsibility for its cybersecurity incident. The piece is about an active institutional cyber disruption affecting healthcare operations and public communications, which matters to defenders because it points to an ongoing incident with potential social-engineering and attribution risks.
Regulation & Enforcement
ai-security
This appears to be about AI-assisted vulnerability discovery and exploitation research, with a focus on Chrome flaws and a Linux remote code execution path. For defenders, the useful angle is whether the findings translate into patching priorities and whether the work suggests broader exposure in common browsers and Linux systems.
Vulnerabilities & Exploitation
OWASP is describing a security test where an AI tool helped a low-skilled user reach an admin account. For defenders, the issue is not the model itself but the way AI assistance can lower the skill barrier for account takeover, which raises the value of stronger authentication, privilege controls, and monitoring for unusual access patterns.
Vulnerabilities & Exploitation