Cyber Security Briefing Briefing — October 30, 2026
Friday, October 30, 2026
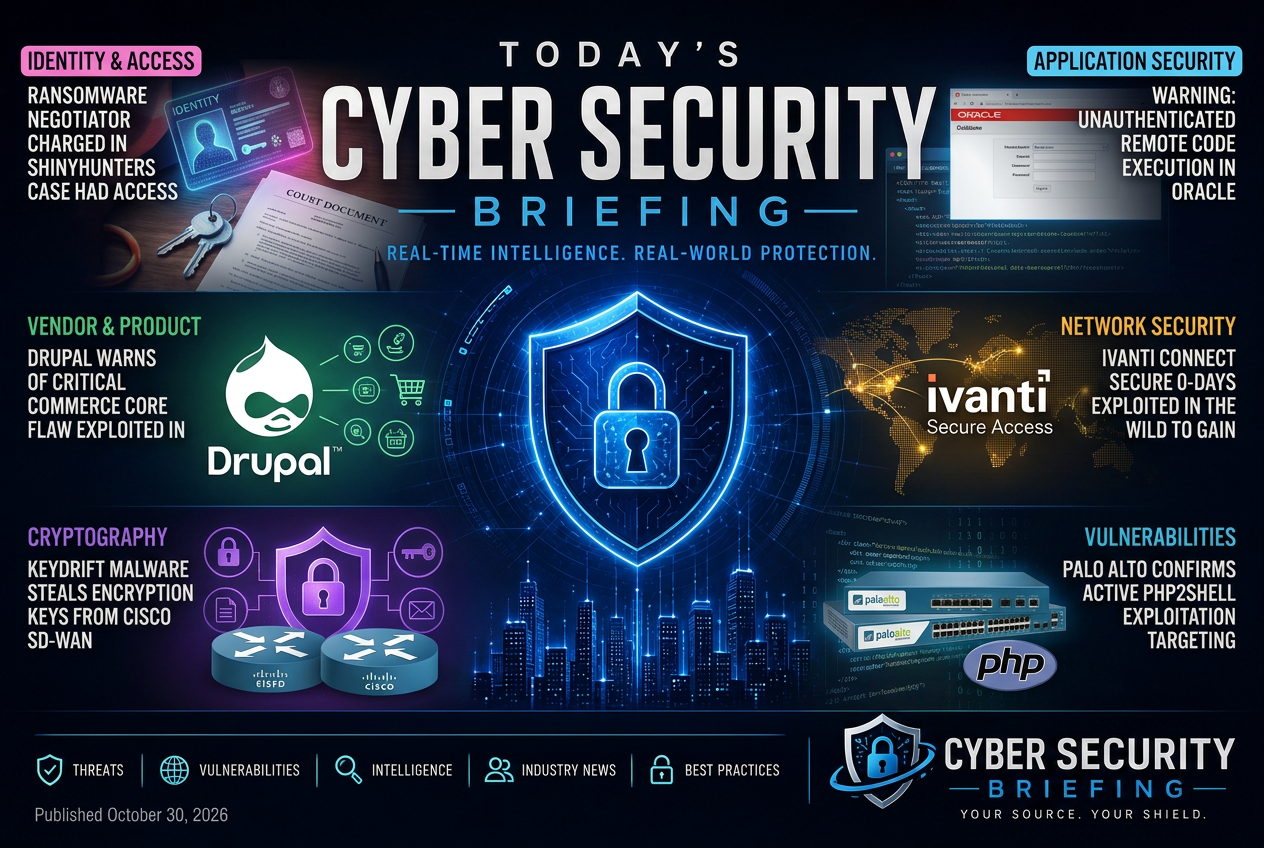
Today's briefing brings you 31 stories across identity & access, application security, network security and cryptography from the global cybersecurity industry. Leading today: Ransomware Negotiator Charged in ShinyHunters Case Had Access to the Clients He Allegedly Betrayed.
identity-access
Edward Dubrovsky, hired to negotiate with ransomware gangs, is now charged with secretly working alongside the ShinyHunters hackers he was paid to counter.
From Our Desk
application-security
Belgium's cybersecurity authority is warning that Oracle E-Business Suite has an unauthenticated remote code execution flaw and is urging immediate patching. For defenders, this is an exposure and priority issue: any internet-facing or externally reachable deployment should be treated as urgent because unauthenticated RCE can lead to full system compromise.
Vulnerabilities & Exploitation
Drupal is warning that a critical flaw in its Commerce Core component is being actively exploited. For defenders, this is a patch-and-verify item because exposed Drupal commerce installations may already be at risk of compromise.
Vulnerabilities & Exploitation
Progress fixed two critical WS_FTP Server flaws in recent releases. For defenders, this is a patch-priority item for any environment that still runs the affected file-transfer software, because exposed file transfer services are a common entry point for intrusion and data theft.
Vulnerabilities & Exploitation
network-security
Ivanti Connect Secure is reported to have active zero-day exploitation that can lead to unauthenticated root access. Defenders using the product should treat this as an urgent exposure issue and prioritize patching, exposure checks, and incident response review.
Vulnerabilities & Exploitation
Palo Alto says attackers are actively targeting exposed PAN-OS management interfaces through PHP2Shell. Defenders need to treat internet-facing management access as a live exposure, tighten access controls, and verify patching and hardening on affected devices.
Vulnerabilities & Exploitation
KISA is warning Synology NAS users about a PHP vulnerability that needs immediate patching. For defenders, the issue is exposure on networked storage devices that often sit inside trusted internal environments and can become a foothold if left unpatched.
Vulnerabilities & Exploitation
This is a kernel vulnerability story, not a general product note. The issue matters because it affects Linux deployments that may be exposed through TCP handling, and the lack of fixes from major downstream vendors means defenders need to track upstream guidance and plan for compensating controls.
Vulnerabilities & Exploitation
A vulnerability disclosure about VMware ESXi audit logging. The security issue appears to let an attacker interfere with or erase evidence, which affects incident response, forensics, and compliance even if the CVSS score is low.
Vulnerabilities & Exploitation
cryptography
The story describes malware inside Cisco SD-WAN controllers stealing encryption keys used to protect network traffic. That raises immediate exposure for network operators because key theft can undermine the confidentiality and trust of traffic flowing through affected SD-WAN deployments.
Vulnerabilities & Exploitation
Trezor says a malicious hardware implant was found in its Safe 5 wallet. That raises supply-chain and device-integrity concerns for cryptocurrency users and for defenders watching for tampering in the hardware security chain.
Vulnerabilities & Exploitation
data-breaches
Cathay Pacific is now part of a broader pattern of airline breaches, which puts passenger and employee data exposure back on the agenda for aviation security teams. The main issue for defenders is not the headline itself but the likelihood of shared weak points across travel systems, third-party services, and account access controls.
Breaches & incidents
This is a data-breach story involving leaked personal data tied to a large U.S. government workforce. For defenders, it highlights exposure of employee records and the operational burden of investigating how the data was obtained and what follow-on phishing or impersonation risk it creates.
Breaches & incidents
This reports an alleged breach involving a bank, with attackers claiming access to PAN and Aadhaar records. For defenders, the immediate issue is exposure of sensitive identity data and the need to verify the claim, assess blast radius, and contain any compromised systems or accounts.
Breaches & incidents
Philippine authorities are looking into a suspected theft of migrant worker records, which makes this a data-breach case with potential identity-theft and privacy consequences. The main issue for defenders is whether a public-sector or labor-related system exposed sensitive personal data at scale, and whether affected workers need notification and monitoring.
Breaches & incidents
A Florida state education website breach exposed Social Security numbers, which turns this into a direct identity-theft and breach-response issue for public-sector defenders. The main questions are what data was exposed, how the site was compromised, and whether state agencies now need to treat this as a broader access and records-security problem.
Regulation & Enforcement
A University of Central Arkansas clinic says it suffered a data breach, which puts patient and administrative records at risk and may trigger notification and response obligations. For defenders in healthcare and higher education, the key issue is exposure of sensitive records rather than a technical flaw.
Breaches & incidents
Police are signaling a possible cyber incident affecting a New Jersey town, which makes this a local government security story rather than a routine IT issue. The immediate question for defenders is whether municipal systems or resident data were touched and what containment steps are now required.
Breaches & incidents
BBC reporting suggests the Asos breach involved more personal data than the company initially disclosed. That raises the exposure for affected customers and the obligation to reassess notification, remediation, and downstream fraud risk.
Ransomware & Extortion
critical-infrastructure
A cyberattack took a solar farm and battery storage system offline in Chile, which is an operational disruption for a piece of energy infrastructure rather than just a reporting headline. The immediate defender concern is service availability, recovery coordination, and whether the incident exposed control systems or remote access paths used to manage the site.
Breaches & incidents
The piece points to a suspected cyber incident affecting refrigeration systems at U.S. military bases, which puts operational continuity and base logistics in scope. For defenders, the relevant issue is OT and critical-infrastructure exposure on government systems, not just a generic intrusion claim.
Critical Infrastructure & OT
The piece is about Volt Typhoon and the risk it poses to infrastructure defenders, not just as espionage but as a preparation problem for operators of critical systems. The practical issue for defenders is exposure across OT and IT environments, where stealthy access can increase the priority on hardening, segmentation, detection, and incident response readiness.
Critical Infrastructure & OT
endpoint
A TeamViewer flaw could let a malicious remote host seize control of a support technician’s machine during a session. The security issue matters because it turns a remote support tool into a path to higher-privilege compromise and wider access inside the defender’s environment.
Vulnerabilities & Exploitation
This piece concerns a Linux kernel privilege-escalation flaw that has been added to CISA's Known Exploited Vulnerabilities list, which raises the urgency for defenders to patch exposed systems. The reported chaining with PHP2Shell means organizations should treat it as an active escalation path, not just a standalone kernel bug.
Vulnerabilities & Exploitation
ai-security
CrowdStrike says it has identified a China-linked campaign that uses AI in the attack chain. For defenders, the point is that AI is now being used to scale or improve hostile activity, which raises the priority on detection, attribution, and controls that can spot unusual automation rather than just known malware signatures.
Threat Actors & Campaigns
Cisco is releasing Quarry as an open-source tool for spotting AI agent attacks that may look like ordinary intermediate actions. For defenders, this is a practical detection and validation issue: it helps security teams look for misuse inside agent workflows rather than only at the final malicious outcome.
AI Security
financial-services
This points to a security incident at Binance that triggered a freeze of a large amount of crypto assets by major stablecoin issuers. For defenders, the operational issue is not price movement but containment, asset tracing, and the ability of counterparties to act quickly when suspicious activity is reported.
Breaches & incidents
Technology
Chrome and Firefox have both shipped security updates that close a large set of vulnerabilities, including several rated critical. For defenders, the immediate issue is patch prioritization across browser fleets and any systems that depend on these browsers for user access or sensitive web applications.
Vulnerabilities & Exploitation
incidents
A Chinese state-linked actor reportedly used a BeyondTrust flaw as a zero-day, which makes the vendor’s product exposure more urgent for defenders than a standard patch-and-monitor story. Security teams using the affected software need to treat it as an active intrusion risk, not just a vulnerability disclosure.
Threat Actors & Campaigns
enforcement
Covenant Health has settled a class-action lawsuit, which makes this a legal and financial consequence of a cyber or privacy incident rather than a technical security update. For defenders, the main signal is that breach-related litigation is moving from disclosure into direct cost, so incident handling, record retention, and patient notification practices have clear downstream exposure.
Regulation & Enforcement
The FTC is acting against a phishing-style impersonation scheme that used fake FTC websites to mislead the public. For defenders, this is mainly an enforcement and fraud-prevention story: it highlights government-brand abuse that can drive credential theft, payment fraud, and other social-engineering attacks.
Regulation & Enforcement