Cyber Security Briefing Briefing — October 31, 2026
Saturday, October 31, 2026
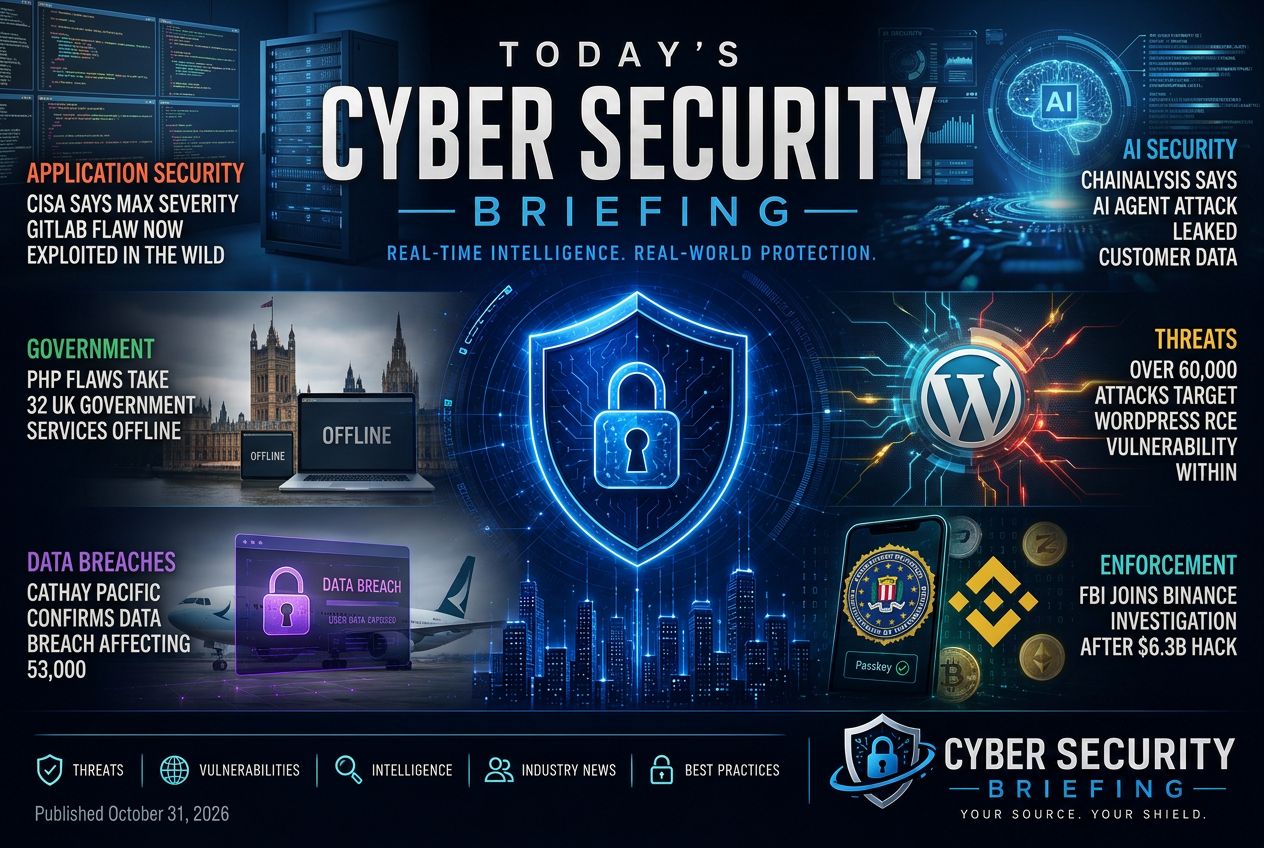
Today's briefing brings you 20 stories across application security, ai security, government and data breaches from the global cybersecurity industry. Leading today: CISA says max severity GitLab flaw now exploited in the wild - BleepingComputer.
application-security
CISA has warned that a maximum-severity GitLab vulnerability is now being used in active attacks. For defenders, this raises the priority on patching, exposure checking, and reviewing GitLab instances for signs of compromise.
Vulnerabilities & Exploitation
This reports active exploitation against a WordPress remote code execution flaw, which moves it from a disclosure item to an immediate defender priority. The practical issue for operators is exposure across any internet-facing WordPress estate that has not been patched or hardened against attack traffic.
Vulnerabilities & Exploitation
A CISA official is criticizing a company for disclosing a PHP vulnerability before defenders had enough time to prepare. The immediate issue for defenders is exposure management: whether the bug is already in their environment, whether it can be exploited before patching is widespread, and how quickly they can validate and remediate affected systems.
Vulnerabilities & Exploitation
A critical flaw in Drupal Commerce could let attackers manipulate checkout pricing and obtain goods for far less than intended. For defenders, the immediate issue is exposure in e-commerce sites running the affected platform, with priority on patching and checking for any abuse of order or pricing logic.
Vulnerabilities & Exploitation
ai-security
Chainalysis says an AI agent attack exposed customer data, which makes this a defender-facing incident rather than a general AI story. For security teams, the issue is exposure of customer information through an AI workflow and the need to review how agents are authenticated, scoped, and monitored.
AI Security
The story points to a defense contractor exposing a secure Pentagon environment to a personal AI agent. For defenders, the issue is access control and data handling: unauthorized tooling inside sensitive government systems can create exposure even without a classic breach.
AI Security
Microsoft says an AI-driven nation-state campaign used ARTEX to enable a supply-chain compromise. For defenders, the issue is exposure in trusted software delivery paths and the need to harden identity, cloud, and vendor access that can be abused to move laterally through downstream customers.
Identity, Cloud & Software Supply Chain
Japan is asking Anthropic and OpenAI for broader access to their cybersecurity-focused models. For defenders, that points to a government trying to widen access to AI tools for security work, which could affect how public-sector teams investigate threats and build defenses.
Critical Infrastructure & OT
government
A PHP-related flaw has apparently taken a set of UK government services offline. For defenders, the immediate issue is service availability in public-sector systems and the likelihood that exposed software weaknesses can create operational disruption even without a confirmed breach.
Regulation & Enforcement
data-breaches
Cathay Pacific says a breach exposed passenger details connected to a large set of bookings. The security issue affects airline customer records and creates a privacy and fraud risk for affected travelers, along with notification and response obligations for the company.
Breaches & incidents
Moldova has opened a criminal investigation after a major breach of government data. For defenders, the issue is both exposure of public-sector records and the likelihood that other government systems will face tighter scrutiny and response requirements.
Breaches & incidents
The reported breach involves two major Canadian law firms and points to risk around sensitive client and deal data held by legal service providers. For defenders, this is a reminder that law firms remain high-value targets because they sit close to confidential business, litigation, and transaction records.
Regulation & Enforcement
Archive of Our Own says it suffered a security incident and that user data may have been compromised. The main defender concern is exposure of user records and the need to verify what was accessed, notify affected users, and tighten account and incident-response controls.
Breaches & incidents
The story appears to be about a cyberattack-related class action against a law firm being dropped. For defenders, the practical issue is not a new technical threat but the legal and operational consequence of a prior incident, including how breach litigation can extend the impact of an attack after the event itself.
Breaches & incidents
enforcement
FBI involvement raises this from a routine market headline to an enforcement and incident-response story. For defenders, it signals a large-scale compromise with likely cross-border follow-up, and it may prompt exchanges and custodians to review account controls, incident reporting, and asset-tracing procedures.
Breaches & incidents
India’s central bank is pressing banks to prove they have met cybersecurity requirements after recent hacks. The practical effect is higher compliance pressure on banks and more scrutiny for defenders who need to show that controls are not just in place but working.
Regulation & Enforcement
endpoint
A compromised extension in the Cursor marketplace was used to drop an attacker SSH key and establish persistence on developer systems. That makes this a software supply chain and identity-access issue for teams that trust marketplace add-ons in their build and coding workflows.
Vulnerabilities & Exploitation
The piece appears to describe an APT campaign using NetamLoader against Windows 10 systems used by Asian government targets. For defenders, the important point is the exposure of government endpoints to malware delivery and follow-on intrusion, which raises priority for endpoint hardening, detection, and incident response.
Threat Actors & Campaigns
cryptography
Iron Fish says its privacy-focused blockchain has an inflation vulnerability and that support is being wound down. For defenders and operators, this is mainly a software and network integrity issue: systems connected to the chain need to assess exposure, stop relying on remaining support, and follow any migration or mitigation guidance from the project or exchanges.
Vulnerabilities & Exploitation
email-security
Ukraine’s communications authorities say they have identified a large-scale email-based attack in which attackers are sending messages that appear to come from DTEK. The immediate defender concern is impersonation and phishing against a major energy brand, which can spread malicious emails, erode trust, and force mailbox and brand-protection responses across the sector.
Breaches & incidents