Cyber Security Briefing Briefing — November 1, 2026
Sunday, November 1, 2026
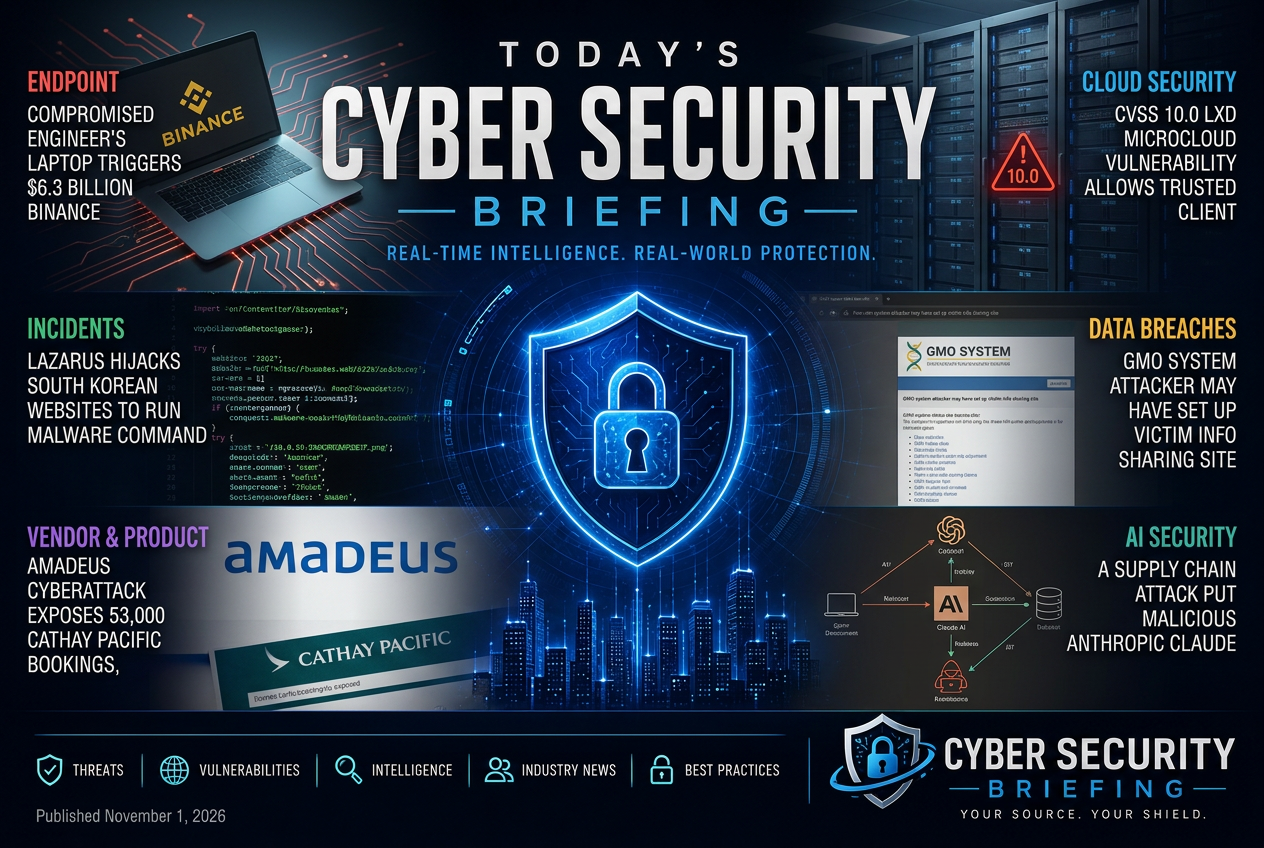
Today's briefing brings you 14 stories across endpoint, cloud security, incidents and data breaches from the global cybersecurity industry. Leading today: Compromised Engineer’s Laptop Triggers $6.3 Billion Binance Cyber Heist; Exchange Freezes $3B and Pledges Full Reimbursal - Pragativadi.
endpoint
This appears to describe a major crypto exchange incident tied to a compromised employee device and a large-scale loss that affected customer funds and the exchange’s response. For defenders, the immediate issue is endpoint compromise on privileged staff systems and the need for tighter access controls, wallet safeguards, and incident response around exchange operations.
Vulnerabilities & Exploitation
A hidden SMS message that can crash or disable Android devices matters because it turns an ordinary messaging path into a denial-of-service risk for endpoints. Defenders should treat it as an Android stability and patching issue, especially for fleets that rely on mobile devices for work access.
Vulnerabilities & Exploitation
cloud-security
A CVSS 10.0 flaw in LXD MicroCloud lets an attacker impersonate a trusted client. For defenders, the immediate issue is identity and access trust inside cloud management components, where a single weakness can undermine authentication and expose managed environments.
Vulnerabilities & Exploitation
incidents
Lazarus is reported to have abused South Korean websites as part of malware command infrastructure. For defenders, the issue is not just the intrusion path but the reuse of legitimate web properties to hide command-and-control activity, which raises detection and takedown priorities for site operators and incident responders.
Threat Actors & Campaigns
data-breaches
The report suggests the GMO intrusion may have been followed by a site set up to share victim information, which points to post-breach data handling as well as the initial incident. For defenders, the immediate concern is exposure of victim data and the possibility that attackers are using a public-facing channel to amplify impact beyond the original compromise.
Breaches & incidents
A reported attack on Amadeus appears to have exposed airline booking data tied to Cathay Pacific and affected other carriers that use the platform. The defender concern is exposure of passenger and reservation records through a shared travel-industry service provider, which raises third-party risk and data-handling obligations for affected airlines.
Breaches & incidents
Warhorse says it will notify people directly affected after a cyberattack, which indicates a confirmed security incident with possible exposure of personal or account data. For defenders, the main questions are what data was touched, whether credentials or internal systems were involved, and how the company will scope notification and containment.
Breaches & incidents
ai-security
Malicious browser extensions tied to Anthropic Claude were reportedly distributed through a supply-chain compromise and installed on many developer devices. The defender impact is exposure of software development environments, potential credential theft, and the need to audit extension provenance and access to AI tooling.
Identity, Cloud & Software Supply Chain
The piece appears to describe a vulnerability in PHP that was present for years and was surfaced with the help of AI. For defenders, the main issue is exposure in a widely used language runtime and the need to review patching, code paths, and any applications that may inherit the flaw.
Vulnerabilities & Exploitation
The piece appears to tie AI-enabled hacking activity in Japan to a government move toward more preemptive surveillance. For defenders, the main issue is the shift in operational exposure and state response, especially if organizations handling sensitive data or critical systems face more monitoring and pressure to harden against AI-assisted intrusions.
Vulnerabilities & Exploitation
Chainalysis says it suffered a data breach tied to offensive agentic techniques, which puts the company in the same risk category it helps other organizations assess. The immediate defender takeaway is exposure of internal data and the possibility that agentic AI techniques can be used to widen intrusion impact or speed attacker operations.
Ransomware & Extortion
government
MPCERT has issued a security advisory to Madhya Pradesh government departments after the LockBit ransomware case. The practical impact is a wider alert posture for state systems, with attention on ransomware exposure, response coordination, and any follow-on compromise of government networks.
Vulnerabilities & Exploitation
critical-infrastructure
Intersect is warning Cardano operators to patch a critical Linux flaw, which makes this an operational exposure issue rather than a market story. The immediate question for defenders is whether any Cardano infrastructure depends on affected Linux systems and can be remediated before attackers use the weakness.
Vulnerabilities & Exploitation
application-security
Mozilla’s security advisory for Firefox 159 is a routine patch notice, but it still matters because it tells defenders which browser flaws were fixed and whether any of them need faster rollout. For security teams, the practical question is exposure: whether managed Firefox deployments are current and whether any of the listed issues overlap with broader application-security risk.
Vulnerabilities & Exploitation