Cyber Security Briefing Briefing — November 2, 2026
Monday, November 2, 2026
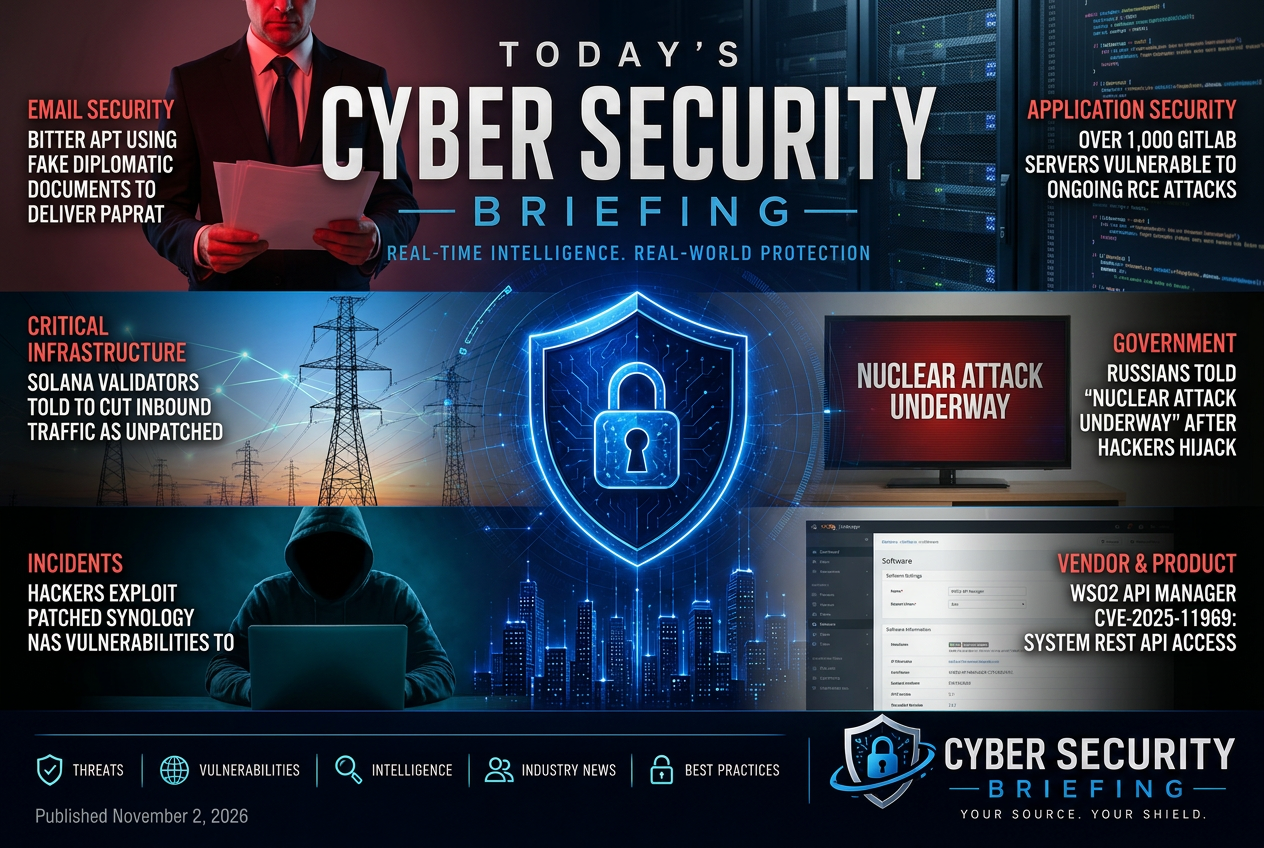
Today's briefing brings you 26 stories across email security, application security, critical infrastructure and government from the global cybersecurity industry. Leading today: BITTER APT Using Fake Diplomatic Documents to Deliver PapRAT Spyware - Hackread.
email-security
This report says BITTER APT is using fake diplomatic documents to deliver PapRAT spyware. For defenders, the immediate concern is targeted espionage against government-related targets, with email and endpoint controls needing to catch malicious attachments and document-based delivery.
Threat Actors & Campaigns
This is a phishing campaign using a fake court-themed lure to deliver LodaRAT to targeted companies. For defenders, the immediate issue is email exposure and endpoint compromise risk, with a need to watch for impersonation lures that can bypass routine user awareness controls.
Regulation & Enforcement
application-security
GitLab servers are being exposed to active remote code execution attacks, which makes this an operational security issue for any organization running affected instances. Defenders need to identify vulnerable installations quickly, patch them, and check for signs of compromise rather than treating this as a routine vulnerability notice.
Vulnerabilities & Exploitation
WSO2 API Manager has a high-severity access control flaw in its system REST API that can let an unauthorized actor carry out admin-level actions. For defenders, this is an application security issue with direct exposure at the management layer, so patching and access review should be treated as urgent.
Vulnerabilities & Exploitation
critical-infrastructure
Solana validators are being advised to reduce inbound traffic because an unpatched Linux flaw with critical severity could expose the systems they run on. The immediate concern for defenders is exposure on internet-facing validator infrastructure and the need to harden or isolate those hosts until patching is available.
Vulnerabilities & Exploitation
This reports an operational attack on supermarket refrigeration systems in Sweden, which points to a direct OT/ICS impact rather than a conventional IT breach. For defenders, the issue is exposure of building and industrial control systems that can affect food safety, store operations, and physical equipment if those systems are reachable or poorly segmented.
Critical Infrastructure & OT
The piece points to sabotage activity against Western industrial sites and water utilities, with a focus on low-skill pro-Russian actors targeting operational technology. For defenders, the immediate issues are exposure of critical infrastructure, weakly defended industrial networks, and the need to harden monitoring and response at plants and utilities.
Critical Infrastructure & OT
Ukraine restored its air alert system after a cyberattack, which makes this a public-sector resilience and continuity issue rather than a generic security headline. The immediate defender concern is whether the attack exposed weaknesses in a critical warning service and whether similar systems need hardening and redundancy.
Vulnerabilities & Exploitation
Norway has raised its national cyber risk level after a rise in successful attacks, which signals a broader threat environment for government and critical infrastructure operators. The practical effect is higher urgency on monitoring, hardening, and incident response across sectors that depend on national networks and services.
Critical Infrastructure & OT
A watchdog audit says the Federal Reserve's security program was ineffective, which puts a major U.S. financial institution's control environment under scrutiny. For defenders, the issue is not a disclosed breach but the exposure created when a core security program does not meet its own standards.
Critical Infrastructure & OT
government
Hackers appear to have used a government app to push a false nuclear attack alert, which is an incident affecting public trust in state alerting systems and civil defense communications. For defenders, the issue is not the nuclear claim itself but the exposure of a government-facing channel that can be abused to spread panic and undermine emergency response.
Vulnerabilities & Exploitation
This report ties attacks on Cisco SD-WAN Catalyst Controller systems to a known nation-state intrusion set, which matters because it points defenders toward a specific adversary profile and a likely pattern of targeting. The immediate priority is to review exposure, harden the controller environment, and look for signs of compromise across managed network infrastructure.
Threat Actors & Campaigns
incidents
This story says attackers are abusing already-patched Synology NAS flaws to push C3RB3R ransomware and encrypt files. For defenders, the issue is exposed internet-facing NAS devices that were not remediated in time, which raises the priority of patch verification and incident review on storage systems that are often overlooked.
Vulnerabilities & Exploitation
endpoint
Apple is warning German lawmakers and government staff about possible compromise of their iPhones. The story points to a targeted mobile espionage or intrusion risk affecting government users in Germany, with immediate relevance for device hardening, account protection, and incident response.
Breaches & incidents
This points to a zero-click vulnerability in Android messaging that could let an attacker trigger harm without any user interaction. For defenders, the immediate question is exposure across Android fleets and whether patching, hardening, or carrier filtering is needed to reduce the attack surface.
Regulation & Enforcement
The piece says attackers are combining a Linux vulnerability with webshell access to reach administrative control on targeted systems. For defenders, that raises the priority on patching exposed Linux hosts, hunting for webshell activity, and checking whether privilege escalation has already happened.
Vulnerabilities & Exploitation
A government cybersecurity warning about a serious TeamViewer flaw matters because remote access tools are high-value targets when they expose endpoints or admin access. Defenders should treat this as a patching and exposure-priority issue, especially where TeamViewer is used for support, remote administration, or third-party access.
Vulnerabilities & Exploitation
Lenovo fingerprint USB drives reportedly stored user data in plaintext on hidden internal SD cards, which turns a biometric accessory into a data-handling risk. Defenders should treat this as an endpoint and vendor-product issue, because it affects how authentication devices are trusted, audited, and sanitized before reuse or disposal.
Vulnerabilities & Exploitation
This piece appears to cover a PHP2Shell threat that is no longer limited to exposed web servers and may also reach internal devices. For defenders, that raises the priority of internal segmentation, device inventory, and patching or hardening where web-facing systems can pivot deeper into the network.
Vulnerabilities & Exploitation
threats
The piece points to renewed probing of a critical BeyondTrust flaw and the likelihood of broader scanning by attackers. For defenders, the immediate issue is exposure on any unpatched BeyondTrust deployments and the need to prioritize detection and remediation before opportunistic exploitation widens.
Vulnerabilities & Exploitation
data-breaches
Several airlines are investigating whether a cyber incident at Amadeus exposed customer data and affected booking operations. For defenders, the issue is both third-party exposure and service continuity: a travel platform incident can ripple into multiple carriers at once and force a broader review of supplier controls and incident response playbooks.
Breaches & incidents
financial-services
Binance says withdrawal services have been restored after a large cyberattack. For defenders, this is a reminder that attacks on crypto exchanges can quickly become an availability and account-access issue, not just a data-theft problem.
Breaches & incidents
cloud-security
ConnectWise has taken its Cloud Backup service offline after a supply chain attack. The immediate defender takeaway is exposure in a trusted managed service, with downstream customers needing to assess backup integrity, access paths, and any shared dependency risk.
Identity, Cloud & Software Supply Chain
ai-security
The report says security flaws were found in several widely used AI coding tools, including OpenAI Codex. For defenders, this points to exposure in tools developers may trust inside software workflows, so the issue is less about the tools themselves and more about what access, code, or data they can reach if misused.
Vulnerabilities & Exploitation
healthcare
This is a patient-record access issue, not a breach in the usual external-attack sense. It still matters because it suggests internal misuse of sensitive healthcare data tied to a major incident and may trigger disciplinary, compliance, and audit follow-up.
Breaches & incidents
enforcement
Ohio is receiving money from a settlement tied to General Motors and data privacy. For defenders, the practical signal is enforcement pressure around how vehicle or connected-device data is collected, retained, and shared.
Regulation & Enforcement