Cyber Security Briefing Briefing — November 4, 2026
Wednesday, November 4, 2026
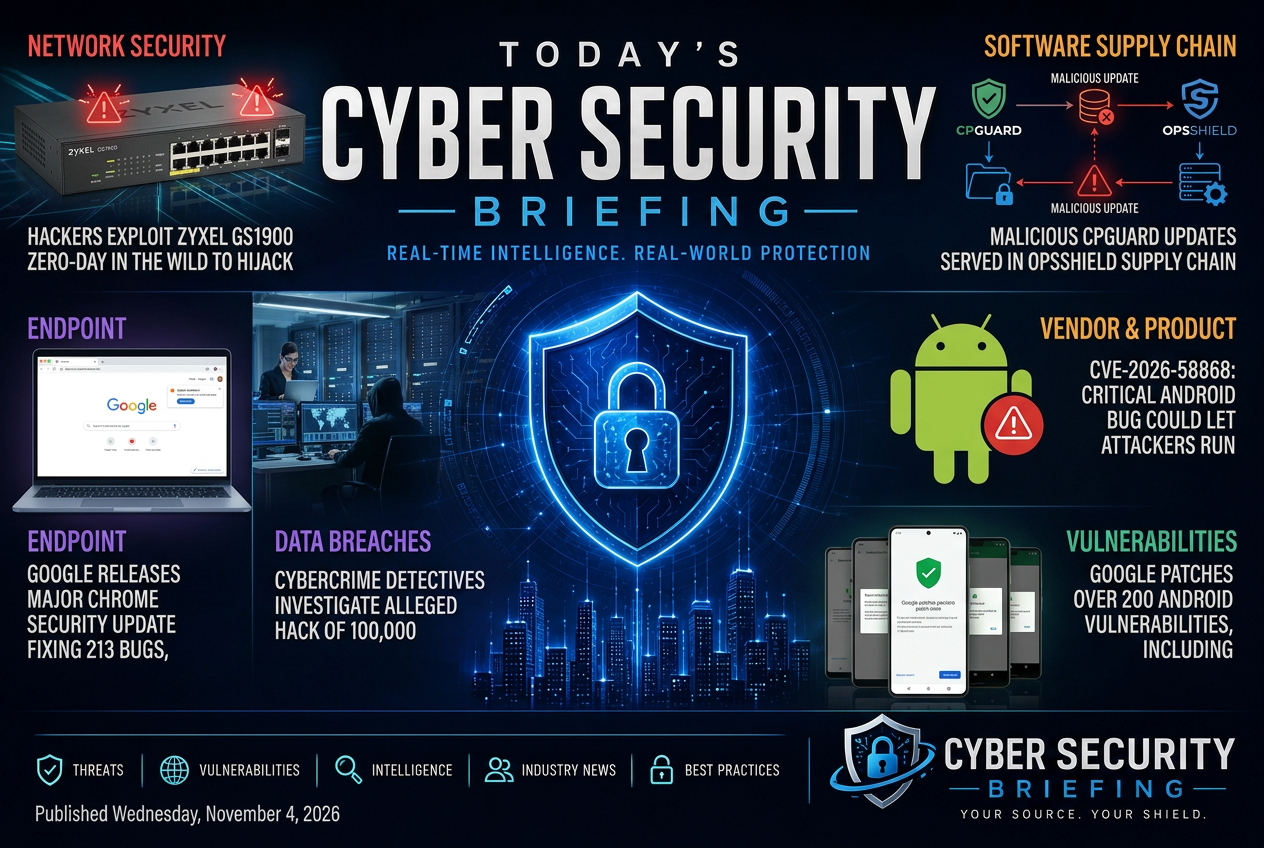
Today's briefing brings you 23 stories across network security, endpoint, software supply chain and data breaches from the global cybersecurity industry. Leading today: Hackers Exploit Zyxel GS1900 Zero-Day in the Wild to Hijack Network Switches - CyberSecurityNews.
network-security
A zero-day affecting Zyxel GS1900 switches is reportedly being used in active attacks to take control of network equipment. That matters because a compromised switch can let attackers redirect traffic, weaken segmentation, and gain a foothold inside an organization’s network.
Vulnerabilities & Exploitation
Barracuda is warning that critical vulnerabilities in its devices could let an attacker gain root-level access. For defenders, this is a patch-and-assess issue because exposed appliances can become a direct foothold into the network if they are reachable and unremediated.
Vulnerabilities & Exploitation
endpoint
Google has issued a Chrome security update that closes a large batch of bugs, including several rated critical. For defenders, this is a routine but high-priority patching event because browser flaws are a common entry point for exploitation and should be pushed quickly across managed endpoints.
Vulnerabilities & Exploitation
A critical Android vulnerability is being reported as capable of remote code execution. For defenders, the immediate issue is exposure on Android fleets and the need to confirm patch status, device coverage, and any compensating controls for managed endpoints.
Vulnerabilities & Exploitation
Google has patched a large batch of Android flaws, including critical remote code execution issues that could be triggered without user interaction. For defenders, this is a patch-priority item for Android fleets because it raises the risk of device compromise before users do anything to defend themselves.
Vulnerabilities & Exploitation
A UEFI bootkit got onto Windows systems that were already fully patched, which puts the focus on boot-chain trust rather than ordinary patch status. For defenders, the issue is exposure at a deeper layer: if firmware or boot components can be subverted, standard endpoint hardening may not be enough, and Microsoft's role becomes part of the remediation question.
Vulnerabilities & Exploitation
software-supply-chain
This appears to be a supply-chain compromise involving malicious updates pushed through software used by defenders, which shifts the risk from a single target to any environment that trusts the affected update path. Security teams should treat it as a vendor trust and patch-validation issue, with priority on identifying exposed deployments and verifying software integrity.
Identity, Cloud & Software Supply Chain
data-breaches
Police are looking into an alleged theft of Australian health records, which makes this a data-breach story with potential privacy and patient-safety consequences. For defenders, the immediate issue is exposure of sensitive personal and medical information and the possibility that the files could be reused for fraud or extortion.
Breaches & incidents
Harvard is reported to have suffered a large data breach affecting a very large user base. For defenders, the story is about exposure and incident response at a major education institution, with likely implications for account security, notification duties, and post-breach hardening.
Regulation & Enforcement
South Korea is investigating a leak of presidential flight records, which points to possible exposure of sensitive government travel and security information. For defenders, the immediate issue is containment and determining whether this was a systems compromise, insider access, or a records-handling failure.
Breaches & incidents
Ford AV, a US-based systems integrator, has reported a data breach. The immediate defender concern is exposure of customer, employee, or project information and whether the incident signals broader third-party risk for organizations that rely on integrators for AV and related systems.
Breaches & incidents
critical-infrastructure
European authorities are investigating attacks aimed at grocery refrigerators, which suggests a connected-device or building-systems issue affecting retail operations. The defender impact is exposure and continuity risk for operators, plus a signal that everyday operational equipment can become part of a broader intrusion or disruption campaign.
Regulation & Enforcement
A researcher found a vulnerability in software used in data centers. For defenders, the immediate question is exposure: which operators use the affected software, whether it sits on internet-facing management paths, and how quickly a patch or mitigation is available.
Vulnerabilities & Exploitation
government
South Korea is moving to centralize cybersecurity leadership under a single czar. For defenders, the practical issue is whether this creates clearer accountability for incident response, regulation, and coordination across government and critical sectors.
Regulation & Enforcement
The headline points to a cyberattack that exposed weaknesses in Moldova’s security posture. For defenders, the useful question is whether this was a single incident or a sign of broader gaps in detection, hardening, or incident response across public-sector systems.
Breaches & incidents
BITTER is a South Asian espionage group, and this piece says it has refreshed its malware to keep spying operations going. For defenders, the main issue is continued exposure to a known threat actor rather than a new class of attack, which still matters for detection, blocking, and hardening priorities.
Threat Actors & Campaigns
The piece is about NIS2 putting explicit cybersecurity oversight duties on company boards. For defenders, that shifts security from an IT issue to a governance obligation and gives security leaders a clearer basis to demand board-level attention, resourcing, and accountability.
Regulation & Enforcement
ai-security
This report says a jailbreak toolkit is being used against OpenAI Codex through prompt injection, with hidden adware as part of the package. Defenders should treat it as an AI-security and endpoint risk, since the issue combines model abuse with unwanted software delivery.
AI Security
A reported breach involving GitBook’s AI agent led to token revocation and forced PancakeSwap to take documentation offline. For defenders, the issue is exposure in the tooling and access layer, not just the content layer: AI-integrated publishing systems can become a path to unauthorized changes or trust erosion across dependent projects.
AI Security
CrowdStrike is reportedly buying two AI security firms, which signals more consolidation around tools for testing and securing AI systems. For defenders, the immediate effect is less about a new threat and more about where security vendors are placing product and investment priority in AI risk management.
AI Security
healthcare
A cyberattack disrupted a French blood bank site, but the report says blood products were not affected. The incident matters because a healthcare service that supports transfusion logistics was targeted, so defenders should treat it as a service-disruption event even without evidence of data loss or product compromise.
Breaches & incidents
financial-services
South Korea is using disclosure requirements to push financial firms to make their cybersecurity posture more visible. The immediate effect for defenders is added reporting pressure, which can drive budget scrutiny, board attention, and a stronger incentive to mature controls in a heavily regulated sector.
Regulation & Enforcement
threats
Chainalysis says it took Reactor and Data Solutions offline because of cyber threats. For defenders, the immediate issue is service disruption to a security product, which raises operational risk for customers even before any breach details are known.
Regulation & Enforcement