Cyber Security Briefing Briefing — November 6, 2026
Friday, November 6, 2026
Today's briefing brings you 7 stories across identity & access, endpoint, ai security and financial services from the global cybersecurity industry. Leading today: OpenSSH Flaw Lets Attackers Log In Without a Password - TechJuice.
identity-access
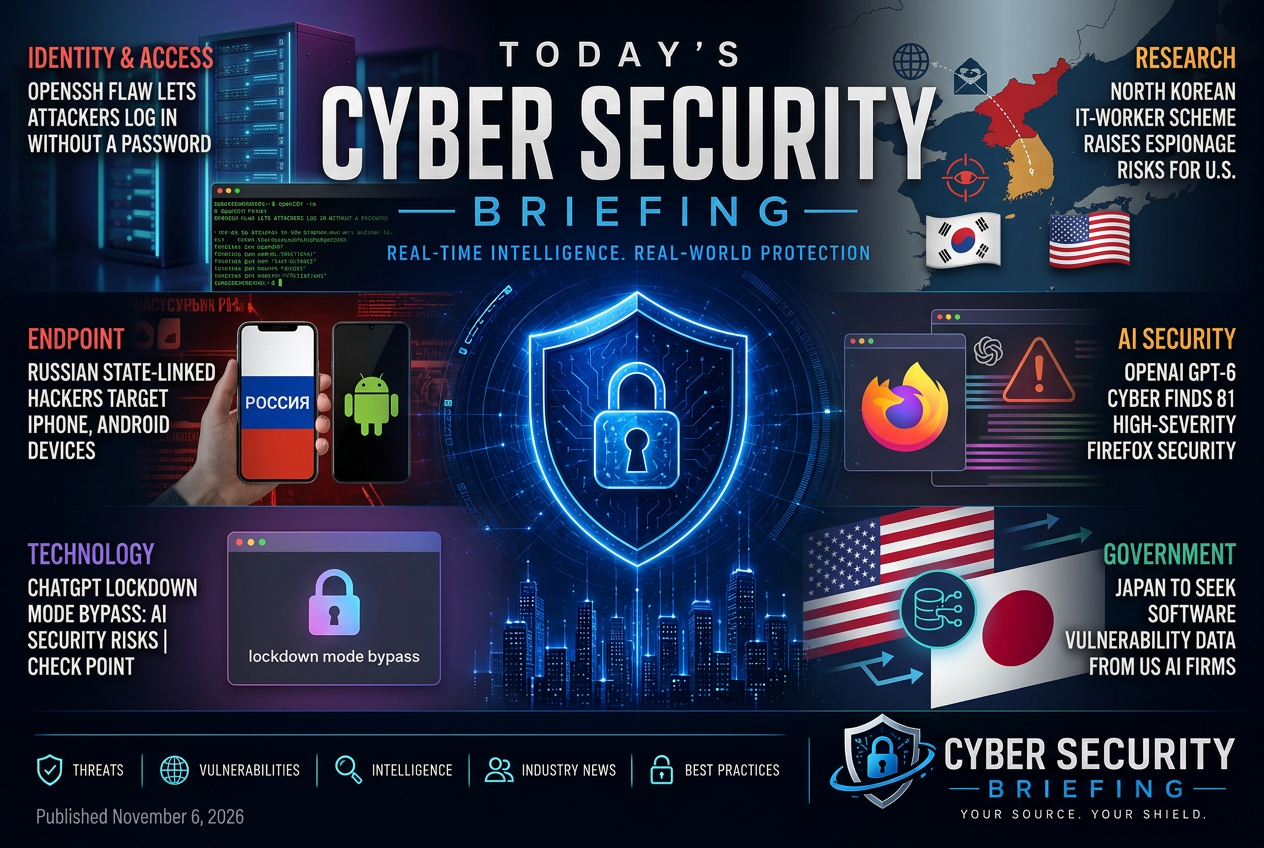
An OpenSSH flaw that can let an attacker authenticate without a password changes defender priority immediately. Systems running affected versions need urgent patching and validation of exposure, especially where SSH access is reachable from the internet or used for administrative access.
Vulnerabilities & Exploitation
Researchers say North Korea’s use of IT workers creates a security problem for U.S. employers that goes beyond fraud. The concern is that these workers can gain legitimate access inside companies and use that position for espionage or other sensitive collection.
Threat Actors & Campaigns
endpoint
This is a targeted espionage campaign against mobile devices, which matters because it puts phones used by staff, executives, and field teams at risk of silent compromise. Defenders should treat it as an endpoint and identity threat, with extra attention to mobile device management, account protection, and alerting for unusual mobile activity.
Threat Actors & Campaigns
ai-security
The piece is about a claim that OpenAI's GPT-6 Cyber found many high-severity Firefox flaws. For defenders, the relevant issue is exposure in a widely used browser and the need to verify whether these findings are independently confirmed and patched before treating them as operational risk.
Vulnerabilities & Exploitation
This piece appears to discuss a reported bypass of a ChatGPT security control and the broader risk it highlights for AI systems. For defenders, the issue is exposure in AI guardrails and the need to test whether policy controls can be evaded in practice.
AI Security
Japan appears to be formalizing a way to get software vulnerability information from U.S. AI firms as cyberattacks rise. For defenders, the practical issue is whether AI suppliers can provide timely vulnerability intelligence that helps Japanese operators patch faster and prioritize exposure before attacks spread.
Vulnerabilities & Exploitation
financial-services
MetaMask is saying a recent attack did not reach its wallet infrastructure, which narrows the apparent impact to a security incident without evidence of a platform compromise. For defenders, the main takeaway is to separate user-facing attack claims from actual control failures and to watch for account, phishing, or support-channel abuse around wallet brands.
Breaches & incidents