Cyber Security Briefing Briefing — November 9, 2026
Monday, November 9, 2026
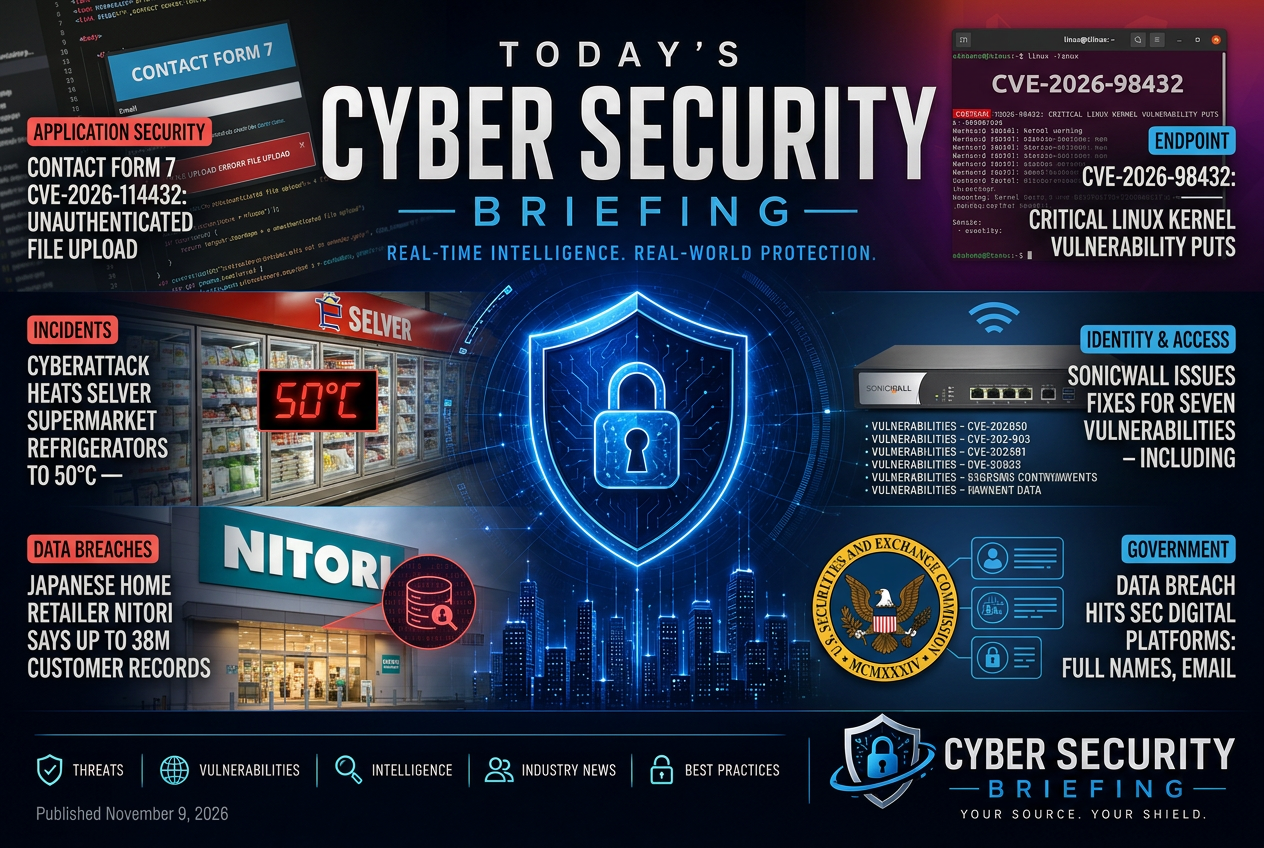
Today's briefing brings you 13 stories across application security, endpoint, incidents and identity & access from the global cybersecurity industry. Leading today: Contact Form 7 CVE-2026-114432: Unauthenticated File Upload Can Lead to RCE — Prepare Now - Rescana.
application-security
A disclosed vulnerability in Contact Form 7 could let an unauthenticated attacker upload files and potentially reach remote code execution. For defenders, this is an application-security issue that raises patching priority for WordPress sites using the plugin and may require temporary mitigations while updates are validated.
Vulnerabilities & Exploitation
endpoint
This is a report about a critical Linux kernel flaw and the risk it creates for enterprise servers. For defenders, the main issue is exposure: if the bug is real and reachable in production, kernel-level compromise could turn a routine patching task into a high-priority server hardening issue.
Vulnerabilities & Exploitation
incidents
A cyberattack disrupted a supermarket operator by overheating refrigeration equipment, which is an operational incident with direct business and public-safety impact. Defenders should read this as an example of OT exposure in retail, where attacks can quickly affect physical systems and supply chain integrity.
Breaches & incidents
This reports a cyber campaign aimed at a European telecom provider and multiple hosted organizations. For defenders, the immediate issue is exposure across shared infrastructure and hosted tenants, which raises the priority of monitoring, segmentation, and incident response across the affected environment.
Vulnerabilities & Exploitation
identity-access
SonicWall has patched seven flaws in its products, including an SSL-VPN issue that can let an attacker get around multi-factor authentication. For defenders, the immediate priority is to check exposure on internet-facing SonicWall VPN appliances, apply the fixes, and review access logs for signs of unauthorized access.
Vulnerabilities & Exploitation
data-breaches
Nitori says it may have exposed customer records affecting up to 38 million people. For defenders, this is a large retail data-breach case that raises the usual questions about what data was accessed, how far the exposure reached, and whether customer identity and fraud monitoring need to be tightened.
Breaches & incidents
The Securities and Exchange Commission’s digital platforms were breached, and the exposed records reportedly include names, email addresses, and tax identification numbers. For defenders, this is a government data exposure with identity and fraud implications, so the priority is containment, notification, credential and account review, and checking whether the intrusion touched other connected services.
Regulation & Enforcement
An Australian state agency has reported a data breach involving the Oral Health Fee For Service Scheme. The immediate defender concern is exposure of sensitive healthcare and government records, plus any follow-on obligation to notify affected people and regulators.
Breaches & incidents
SM Entertainment has reportedly suffered a data breach. For defenders, the immediate questions are what records were exposed, whether any accounts or internal systems were accessed, and whether the incident points to broader identity or perimeter weaknesses that other media and entertainment firms should check for.
Breaches & incidents
critical-infrastructure
CISA and the FBI are warning that industrial refrigeration systems are being targeted worldwide. For defenders, this is an OT security issue that can affect cold storage, food processing, and other operational environments where exposure can become an availability and safety problem.
Vulnerabilities & Exploitation
Technology
Veeam is warning that a critical Linux kernel flaw could destabilize backup appliances and interfere with recovery operations. For defenders, this is an availability and resilience issue, since backup systems that fail during an incident can slow containment and lengthen downtime.
Vulnerabilities & Exploitation
Attackers are exploiting Plex vulnerabilities to take control of exposed media servers and use them for cryptocurrency mining. For defenders, this is a reminder that internet-facing consumer-adjacent software can become an entry point for unauthorized code execution and resource theft if it is not patched and monitored.
Vulnerabilities & Exploitation
ai-security
India’s CERT-In is setting out audit guidance for AI systems, with a focus on poisoning, prompt injection, and risks from agentic AI. For defenders, this shifts AI security from an optional best practice to a formal compliance and assessment issue for organizations deploying these systems in India.
AI Security